Ai Threat Intel Analysis CLOSEDQUORUM and the Rise of Autonomous AI Malware Cisco Talos analyzes CLOSEDQUORUM, a Windows implant that delegates tactical decisions to multiple commercial LLMs instead of a conventional C2 server.
Ai Threat Intel Analysis PAYLOAD ransomware turns Active Directory into an attack tool Kaspersky’s analysis shows how PAYLOAD used trusted Active Directory Group Policy to disrupt a manufacturing environment without Windows encryption.
Ai Threat Intel Analysis Atomic macOS Stealer: How Deceptive Setup Guides Deliver AMOS Palo Alto Unit 42’s lab analysis shows how deceptive macOS setup instructions deliver AMOS, harvest sensitive data, and establish persistence.
Ai Threat Intel Analysis AWS AgentCore Harness: When Prompt Injection Reaches Credentials Unit 42’s testing shows how default AgentCore Harness tools can turn prompt injection into credential exposure, with practical controls for AWS operators.
Ai Threat Intel Analysis Japanese Ransomware Activity: The Gentlemen and Qilin Cisco Talos examines ransomware activity affecting Japan, including The Gentlemen’s intrusion workflow and Qilin’s possible use of AI-assisted tooling.
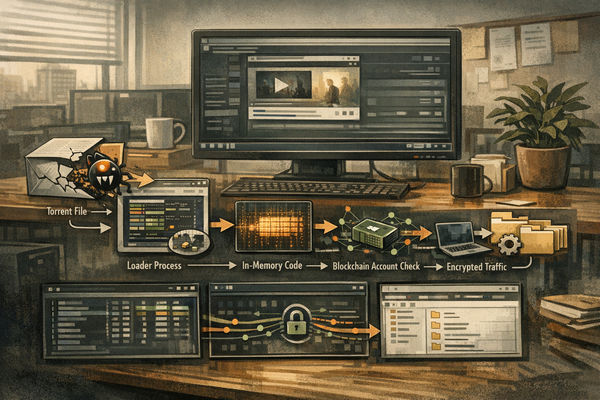
Ai Threat Intel Analysis MovieReaper: How Torrent Files Hide a Modular Trojan Securelist details MovieReaper, a multi-stage Windows Trojan distributed through compromised torrent files and using Solana to conceal its C2.
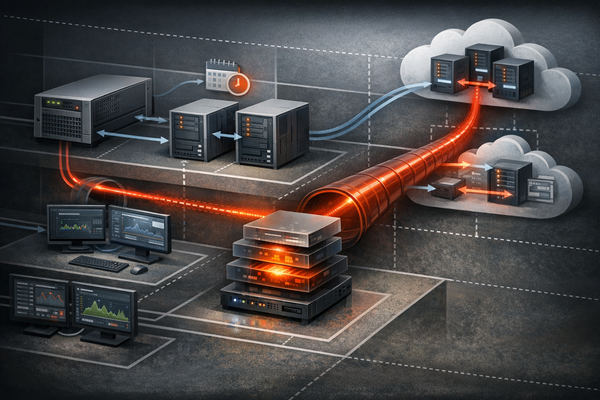
Ai Threat Intel Analysis NightEagle’s GhostContainer Campaign Targets Russian Businesses Kaspersky details NightEagle’s use of GhostContainer, Exchange servers, tunneling tools, RDP weaknesses, and Active Directory abuse.
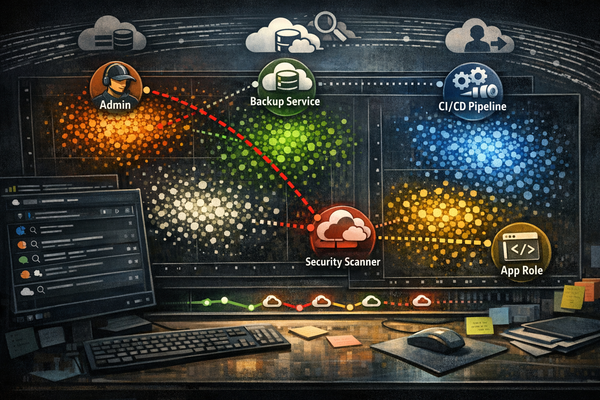
Ai Threat Intel Analysis Behavioral Mapping Brings Context to AWS Identity Detection Palo Alto Unit 42 shows how CloudTrail behavior can reveal functional identity roles and improve detection of anomalous AWS activity.
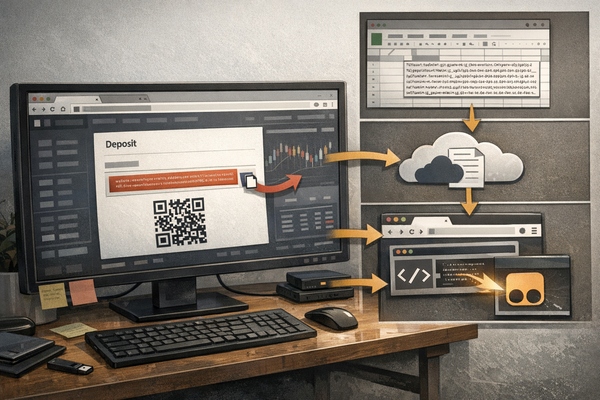
Ai Threat Intel Analysis ClickFix Turns the Browser Into a Cryptocurrency Skimmer Cisco Talos describes a ClickFix campaign that uses Google-hosted JavaScript, browser injection, and fake cryptocurrency bonuses to redirect deposits.
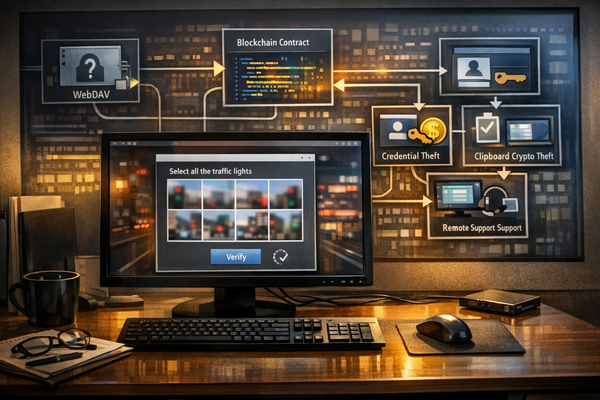
Ai Threat Intel Analysis ClearFake WebDAV Chain Delivers Stealers and Remote Access Cisco Talos details a ClearFake delivery chain using WebDAV, blockchain-hosted JavaScript, Amatera, ZigCryptoStealer, and NetSupport Manager.
Ai Threat Intel Analysis September 2026 Microsoft Patch Tuesday: What to Prioritize Cisco Talos identifies two exploited flaws and a broad set of high-priority Microsoft vulnerabilities, with Snort coverage for selected attack attempts.
Ai Threat Intel Analysis Cisco FMC Exploitation Puts Security Management at Risk Cisco Talos reports active exploitation of two Secure Firewall Management Center flaws, with observed activity ranging from credential theft to ransomware preparation.
Ai Threat Intel Analysis SPIFFE/SPIRE: When Node Compromise Breaks Workload Identity Palo Alto Unit 42 shows how root access to a Kubernetes node can undermine SPIFFE/SPIRE workload identity and expose co-located service credentials.
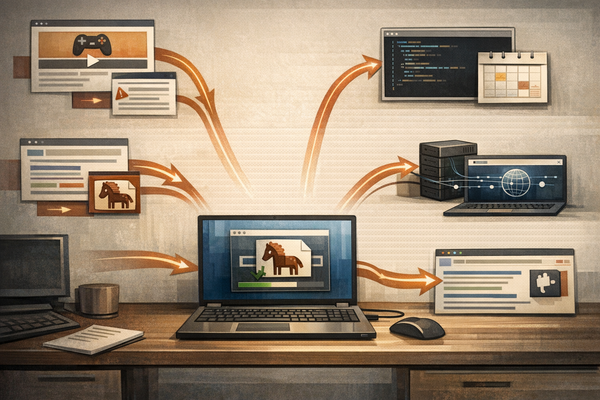
Ai Threat Intel Analysis How Pay-Per-Install Malware Hides Behind Trusted Downloads Palo Alto Unit 42 traced a pay-per-install campaign that used gaming videos, SEO poisoning and a shared loader to deliver multiple malware families.
Ai Threat Intel Analysis How Agentic AI Is Reshaping the Threat Landscape Google Threat Intelligence and Mandiant report that adversaries are combining AI agents, stolen credentials, supply-chain abuse, and cloud hijacking.
Ai Threat Intel Analysis How Adversary Engagement Improves Threat Intelligence Cisco Talos explains how persona-based dark-web research, patience, and evidence-based analysis turn fragmented criminal activity into usable intelligence.
Ai Threat Intel Analysis How AI Agents Compressed an Enterprise Intrusion Unit 42 details an AI-assisted enterprise intrusion that automated reconnaissance, credential theft, pipeline abuse and cloud takeover.
Ai Threat Intel Analysis AI-Enabled Intrusions Target Latin American Organizations Unit 42 details two Latin American intrusion clusters using LLM-assisted workflows, SOCKS5 tooling, data theft, and exposed infrastructure.
Ai Threat Intel Analysis Toy Ghouls Deploys Windows Backdoors Over MQTT and Matrix Kaspersky details Toy Ghouls backdoors that use HiveMQ MQTT and Matrix-based Element for Windows persistence, telemetry, and command execution.
Ai Threat Intel Analysis ValleyRAT Campaign Hides a Backdoor in Fake Adware Securelist details how a deceptive adware installer sideloads ValleyRAT, disables Windows Defender, establishes persistence, and collects sensitive host data.
Ai Threat Intel Analysis Mirage Kitten Targets Developers With Cross-Platform RATs Securelist details Mirage Kitten campaigns using NodeRabbit and PollCat backdoors in trojanized coding assessments aimed at aviation and FinTech.
Ai Threat Intel Analysis BREEZE COMET: How Brazil’s Payment Systems Were Targeted Google Threat Intelligence and Mandiant detail BREEZE COMET’s intrusion path into Brazilian financial environments and outline defensive priorities.
Ai Threat Intel Analysis Spring Ring: Teams Vishing Turns Help Desks Into Attack Paths Unit 42 details Spring Ring, a Microsoft Teams voice-phishing operation that used fake IT staff, RMM tools and malware to target enterprise identities.
Ai Threat Intel Analysis How Obfuscated JavaScript Powers Modern Phishing Kits Cisco Talos explains how phishing kits hide JavaScript behavior and how defenders can safely recover redirects, payloads, and credential-theft logic.
Ai Threat Intel Analysis ICS Threats in Q2 2026: What Defenders Should Know Securelist’s Q2 2026 telemetry shows declining overall ICS detections but rising email, ransomware, worm, and malicious-document activity.