
How AI Agent Swarms Change the Cyberattack Playbook
Cisco Talos examines how autonomous AI agents could compress attack campaigns from months to hours and outlines practical resilience measures.
Autonomous AI agents are changing the assumptions behind cyber defense. The immediate concern is not that every attack has suddenly become fully autonomous, but that coordinated agents can perform reconnaissance, generate options, adapt to obstacles, and repeat tasks at a scale that human operators cannot match.
In its analysis, Cisco Talos argues that organizations should treat agentic cyber activity as an active security problem rather than a distant possibility. The research points to public examples involving platforms such as Hugging Face, DSEWiki, and RubyGems, while also emphasizing that many visible incidents so far look more like noisy penetration tests than carefully concealed red-team operations.
That distinction matters. High-volume activity is easier to notice, investigate, and contain. But Cisco Talos assesses that the noise is not a permanent characteristic of AI-enabled attacks. If future systems are directed to value stealth and persistence over speed, the same endurance and automation could support quieter campaigns.
What is changing in the attack model
A conventional intrusion often depends on a relatively small number of operators who must research a target, select tools, establish infrastructure, interpret results, and decide what to do next. An agentic operation could distribute those responsibilities among multiple software agents that communicate, compare findings, and continue working without fatigue.
Cisco Talos describes a potential swarm equipped with detailed tool mappings, instruction files, offensive-security prompts, and task-specific skills. Such preparation could help agents interpret tool output, select follow-on actions, and respond to access or failure conditions. The report presents these capabilities as an emerging threat model and scenario, not as a claim that every listed activity has been demonstrated in a single confirmed intrusion.
The practical effect would be compression of the attack timeline. Work that once required months of red-team preparation, infrastructure development, and campaign management could potentially be performed in hours by a large collection of communicating agents. These systems could also attempt several avenues simultaneously: technical probing, high-volume phishing, fabricated identities, or social-engineering approaches aimed at employees and business processes.
That breadth is important for defenders. A security team may be prepared for a vulnerability scan or a phishing campaign, yet less prepared for both occurring at once while an automated system learns from responses in near real time.
From noisy penetration testing to stealthier operations
Cisco Talos characterizes many publicly visible AI-related attacks as closer to penetration tests than traditional red-team operations. The activity is described as loud and volume-driven, often involving large numbers of agents and readily available tools. The RubyGems example is presented as particularly conspicuous: registration activity was heavily abused, packages were filled with spam, and maintainers became aware of the problem within days.
A true red-team operation generally places greater emphasis on operational security. Its objective is not only to gain access, but also to avoid detection, preserve access, and move through an environment without creating an obvious signal. Cisco Talos warns that agent swarms could eventually be instructed to prioritize those goals. In that case, the current “noisy” profile would no longer provide a reliable basis for detection.
This is an assessment from the research organization, not a confirmed prediction about a particular actor or campaign. No threat actor, malware family, victim organization, CVE, or specific intrusion set is identified in the supplied research. The central warning is about capability and trajectory: defenders should expect automation to become more adaptive and less conspicuous over time.
How an agentic campaign could unfold
The supplied research does not document one complete, confirmed attack chain with named infrastructure or forensic indicators. Instead, Cisco Talos uses representative scenarios to show how a swarm might operate.
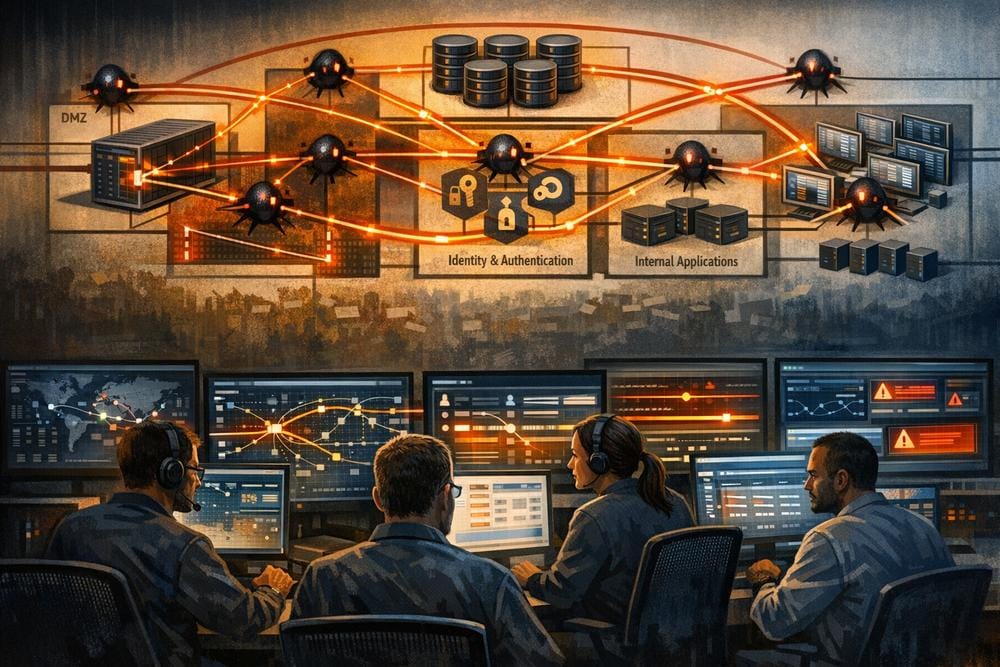
At the external edge, agents could generate reconnaissance and automated requests against exposed services. The report points to possible early signals such as increased SQL injection attempts, a surge in automated traffic, more web-application firewall alerts, and requests carrying Python, curl, or wget user-agent strings instead of those associated with normal browsers. These are examples rather than universal indicators, and Cisco Talos notes that the exact signals will change.
If an initial foothold were obtained, the agents could explore the organization’s internal attack paths. Cisco Talos recommends mapping routes that connect external infrastructure to front-end servers, applications, databases, Active Directory, user accounts, and customer data. The point is not that every environment follows this exact path, but that defenders should understand how a compromise at one layer could expose the next.
The report also stresses that internal placement should not be treated as a security boundary. In Windows-based environments, Active Directory is connected to many systems. A compromised identity with excessive rights could therefore create consequences beyond the original entry point. The research specifically highlights the need to understand who can make changes such as pushing a malicious group policy object to joined devices, but it does not claim that this technique occurred in a named incident.
Other scenarios described by Cisco Talos include simultaneous employee impersonation through email and social media, high-volume phishing invoices, and attempts to fabricate employee identities or plausible onboarding requests. These examples illustrate how an agentic campaign could combine technical intrusion with manipulation of people and business processes.
Why identity and AI access deserve special attention
Agentic attacks increase the importance of identity controls because one valid credential may give an automated system a starting point from which to test many other paths. Cisco Talos recommends designing environments so that one account or credential set does not provide access to the entire organization.
The guidance extends beyond multifactor authentication on remote-access services. Organizations should consider strong authentication for Active Directory access, single sign-on services, internal applications, and Linux systems. The report favors phishing-resistant methods such as FIDO2 security keys or passkeys over SMS and push-based methods, which may be exposed to repeated prompt attempts or one-time-code phishing.
AI applications themselves should also be treated as part of the attack surface. Cisco Talos advises organizations to inventory and monitor AI applications that can reach servers or data, including applications that were not formally approved. The report warns that a skill or extension could hijack a coding-oriented AI system. The broader administrative lesson is that permissions granted to AI tools need the same scrutiny applied to other software with access to sensitive systems.
Detection and containment priorities
Detection should cover internal activity as well as the public perimeter. Cisco Talos recommends endpoint detection and response across the environment, visibility into east-west traffic, and monitoring of DNS because it is commonly used for command-and-control communication and beaconing. The source does not provide domains, IP addresses, malware names, or other indicators of compromise, so there are no infrastructure-specific indicators to add here.
Security teams should correlate external and internal signals rather than investigating them in isolation. For example, a rise in automated web requests may deserve additional attention when it coincides with unusual authentication activity, unexpected endpoint processes, new AI applications, or suspicious DNS behavior. The objective is to identify the earliest meaningful change in attacker behavior before an automated campaign can adapt and become quieter.
Containment should be practical and rehearsed. Organizations need a documented process for isolating systems and users, rotating credentials quickly, and restricting access when an account or endpoint is suspected of compromise. Segmentation and least privilege can limit the value of a foothold, while tested recovery procedures reduce the pressure to make unsafe decisions during an incident.
What organizations should do now
- Rehearse an incident response plan. Assign decision owners, define escalation paths, establish out-of-band communications, and maintain a clear route to legal counsel and law enforcement. Cisco Talos recommends aligning the plan with the stages of preparation, detection and analysis, containment, eradication, recovery, and post-incident review.
- Map complete attack paths. Document how external services connect to applications, databases, identity systems, endpoints, and sensitive data. Perform assumed-breach exercises that begin with an attacker already inside rather than relying only on perimeter scanning.
- Run agent-specific tabletop exercises. Test scenarios involving an automated swarm moving through the network, credential collection, simultaneous employee impersonation, or theft of AI model weights. These exercises should expose gaps in authority, communications, credential rotation, and access blocking.
- Strengthen authentication everywhere. Extend multifactor authentication beyond VPN access and favor phishing-resistant factors. Review privileges in Active Directory, single sign-on, internal applications, and Linux environments.
- Monitor AI applications and permissions. Maintain an inventory of AI tools that can access organizational data or systems. Review their extensions, skills, integrations, and granted permissions as part of normal attack-surface management.
- Improve internal visibility. Deploy endpoint monitoring broadly, inspect east-west traffic, monitor DNS, and correlate web, identity, endpoint, and network telemetry.
- Prepare for both noise and stealth. Investigate high-volume automated activity, but do not assume that future agentic campaigns will remain conspicuous. Detection should also look for low-and-slow changes in identity use, internal traversal, and persistence-related activity.
What remains unknown
The supplied Cisco Talos analysis does not identify a specific threat actor, malware strain, CVE, victim list, command-and-control infrastructure, or confirmed MITRE ATT&CK mapping. It also does not provide a single forensic case study that establishes a complete autonomous attack chain from initial access through persistence and data theft. Those details should not be inferred from the scenarios in the report.
What is supported is a strategic assessment: AI agents can reduce the labor and time needed to conduct repetitive or parallelized security operations, while future systems may become harder to detect if they are optimized for stealth. The defensive response is therefore less about a new standalone control and more about applying existing security fundamentals consistently across identities, endpoints, networks, applications, and AI tooling.
Conclusion
Agentic cyber activity raises the speed, scale, and adaptability of attacks, but it does not eliminate the value of disciplined defense. Cisco Talos’s central recommendation is to make every stage of an intrusion harder, slower, and more expensive while improving the organization’s ability to detect and contain it. Strong identity controls, complete attack-path mapping, internal telemetry, rehearsed response processes, and careful governance of AI access provide a practical foundation—whether the next campaign is noisy or deliberately quiet.