
MacSync on macOS: Stealer Gains a Persistent Backdoor
Securelist details a redesigned MacSync campaign that targets macOS developers and cryptocurrency users with binary loaders, data theft, and a backdoor.
MacSync has evolved from a relatively straightforward macOS information stealer into a more capable intrusion platform. In its analysis, Securelist describes a newly observed version that combines credential and cryptocurrency-data theft with a persistent backdoor, while replacing earlier script-heavy delivery methods with compiled loaders and executable payloads.
The campaign is particularly relevant to developers, cryptocurrency users, and other people who routinely store valuable credentials, wallet information, cloud configuration, and source-control data on a Mac. Securelist says the malware is distributed as a malware-as-a-service offering, meaning the party operating a campaign can determine the initial delivery method. The research does not identify a specific victim organization or provide evidence of a single, confirmed intrusion set behind every observed sample.
What Securelist observed
MacSync was initially advertised under the name Mac.c in 2025, according to Securelist, and was later renamed by its operators. Earlier versions were implemented primarily as AppleScripts and reportedly shared similarities with the AMOS stealer family. The newer sample examined by the researchers instead uses binary droppers and loaders, with the principal malicious modules written in Swift and Objective-C.
Securelist observed the latest infection chain in September 2026. The campaign used malicious DMG images and fake applications. One example impersonated a nonexistent cryptocurrency wallet called Toria. The associated operators promoted the supposed application through a dedicated website and social-media channels, including X and Telegram, according to the report.
The researchers also note that MacSync has appeared disguised as free or cracked software, new applications, and payloads delivered through social-engineering or ClickFix-style activity. Those delivery methods are part of the broader family’s observed behavior; the detailed chain in this report begins with a malicious application inside a disk image.
How the infection chain works
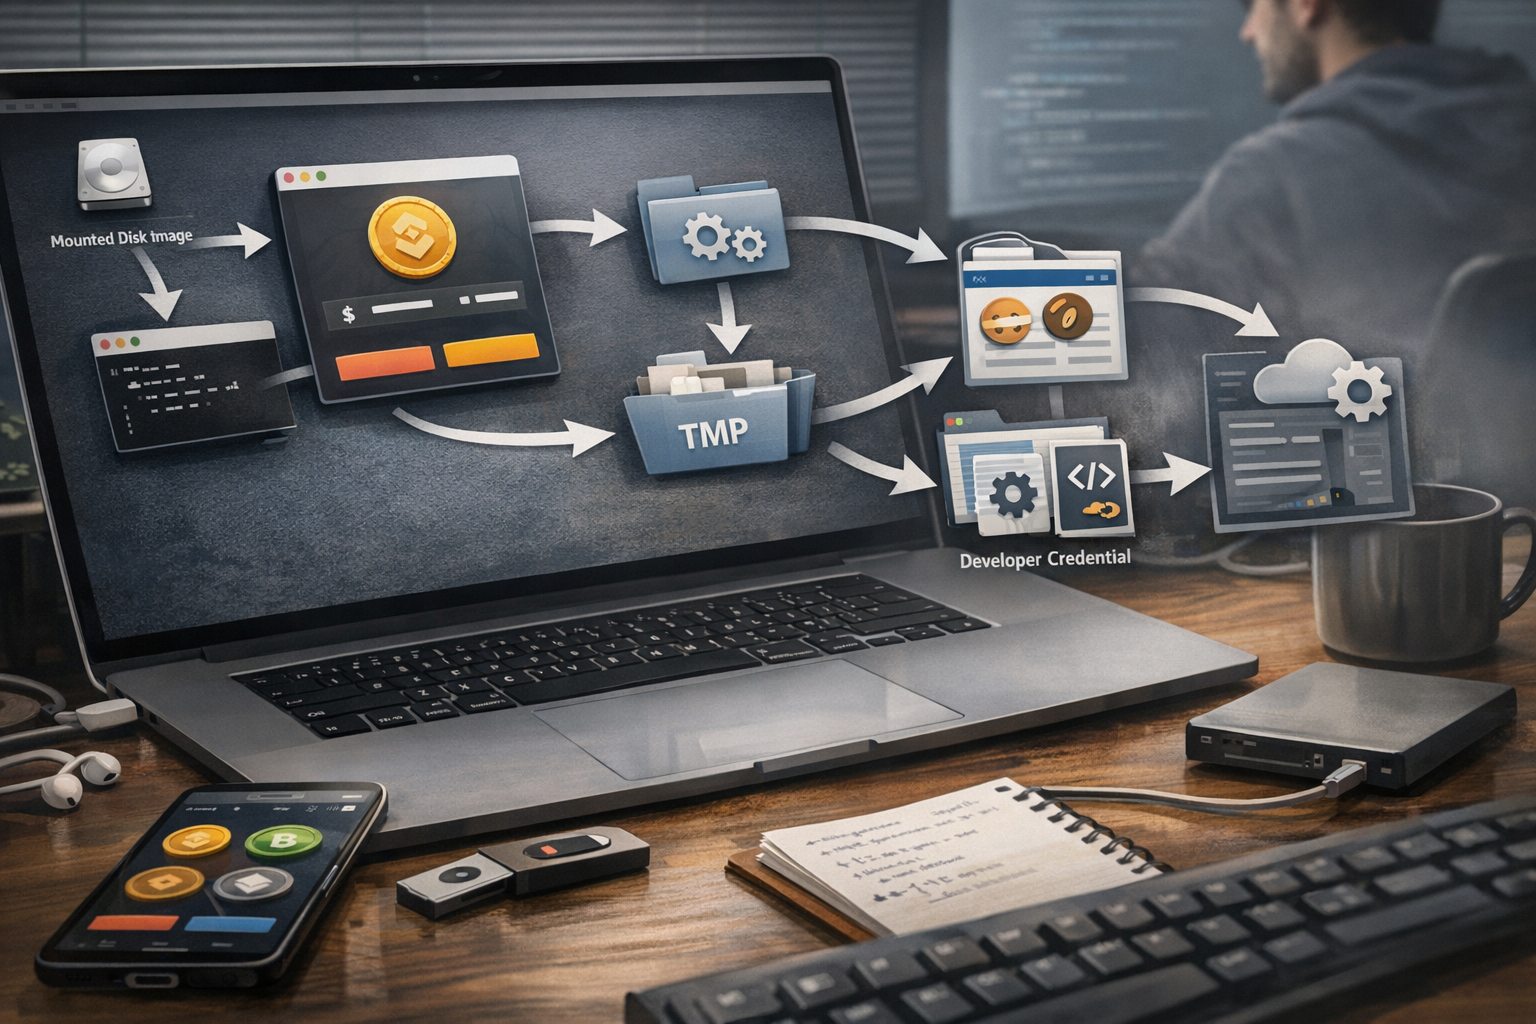
The analyzed chain starts when a user opens an application from a malicious DMG. The application checks whether macOS has assigned the bundle a quarantine attribute. If present, it removes the extended attributes before continuing. The loader then extracts an encrypted URL from data appended to the binary, decrypts it, and retrieves the next stage.
Securelist identified more than one delivery variation within a campaign built around the same fake application. In one version, a compiled JavaScript for Automation script decoded a shell script and passed it directly to an interpreter. In the more complex chain, the script appeared later, after multiple binary stages.
One notable variation used Apple’s iCloud infrastructure as an intermediate delivery point. The loader retrieved a publicly accessible iCloud calendar. The calendar was not itself a normal command channel: the downloader fed its contents line by line to a Z shell process, with the malicious instructions appearing after the calendar’s DESCRIPTION: field. Those instructions downloaded a compressed application archive, removed its quarantine attributes, applied an ad-hoc signature, and executed it.
The use of a legitimate cloud service complicates simple infrastructure-based blocking. It also means that a connection to an Apple-hosted service is not, on its own, proof of compromise. Defenders should instead examine the surrounding process chain, including an untrusted application launching shell activity, removal of quarantine metadata, and execution of an unsigned or ad-hoc-signed bundle.
The downloaded application acted as a dropper. It unpacked an encrypted executable into a randomly named path under /tmp. A subsequent dropper used anti-debugging measures, including checks associated with virtualization and the use of ptrace with PT_DENY_ATTACH, according to Securelist.
A later script downloaded another encrypted payload from command-and-control infrastructure and executed it in memory. At this stage, the malware retrieved the infostealer, the backdoor, and a utility used to generate encryption keys and decrypt additional files. Securelist says the delivery process used an elliptic-curve Diffie-Hellman exchange based on Curve25519, followed by authenticated encryption. The utility also cleared buffers containing keys and data after use, a behavior the researchers assess as intended to hinder forensic collection and dynamic analysis.
Across the chain, temporary files were placed in /tmp, and lock files were used to prevent repeated execution. Modules removed temporary files and logs after completing tasks. These characteristics provide useful behavioral signals even when file-based indicators change.
Information targeted by the stealer
The infostealer is packaged as a macOS application whose main executable is written in Swift. Securelist says it prompts the user for an administrator password and changes the appearance of its prompt to resemble the application it is impersonating. After the password is entered, it displays a deceptive notification suggesting that the application is corrupted and should be moved to the Trash.
Rather than using the more commonly observed dscl utility to validate a password, the sample uses macOS Pluggable Authentication Modules, or PAM. Securelist describes this as a comparatively recent technique in macOS malware and says it was also observed in the Pam Stealer family in July 2026.
The collected information includes browser history, cookies, saved logins and passwords, Local State files, and cryptocurrency-wallet extension data. The stealer also seeks data associated with cryptocurrency wallet applications and Telegram. Other targets include the device login and password, Keychain data, installed applications, running processes, hardware and device identifiers, SSH configuration, Z shell and Bash histories, and configuration files for services and tools such as AWS, Kubernetes, and Git.
The malware stores collected information in a hidden temporary directory and compresses it into an archive before sending it to the operators. Securelist reports that stolen data is uploaded through HTTP PUT requests, in chunks of approximately 90 megabytes in the analyzed version.
The researchers also found code for a Keychain-related capability that was disabled in the samples they examined. Its apparent purpose was to alter access controls for selected browser secrets, including Chrome and Brave storage items. Securelist explicitly presents the future purpose of this feature as an assessment: the relevant helper was absent, and the observed fallback still triggered a user confirmation request. Organizations should therefore distinguish this planned or incomplete capability from functionality confirmed to be active in the analyzed samples.
The backdoor changes the risk
MacSync’s backdoor extends the incident beyond one-time theft. It is a Fat Mach-O executable written in Objective-C and can communicate with its operators over HTTP. Securelist says the backdoor checks in for commands, refreshes an expired access token, uploads files in separate requests, and reports execution status to the server.
Persistence is established through several locations. The malware creates a directory at $HOME/Library/Application Support/System, stores a backup copy and supporting files there, and disguises the backdoor as Finder. It installs a LaunchAgent named com.apple.finder.agent. It also injects commands into the user’s .ZSHRC file and into global Git pre-commit and post-checkout hooks.
A repair script checks whether the backdoor remains present, restores it from the backup if necessary, and recreates or reloads the LaunchAgent. The script also terminates several macOS notification and background-task processes to suppress notifications about the newly created LaunchAgent. On older macOS versions, Securelist says a helper can add the executable to Login Items.
The backdoor’s documented command handlers include deploying a browser extension, replacing an installed Ledger wallet with a version supplied by the server, collecting system information or selected files again, and downloading a component associated with a command called live_browser. Securelist says the purpose of that component, named sn_relay, remains unknown. Based on the command name and server messages, the researchers assess that it may support interception of browser traffic, but this is not confirmed.
What organizations should do now
Prioritize macOS telemetry. Monitor for applications launched from DMG files or user-writable locations that remove quarantine attributes, create ad-hoc signatures, invoke shells, or execute content from /tmp. Correlate these events with unusual access to browser profiles, Keychain-related processes, wallet directories, SSH files, cloud credentials, and Git configuration.
Review persistence locations. Hunt for unexpected LaunchAgents, Login Items, modifications to .ZSHRC, and changes to global Git hooks. The combination of a suspicious LaunchAgent, a hidden application-support directory, and a repair script is especially significant. Administrators should preserve relevant files and timestamps before deleting them during an investigation.
Protect developer and cryptocurrency assets. Developers should avoid cracked or unofficial software and verify downloads through trusted vendor channels. Organizations should use phishing-resistant multifactor authentication where available, rotate potentially exposed cloud, source-control, SSH, and cryptocurrency credentials, and treat a compromised developer Mac as a possible exposure of downstream repositories or signing material. Wallet recovery procedures should be followed if wallet-related data may have been accessed.
Inspect network behavior. Look for unexpected HTTP traffic from newly installed applications, repeated requests to agent-style endpoints, large outbound PUT requests, and custom headers such as X-Upload-Token. Because the campaign can use legitimate Apple-hosted infrastructure, network indicators should support—not replace—endpoint and process analysis.
Use the supplied indicators carefully. Securelist lists file hashes for loaders, droppers, scripts, the infostealer, the backdoor, and an auxiliary autorun tool. It also lists domains associated with delivery and command-and-control activity. These indicators should be imported into appropriate security tools in defanged form and validated against local telemetry; they are not a substitute for behavioral detections because the service-based delivery model can allow operators to change infrastructure.
Conclusion
Securelist’s analysis shows MacSync moving toward a modular macOS compromise that combines credential theft with durable access. The most important defensive lesson is the need to detect the full sequence: a deceptive application, quarantine removal, shell and loader activity, execution from temporary paths, theft of developer and wallet data, and persistence through LaunchAgents, shell configuration, and Git hooks.
The report does not establish that every capability observed in code was active in the field. In particular, the Keychain enhancement and possible browser-traffic interception remain incomplete or unconfirmed. Even so, the confirmed stealer and backdoor functions create a substantial risk for individuals and organizations whose Macs contain cryptocurrency assets, development credentials, or access to corporate systems.
Sources
Selected indicators
Securelist reports the following sample hashes: 26a0f7cdb9f7dc5ace9a40af825b1538, 3ded1d71a822b53b12c3b67bcaf633f5, c53d0ea45dbc622afb7f16ea3eec78bc, and fc3ba5ed282d77127efd0b0f2403531b. Defanged infrastructure listed by the researchers includes hxxps://toria[.]app/, hxxps://toria[.]apple03cloudstore[.]com/, hxxps://docsend[.]appstore[.]com[.]mx/, and hxxps://caldav[.]icloud[.]com/. These are provided for defensive investigation only.