
Citrix NetScaler Campaign Uses Web Shells and Tunneling
Google Threat Intelligence and Mandiant detail active NetScaler exploitation involving root access, disguised PHP web shells, and internal network tunneling.
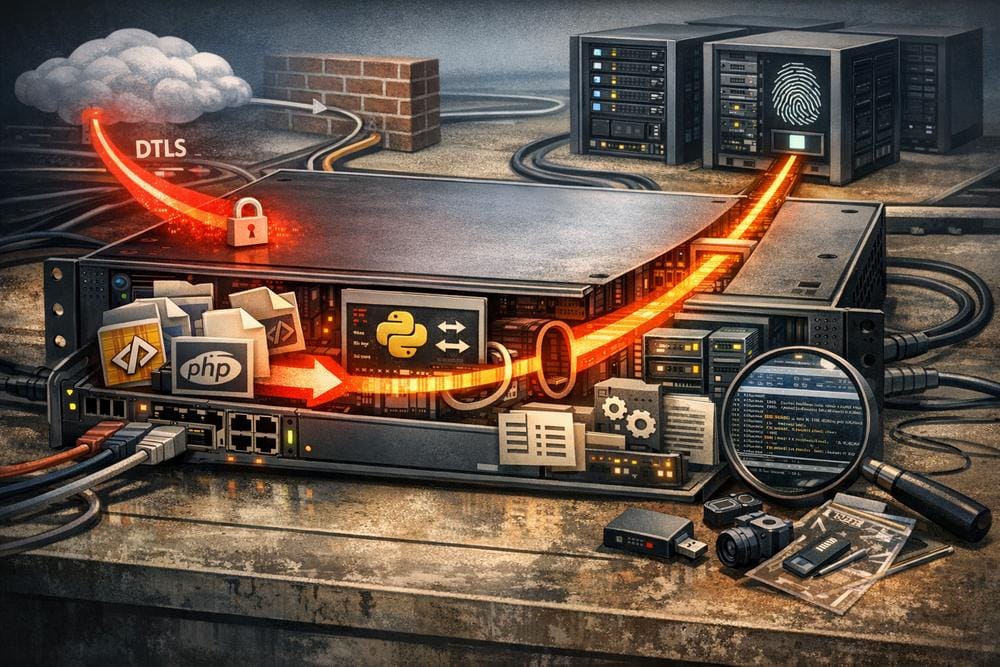
Internet-facing Citrix NetScaler appliances are being used as an entry point into organizational networks in an active exploitation campaign analyzed by Google Threat Intelligence and Mandiant. The research describes exploitation of CVE-2026-88772, a zero-day affecting NetScaler ADC and NetScaler Gateway, as well as vendor-reported exploitation of a second zero-day, CVE-2026-88771.
The observed post-compromise activity is notable because it combines appliance-level persistence with a covert route into internal systems. The toolkit includes lightweight PHP web shells, including WHIPSHOT, and a Python tunneling component called SLAPSHOT. Together, these tools can provide command execution on the appliance, relay traffic into internal networks, and support reconnaissance and credential theft.
Google Threat Intelligence and Mandiant reported evidence that organizations in North America and Europe were likely affected. The sectors represented in the observed activity included government, financial services, education, legal services, and professional services. The researchers said the campaign had been ongoing since at least early September 2026, with the analysis published on September 29, 2026.
What the researchers confirmed
According to Google Threat Intelligence and Mandiant, exploitation of CVE-2026-88772 occurs before authentication during processing of a DTLS handshake. The research team did not possess exploit code. Instead, its assessment was based on frontline telemetry and appliance behavior. The researchers assess that specially malformed or fragmented DTLS record headers can cause heap memory boundary corruption in the NetScaler Packet Processing Engine, or NSPPE, allowing arbitrary shellcode to execute with root-level privileges on the underlying FreeBSD system.
This distinction matters. The exploit mechanism is a researcher assessment derived from observed telemetry rather than a directly analyzed exploit sample. The observed consequence, however, was consistent: exploitation attempts produced a DTLS handshake failure followed by NSPPE termination or abnormal process behavior.
Relevant telemetry included SSL handshake failure events showing DTLSv1.0 and the reason “Handshake failure-Internal Error.” System logs could also record NSPPE termination messages and watchdog activity from the pitboss service. A handshake failure followed within minutes by an NSPPE crash or termination on the same appliance should therefore receive urgent investigation, particularly when DTLS is not expected or is disabled.
The research also states that Citrix disclosed active exploitation of CVE-2026-88771. The supplied analysis does not describe that vulnerability’s technical mechanism, so defenders should not assume that controls specific to the DTLS-based activity address both issues.
From initial access to persistent web shells
After gaining access, the operators used installer-style PHP web shells to modify Apache configuration files. The changes caused files that would normally be treated as packages, signatures, or other non-script content to be executed as PHP. This created a way to stage web shells under deceptive extensions while keeping them within directories associated with VPN clients and web assets.
One persistence pattern registered the .deb extension as a PHP handler. Another used an alias rule to make requests for apparently ordinary icon files under /vpn/media/ resolve to PHP-capable files stored in a script directory. This second method could make web-shell activity resemble requests for static images.
Mandiant observed requests that returned HTTP 404 responses while taking unusually long to process or returning multi-kilobyte bodies. Error logs also contained references to missing .sig files. These observations are useful because a web shell can continue to leave traces even when access logging has been altered or requests are designed to appear unsuccessful.
The operators also sought to preserve root-level execution after the initial exploit. The research describes modification of the set-user-ID permissions on /bin/sh, allowing later web-server activity to invoke the shell with elevated privileges. Appliance reboots or Apache restarts were used to apply configuration changes. In some variants, shell history and cron references associated with the installation path were scrubbed, indicating an effort to reduce forensic visibility.
WHIPSHOT and SLAPSHOT: a two-part access channel
WHIPSHOT is described by the researchers as a PHP web shell disguised as a Debian package and placed in a NetScaler VPN script directory. Its primary role is to act as an HTTP transport bridge for SLAPSHOT rather than simply provide interactive command execution.
WHIPSHOT collects sequential HTTP header values, decodes the resulting Base64 data, and forwards it over a local connection. The headers use names beginning with HTTP_X_UX. Before forwarding traffic, WHIPSHOT checks for temporary port and lock files. If SLAPSHOT is not already running, it extracts an embedded payload and starts the Python component in the background.
The shell suppresses ordinary error reporting and returns a 404 status, even though it can place tunneled data in the response body. That combination is intended to make the endpoint look broken or irrelevant to routine web monitoring.
SLAPSHOT provides the internal-network bridge. It binds to an ephemeral loopback port, records that port in /tmp/.uxdport, and uses /tmp/.uxdlock to prevent multiple instances from running simultaneously. Its custom protocol supports opening outbound TCP connections, sending and receiving data, checking health, and closing sessions.
The tool includes automatic cleanup behavior. Individual sessions close after 15 minutes of inactivity, while the daemon can terminate after a longer idle period when no sessions or commands are active. This behavior may reduce memory use and limit the period during which the process is visible, but the temporary files and process state remain useful hunting opportunities.
In at least one observed intrusion, the actor used the proxy for manual internal reconnaissance and credential theft. The supplied research does not identify specific victims, stolen credentials, internal destinations, or a named threat actor. It also does not establish that every compromised appliance contained both WHIPSHOT and SLAPSHOT.
Useful indicators and hunting opportunities
Defenders should inspect NetScaler configuration, filesystem, process, and network telemetry together. No single artifact is sufficient: legitimate VPN traffic can include requests to media paths, while logs may have been modified.
- Review Apache configuration files for unauthorized
AddHandler,AddType, orphp_flag engine ondirectives involving extensions other than.php. - Look for
AliasMatchor similar rules mapping paths such as/vpn/media/,/vpn/theme/, or/vpn/images/into script directories. - Examine VPN script and web-asset directories for plain-text PHP masquerading as compiled binaries, archives, signatures, or static content.
- Search for
/tmp/.uxdportand/tmp/.uxdlock, unexpected Python processes, or background interpreters associated with Base64-encoded payloads. - Check whether
/bin/shhas unexpected root-owned set-user-ID permissions. - Correlate DTLS handshake failures with NSPPE termination,
pitbossmessages, unexpected restarts, or HA failovers. - Investigate 404 responses for icon or script paths that have unusually large response bodies, long processing times, or corresponding entries in HTTP error logs.
The report identifies the following network and request indicators: inbound UDP port 443 carrying DTLSv1.0; the headers HTTP_NSC_LDAP, HTTP_NSC_CLIENTTYPE, and the HTTP_X_UX family; and paths including /vpn/media/*.ico and disguised files under /vpn/scripts/linux/. Two IPv4 indicators are also provided: 143[.]198[.]7[.]94 and 157[.]254[.]167[.]12. These should be treated as research indicators, not as a complete blocklist.
What organizations should do now
Patch both vulnerabilities. Mandiant recommends applying the latest Citrix build that addresses the affected issues. The supplied guidance identifies NetScaler 14.1-73.37 or later and 13.1-64.23 or later, with separate fixed releases for certain FIPS and NDcPP deployments. Administrators should confirm the appropriate release for their deployment with Citrix rather than relying on a generic version assumption.
Investigate before rebooting where feasible. If compromise is suspected, preserve relevant appliance and virtual-machine state for forensic work when operationally practical. Isolate the affected appliance, assess both nodes in an HA pair independently, and pause configuration synchronization until each node has been validated.
Reduce exposure while patching. Mandiant describes disabling DTLS where it is not required and restricting inbound UDP/443 upstream as compensating measures for the CVE-2026-88772 activity. These controls do not replace fixed software and should not be treated as protection against CVE-2026-88771. Management interfaces should not be exposed to the internet, and outbound appliance traffic should be limited to explicitly approved destinations.
Assume appliance-held secrets may be exposed. After successful remediation, rotate NetScaler administrator credentials, local accounts, SSH keys, certificates and private keys, and integration secrets such as LDAP, RADIUS, TACACS, SNMP, and API credentials. Revoke active sessions and review connected Citrix infrastructure, PAM systems, and identity logs for follow-on activity.
Improve visibility. Ensure the SIEM receives NetScaler audit data, FreeBSD system logs, web access and error logs, and firewall or flow telemetry from appliance addresses. Detection should correlate appliance crashes, configuration changes, suspicious web requests, unexpected egress, and identity activity rather than depending on one indicator.
Conclusion
The campaign illustrates why edge appliances require the same incident-response attention as servers and endpoints. NetScaler devices can sit outside conventional EDR coverage while handling authentication, remote access, certificates, and integration credentials. The combination of root-level exploitation, disguised PHP execution, and an internal TCP proxy creates a credible path from perimeter compromise to deeper network activity.
Organizations should prioritize fixed Citrix releases, inspect configuration and runtime artifacts, preserve evidence when compromise is suspected, and rotate secrets after remediation. The most important unknowns remain the complete victim set, the identity of the operators, and the full scope of activity associated with the second vulnerability.