
Cisco Talos on Making Cyber Defense Harder to Abuse
Cisco Talos argues that behavior-based detection, controlled tools, deception, and bounded AI agents can reduce attacker flexibility.
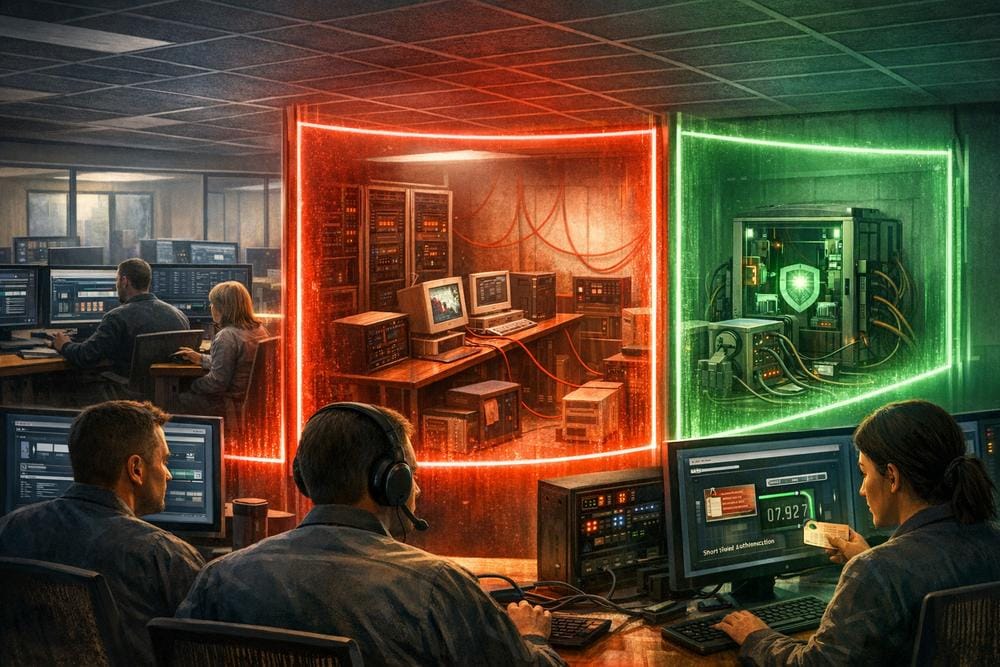
Cisco Talos’s October 1, 2026, Threat Source newsletter is not a campaign report or malware analysis. It contains no detailed incident investigation, attack-chain reconstruction, threat-actor attribution, vulnerability identifier, or dedicated detection package. Its principal technical contribution is a short defensive argument: organizations should make common attacker options less reliable by controlling legitimate tools, detecting behavior rather than individual payloads, introducing deception, and placing firm boundaries around AI agents.
That distinction matters. The newsletter includes references to several security stories and lists files observed in Talos telemetry, but the supplied material does not connect those items into a single campaign. It also does not explain how the listed files operate, how they arrived on systems, whether they established persistence, or whether they communicated with command-and-control infrastructure. Any assessment of those details would go beyond the available research.
The central idea: reduce attacker flexibility
Talos frames defense as a problem of economics and operational friction. Threat actors benefit when enterprise environments are predictable, remote-management utilities are broadly available, and security teams focus narrowly on recognizing a particular malware family. In that model, an attacker can replace one payload or tool with another while continuing toward the same objective.
The newsletter therefore recommends focusing on the activity that enables an intrusion, rather than relying exclusively on a named file or a static signature. This is a practical shift for defenders managing diverse endpoints, cloud services, remote administration platforms, and increasingly automated workflows. The goal is not to identify every possible payload in advance. It is to make unauthorized actions harder to perform quietly, regardless of which specific utility or file is used.
Talos describes this approach as “friction”: controls that slow an operation, increase its visibility, or force an adversary to take a riskier path. Deception can add uncertainty, while behavioral detections can expose suspicious use of otherwise legitimate capabilities. The newsletter also presents the possibility that sufficient friction may cause an operation to fail or become too costly to continue.
Legitimate administration tools require governance
One recommendation is to allow approved remote monitoring and management, or RMM, tools while blocking unauthorized ones. RMM software can be useful for IT teams and managed service providers, but its administrative purpose also makes governance important. The supplied research does not identify a particular RMM product, a specific abuse case, or a confirmed intrusion involving one. Talos’s point is broader: organizations should know which remote-management tools are authorized and prevent unapproved alternatives from becoming an invisible extension of administrative access.
For administrators, that means treating RMM inventory as an access-control issue rather than merely a software inventory exercise. An organization should establish which tools are approved, which business units or providers may use them, and which endpoints they may manage. The associated accounts, certificates, service permissions, and network destinations should be reviewed as part of the same process.
MSPs face an additional governance challenge because their tools may operate across multiple customer environments. A clear separation between customers, documented authorization, and rapid review of new tooling can help prevent a trusted management channel from becoming an unmanaged path into many systems. These are general defensive recommendations derived from Talos’s control-focused guidance, not findings about a specific MSP incident.
Why behavior-based detection matters
Talos cautions against depending solely on tool-specific or malware-specific detections. A file hash can be valuable for triage, but it describes one artifact. An adversary may alter or replace that artifact without changing the underlying objective. Behavioral analytics can instead examine combinations of events, such as unusual administrative activity, unexpected remote-management use, or actions that fall outside an account’s normal scope.
The supplied newsletter does not provide detection queries, thresholds, telemetry requirements, or MITRE ATT&CK mappings. It therefore cannot support a claim that a particular rule will identify the activity discussed. Organizations should validate behavioral ideas against their own environment and avoid treating every administrative action as malicious.
A useful starting point is to define expected behavior for privileged accounts, remote-support tools, service accounts, and automation identities. Security teams can then look for deviations involving timing, destination, device population, privilege level, or the combination of actions. Alert quality will depend on context: an approved support session from a known provider should be distinguishable from an unapproved tool appearing on an employee workstation.
Deception as an early-warning layer
The newsletter also recommends deception techniques, including fake employee profiles or false infrastructure. The supplied material does not describe a deployed deception system, a confirmed adversary interaction with one, or measured results. Talos presents deception as a way to create uncertainty and generate opportunities for defenders to observe activity that should not occur.
Deception controls need careful ownership. Decoy identities, systems, or data should be clearly separated from production workflows and monitored for access. Their value depends on low expected legitimate use; excessive noise can make alerts difficult to investigate. Organizations should also ensure that decoys do not accidentally expose real personal information or create confusion for help-desk and incident-response teams.
When a decoy generates an alert, responders should preserve the surrounding context rather than treating the event as proof of a complete compromise. The alert may indicate probing, mistaken access, or unauthorized activity, but the supplied Talos research does not define an interpretation model. Investigation should establish which identity, device, network path, and permissions were involved.
AI agents need identifiable, temporary access
Talos extends the same control philosophy to AI agents. Its guidance is to give agents identifiable, short-lived credentials and strict network boundaries. The newsletter does not identify a particular AI platform, agent, incident, or exploit. It does, however, treat machine-driven activity as requiring explicit accountability and constrained reach.
Short-lived credentials can reduce the period during which an exposed or misused token remains useful. Identifiable credentials can make activity easier to attribute to a particular agent, workflow, or owner. Network boundaries can limit which services an agent can reach and reduce the consequences of an unintended action. These controls should be paired with permissions limited to the agent’s documented task.
Organizations should also maintain an inventory of deployed agents and the data, APIs, tools, and environments they can access. Approval processes should cover changes to an agent’s permissions or connected services. Logging should capture the identity of the agent, the requesting workflow, the target service, and the result, subject to applicable privacy and data-retention requirements.
What the telemetry section does—and does not—show
The newsletter lists five files described as the most prevalent malware files in Talos telemetry for the stated week. The entries include SHA-256 and MD5 hashes, example filenames, and Talos detection names. The listed example filenames are sample.exe, d4aa3e7010220ad1b458fac17039c274_63_Exe.exe, tmp00055df5.dll, f_006048.exe, and SECOH-QAD.exe.
The supplied research does not identify victims, infection vectors, malware families, persistence mechanisms, defense-evasion behavior, C2 infrastructure, geographic distribution, or impact associated with these files. Their presence in telemetry should not be interpreted as evidence that a reader’s environment is compromised. Organizations can use the hashes as search pivots if their own security processes permit, but a match would require validation in context.
The newsletter also mentions other security headlines, including reports involving air-traffic-control operations, a cybersecurity nonprofit, NetScaler, a Pentagon personnel agency, and TeamViewer. Those references are summaries of external coverage rather than technical findings developed in the supplied Talos material. No CVE, victim detail, exploitation sequence, or attribution from those stories should be assigned to the central defensive recommendations here.
What organizations should do now
- Inventory remote administration. Identify approved RMM products, owners, service accounts, managed devices, and expected network destinations. Block or investigate unauthorized RMM software.
- Move beyond file-centric detection. Combine endpoint, identity, network, and administrative telemetry to identify unusual behavior, while tuning alerts around known business workflows.
- Review privileged access. Confirm that administrator accounts, service identities, and provider access have only the permissions and reach required for their jobs.
- Use deception deliberately. Deploy tightly scoped decoys only where they can be monitored, maintained, and investigated without exposing real data or disrupting operations.
- Constrain AI agents. Use distinct identities, short-lived credentials, limited permissions, and network boundaries. Log agent actions and review changes to connected tools.
- Validate telemetry coverage. Ensure incident responders can correlate account activity, endpoint processes, remote sessions, and network connections when an anomaly appears.
- Handle hash matches carefully. Treat the Talos-listed hashes as investigative pivots, not proof of compromise, and preserve relevant evidence before taking disruptive action.
Conclusion
Cisco Talos’s supplied newsletter offers a defensive framework rather than a threat report. Its confirmed guidance centers on limiting unauthorized tools, detecting behavior, using deception, and constraining AI agents. The source does not provide enough evidence to describe a specific malware operation, victim set, exploit, or threat actor. For security teams, the practical lesson is to make access paths explicit, observable, and narrowly permitted—and to use layered controls that remain useful when an attacker changes the file or utility involved.