Ai Threat Intel Analysis PAYLOAD ransomware turns Active Directory into an attack tool Kaspersky’s analysis shows how PAYLOAD used trusted Active Directory Group Policy to disrupt a manufacturing environment without Windows encryption.
Security News Fake LastPass Authenticator Installer Abuses Microsoft-Signed Driver to Kill Antivirus and EDR TheHackerNews
Security News Contagious Interview Campaign Compromises 30,000 Devices, Steals $10.71M in Crypto TheHackerNews
Security News ⚡ Weekly Recap: Cisco 0-Day, AI Agent RCE, ClickFix Attacks, ClickFix Surge, and Browser Hijacks TheHackerNews
Security News TASK#STOMP PowerShell Backdoor Steals Documents, Wi-Fi Passwords, and Clipboard Data TheHackerNews
Security News ClickFix Lures Deploy ChainScript RAT Using Polygon to Rotate C2 Infrastructure TheHackerNews
Security News Jade Sleet Linked to Indian IT Provider Breach With FLATROOF and ROOFDECK Backdoors TheHackerNews
Ai Threat Intel Analysis Atomic macOS Stealer: How Deceptive Setup Guides Deliver AMOS Palo Alto Unit 42’s lab analysis shows how deceptive macOS setup instructions deliver AMOS, harvest sensitive data, and establish persistence.
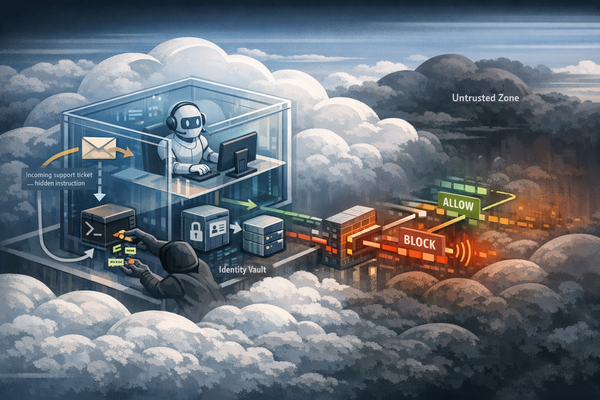
Ai Threat Intel Analysis AWS AgentCore Harness: When Prompt Injection Reaches Credentials Unit 42’s testing shows how default AgentCore Harness tools can turn prompt injection into credential exposure, with practical controls for AWS operators.
Security News BragJack attacks hijack AI browser agents through malicious extensions BleepingComputer
Security News ShinyHunters hacks Clop leak site, threatens to extort ransomware gang BleepingComputer