
Executive Threat Detection: Hunting High-Value Assets
Cisco Talos outlines an intelligence-led approach to hunting for subtle threats against executives and other high-value organizational assets.
Executives are not simply another category of endpoint user. Their accounts may provide access to sensitive financial information, strategic communications, intellectual property, and business decisions. They also tend to operate across a wider digital footprint than many employees, increasing exposure to targeted phishing, social engineering, and account-compromise attempts.
In a report announcing its Executive Threat Detection service, Cisco Talos argues that this risk requires more than broad, automated security monitoring. Its proposed answer is a recurring, intelligence-led hunting process focused on executive-associated systems and other high-value assets.
The report is primarily a description of a commercial incident-response service rather than a case study of a particular intrusion. It does not identify a victim, malware family, threat actor, exploit, campaign indicator, or confirmed breach. Its value for defenders is therefore methodological: it describes how a security team could narrow its focus, develop hunting hypotheses, and combine internal telemetry with external intelligence.
Why high-value users can evade broad monitoring
Cisco Talos assesses that organization-wide endpoint detection and response remains an important foundation, but says it may not provide sufficient attention to executive systems. In a large environment, security teams must process substantial volumes of routine activity. Subtle changes affecting a small number of high-value users can be difficult to distinguish from normal behavior, particularly when an attacker remains quiet over an extended period.
The report specifically frames executives as attractive targets because their accounts may connect to valuable business information and systems. It also points to the personal and professional exposure created by executive digital footprints. That exposure can support bespoke social engineering or targeted credential theft, although the supplied research does not describe a specific campaign or explain how any named actor carried out such an operation.
This distinction matters operationally. The report does not claim that executive accounts are routinely compromised, nor does it provide a measured compromise rate. Instead, Cisco Talos presents executive targeting as a risk that can be overlooked when monitoring is optimized primarily for the average user profile.
The proposed hunting model
Executive Threat Detection is described as an ongoing service supporting up to 10 principals. Cisco Talos says its process uses monthly, human-led threat hunting and intelligence analysis. The stated objective is to identify compromise of executive-associated assets before those systems or accounts can be used in a broader intrusion.
The methodology has several connected elements:
- External intelligence review: Incident commanders and intelligence analysts conduct an open-source intelligence review each month. The purpose is to identify emerging threats relevant to executive personas and translate them into indicators or behaviors that can be searched in customer environments.
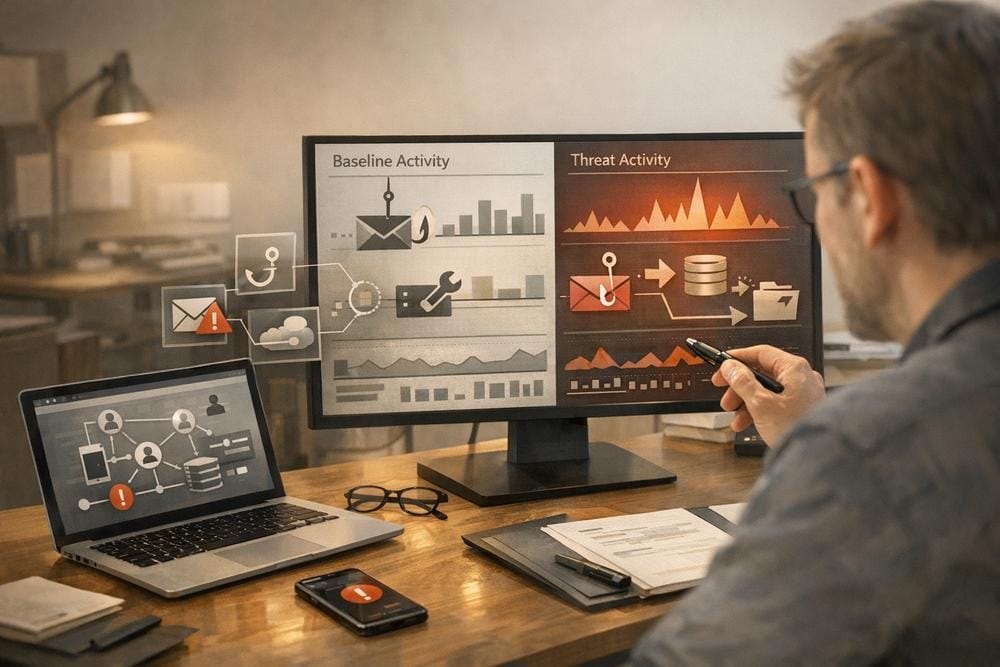
- Baseline hunting: Consultants review available events and telemetry for anomalies that automated alerts may not have surfaced. The report says this includes attention to living-off-the-land activity, in which legitimate system tools are used in ways that can make malicious behavior harder to recognize.
- Emerging-threat hunting: The team applies atomic or pattern-based indicators derived from the monthly intelligence review. Cisco Talos presents this as a way to test executive systems against newly observed campaigns or techniques rather than relying only on static detection content.
- Outside-in monitoring: Analysts monitor for indications that an executive’s corporate information may have been exposed or leaked. This extends the investigation beyond device events and account telemetry.
The research does not publish the specific data queries, detection rules, intelligence feeds, indicators, or event thresholds used by the service. It also does not enumerate MITRE ATT&CK techniques or provide a reproducible hunt package. Organizations should therefore treat the description as a planning model, not as a complete detection playbook.
How the attack sequence is framed
The source does not document a confirmed attack chain. It describes a risk sequence instead: a targeted threat may focus on an executive or another high-value principal, gain an initial foothold through a personalized attack, remain unobtrusive, and eventually use access to reach more valuable corporate resources.
Several possible behaviors are mentioned at a high level, including phishing kits intended to bypass multifactor authentication, zero-day exploits offered in criminal markets, social engineering, and the abuse of legitimate system tools. These are examples of the types of developments the service says it may monitor; they are not presented as evidence that a particular customer was attacked with any of them.
That limitation should guide interpretation. There is no supplied evidence tying the service announcement to a named malware family, a specific vulnerability, a particular infrastructure set, or a confirmed intrusion. No malicious domains, IP addresses, email addresses, or URLs are reported. Accordingly, there are no source-supported indicators of compromise to reproduce or hunt directly.
Visibility without changing executive systems
Cisco Talos says the service is designed to use an organization’s existing security stack and typically does not require changes to executive systems. The stated rationale is to preserve productivity and avoid the operational disruption that can accompany additional endpoint controls, system changes, or aggressive automated response.
For defenders, this highlights a practical design question: whether existing telemetry is detailed and reliable enough to support focused investigations. Relevant sources may include endpoint events, identity and authentication records, email security data, cloud application logs, browser and software inventories, remote-access records, and external exposure monitoring. The supplied research does not require any particular product or identify the telemetry fields used by Cisco Talos, so organizations should validate coverage in their own environments before assuming that an existing toolset provides adequate visibility.
Silent monitoring also creates a response trade-off. Hunting can reduce disruption, but a serious finding requires a clearly defined escalation path. Cisco Talos says a critical discovery under the service can lead to an emergency-response engagement. Organizations building their own process should similarly establish who can authorize containment, how executive activity will be handled during an investigation, and how legal, privacy, communications, and business leadership will be involved.
What organizations should do now
The following actions are general defensive recommendations based on the risks and workflow described by Cisco Talos. They are not claims about controls implemented by the service or about any specific incident.
- Identify high-value principals and systems. Document which executive accounts, devices, cloud identities, mailboxes, collaboration platforms, and administrative relationships could materially affect the organization if compromised. Include assistants, delegates, service accounts, and recovery channels where appropriate.
- Test telemetry coverage. Confirm that security teams can reconstruct authentication activity, privilege changes, mailbox access, endpoint process activity, remote sessions, and relevant cloud actions for those principals. Record retention gaps and differences between executive and standard-user coverage.
- Create focused hunting hypotheses. Develop searches for unusual sign-ins, unexpected access paths, abnormal use of legitimate tools, new persistence-related changes, suspicious mailbox activity, and activity inconsistent with an executive’s normal work pattern. Keep hypotheses tied to available evidence and review them regularly.
- Use current intelligence to refresh hunts. Track credible reporting about targeted phishing, identity attacks, exposed credentials, and software vulnerabilities that affect the organization’s executive environment. Convert relevant findings into testable searches rather than forwarding intelligence without an operational action.
- Monitor external exposure. Review whether corporate contact information, credentials, documents, or other executive-associated data appear in known exposure sources. Establish a documented process for validating reports and protecting sensitive information during review.
- Strengthen recovery and escalation procedures. Verify that high-value accounts have strong authentication, protected recovery methods, appropriate privilege separation, and rehearsed incident-response contacts. Make sure a suspected executive compromise can be investigated without relying solely on the potentially affected account.
- Report findings in two layers. Technical teams need evidence, timelines, affected assets, and disposition. Leaders need risk, business impact, decisions required, and remediation status. Separating those views improves both response speed and accountability.
Confirmed findings, assessments, and open questions
Confirmed in the source: Cisco Talos announced Executive Threat Detection as a proactive service for up to 10 principals, with monthly human-led hunting, intelligence analysis, reporting, strategic recommendations, and monitoring of executive-related corporate information. The described workflow includes OSINT review, baseline and emerging-threat hunting, and use of existing security tools.
Researcher assessment: Cisco Talos assesses that executives and other high-value users face personalized targeting and that low-and-slow activity may be missed in broad enterprise monitoring. It presents focused hunting as a way to close that visibility gap.
Not established by the research: The report does not identify a confirmed victim, breach, attacker, malware, CVE, exploit, campaign, technical indicator, or measured effectiveness result. It also does not provide enough detail to independently reproduce the service’s detection logic.
Conclusion
Executive-focused monitoring is best understood as a prioritization strategy, not a replacement for enterprise security controls. Cisco Talos’ announcement makes a defensible case for combining targeted asset inventories, human investigation, current intelligence, and external exposure monitoring. Organizations can apply the same principles internally by improving telemetry around high-value identities, testing focused hunting hypotheses, and preparing an escalation process before a suspected compromise becomes a business crisis.