
AI Is Reshaping Vulnerability Discovery and Exploitation
Google Threat Intelligence finds faster vulnerability disclosure and exploitation, with edge appliances and AI infrastructure emerging as priority risks.
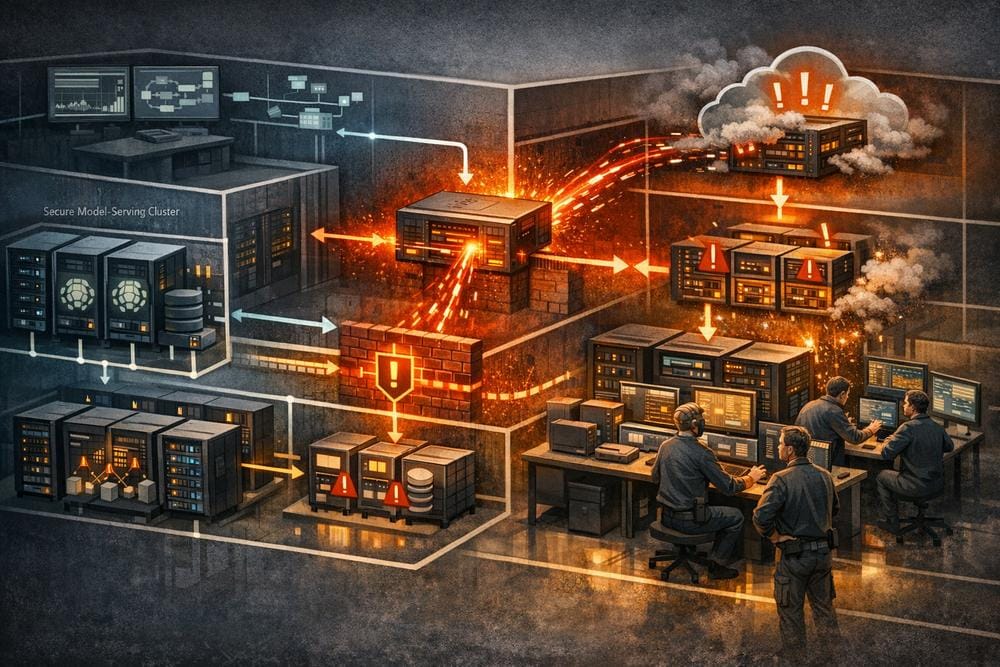
Artificial intelligence is changing vulnerability management in two connected ways: it is helping researchers identify flaws more efficiently, while also creating new software layers that can be attacked. The result is not simply a larger list of vulnerabilities. It is a security environment in which disclosure volume, exploit development, and operational exposure are moving faster than many traditional remediation processes can accommodate.
That is the conclusion of an analysis by Google Threat Intelligence Group (GTIG), based on vulnerabilities disclosed between January 1, 2025, and August 31, 2026. The research examines disclosure rates, in-the-wild exploitation, GTIG’s own vulnerability risk ratings, and vulnerabilities affecting artificial intelligence and large language model infrastructure.
GTIG’s findings point to a need for more selective vulnerability prioritization. The organization does not argue that every newly assigned CVE represents an immediate compromise risk. Instead, its data shows that defenders must separate disclosure volume from operational danger, focusing on exposed systems, exploitation evidence, attack surface, and consequences such as remote code execution.
A larger vulnerability pipeline, but not uniform risk
GTIG recorded a sharp increase in monthly vulnerability disclosures during 2026. The number rose from 5,045 in January to 10,477 in July and 10,740 in August. High-risk disclosures also increased, rising from 131 in January to 350 in August. Although high-risk issues represented only about 3% of all August disclosures in GTIG’s rating system, their growth was considerably faster than the overall baseline.
The research cautions that raw CVE counts can be misleading. Automated assignment practices in some open-source ecosystems can substantially increase totals without producing a corresponding rise in active attacks. GTIG cites vulnerabilities whose descriptions referenced the Linux kernel as an example: approximately 5,000 CVEs appeared between January and August 2026, with no observed exploited zero-days in that group.
Vendor disclosure cycles also affected the figures. GTIG attributes notable portions of the high-risk increase to concentrated disclosures involving TOTOLINK consumer router firmware, Oracle middleware, and Linux kernel network drivers. These examples demonstrate why a monthly count should not be treated as a direct measure of attacker interest. A large vendor release can change the statistics even when the practical risk is concentrated in a small number of externally reachable products.
Exploitation is growing, but remains selective
GTIG identified 141 distinct vulnerabilities disclosed and exploited between January and August 2026, compared with 127 exploited vulnerabilities during all of 2025. The average number exploited per month rose from 10.5 in 2025 to 18 during the first eight months of 2026.
That increase is significant, but the proportion of disclosed vulnerabilities observed in active exploitation remained very small. GTIG reports that only 0.23% of vulnerabilities disclosed in 2026 were seen being exploited, or roughly one in 431. The practical implication is important: organizations should not respond to disclosure volume with indiscriminate, unprioritized mass patching alone. They need a way to identify the relatively small subset of flaws that create immediate exposure.
GTIG’s assessment is that the growth in exploitation was driven primarily by the rapid weaponization of known vulnerabilities, or n-days, rather than by a comparable increase in newly discovered zero-days. Exploitation of high-risk vulnerabilities more than doubled, from 28 during 2025 to 75 between January and August 2026.
Zero-day exploitation increased more modestly, from an average of eight per month in 2025 to 11 per month during the 2026 period. August was an exception, with 22 zero-days recorded. GTIG says zero-days accounted for 62% of all observed exploited vulnerabilities from January through August 2026, but still represented a very small share of total disclosed vulnerabilities.
The organization suggests that threat actors may be using large language models and other AI tools to compare product versions, patches, advisories, and proof-of-concept material, potentially shortening the time required to weaponize n-days. This is presented as an assessment rather than a comprehensive measurement of attacker behavior. Public evidence remains limited, and the research does not establish that AI was involved in every observed exploit.
Perimeter systems remain a practical priority
GTIG found that vulnerabilities affecting edge and security appliances represented 14% of exploited vulnerabilities from January through August 2026. Enterprise directory and collaboration hubs represented another 11%. More than 65% of exploited edge vulnerabilities met GTIG’s High or Critical Threat Risk ratings.
The research characterizes exposed management interfaces and other perimeter services as especially important because they can provide initial access before endpoint security controls have visibility into the activity. This makes internet-facing gateways, security appliances, remote-access products, and enterprise services valuable targets even when the wider vulnerability population is expanding much more rapidly.
For defenders, the finding supports a practical ordering of work: first identify externally reachable assets, then determine whether vulnerable services are exposed without authentication or have privileged access to internal systems. A lower-rated flaw on an isolated internal host may deserve less immediate attention than a high-impact vulnerability in an internet-facing gateway.
AI-assisted discovery may produce more consequential flaws
GTIG’s analysis of vulnerabilities it could identify as likely AI-discovered found a different risk distribution from the broader CVE population. Conventional disclosures in the dataset were 69% Low Risk, 28% Medium Risk, and 3% High Risk according to GTIG ratings. The AI-discovered group was 39% Low Risk, 58% Medium Risk, and 4% High Risk.
The same divergence appeared in exploitation consequences. Half of the AI-discovered vulnerabilities led to remote code execution, compared with 26% across the wider CVE ecosystem. AI-discovered issues were less concentrated in information disclosure and data manipulation.
GTIG describes this as an early indicator, not a settled industry-wide trend. The organization also warns that public data undercounts AI-assisted discovery because CVE records do not consistently identify whether AI was involved. Cloud and SaaS providers may fix AI-surfaced flaws directly in production without requesting a CVE, while other findings may remain confidential during coordinated disclosure.
The report includes CVE-2026-1731 as an example of the potential operational impact. GTIG says the unauthenticated operating-system command-injection vulnerability in BeyondTrust Privileged Remote Access and Remote Support was autonomously discovered by a third-party research agent identified as Hacktron AI. After public disclosure, GTIG observed exploitation in targeted initial-access campaigns and reported that multiple threat clusters used the flaw within days. The organization also observed post-exploitation activity including privilege escalation, data exfiltration, and deployment of SNOWLIGHT, SPARKRAT, and cryptominers.
Those observations are specific to GTIG’s reporting. The supplied research does not identify affected victims by name, and it does not establish that all exploitation of the vulnerability used the same tooling or followed the same sequence.
AI infrastructure is becoming an additional attack surface
GTIG tracked 2,076 cumulative AI-related CVE disclosures across eight architectural layers during its monitoring window, including more than 1,500 from January through August 2026. The largest category was AI orchestration and agent frameworks, with 782 disclosures. Web applications and portals accounted for 230, inference and serving infrastructure for 212, model security advisories for 106, and machine-learning frameworks and hubs for 99.
The report identifies orchestration middleware as a major concentration point. Frameworks and visual workflow tools may connect language-model prompts to tools, files, code, and external services. GTIG reports vulnerability patterns including unsafe workflow serialization, insecure Python tool calling, server-side template injection, and command injection. The organization says orchestration-related disclosures increased 347% in 2026 and represented 50% of AI-related flaws in its dataset.
Inference infrastructure is another concern. GTIG recorded 212 vulnerabilities in products and frameworks used to serve models, including vLLM, Ollama, LiteLLM, Llama.cpp, Triton, Ray, TGI, SGLang, TensorRT-LLM, BentoML, and LocalAI. Nearly 24% of these flaws were attributed to unauthenticated APIs or server-side request forgery. Potential consequences described by GTIG include unauthorized access, resource exhaustion, and exposure of model checkpoints.
GTIG says it has not observed zero-day exploitation of AI infrastructure, but has confirmed in-the-wild exploitation of a small number of newly disclosed middleware vulnerabilities. Examples listed in the research include CVE-2026-42271 in BerriAI LiteLLM, CVE-2026-5027 in Langflow, and CVE-2025-3248 in Langflow. The reported impact categories include command injection, arbitrary file writing, and unauthenticated code injection. Organizations should verify affected versions and vendor guidance through authoritative advisories rather than infer exposure from product names alone.
What organizations should do now
- Prioritize exposed attack surfaces. Maintain an inventory of internet-facing appliances, remote-access services, AI gateways, inference servers, orchestration platforms, and administrative APIs. Confirm whether management interfaces are publicly reachable and whether they require authentication.
- Combine vulnerability data with threat intelligence. Rank remediation using observed exploitation, asset exposure, privilege, business function, and exploit consequence. Treat GTIG risk ratings as separate from CVSS; the report explicitly uses its own rating system.
- Accelerate remediation for high-impact n-days. Establish emergency workflows for vulnerabilities with active exploitation, unauthenticated access, command execution, arbitrary file writing, or direct access to credentials and sensitive data.
- Protect AI services as production infrastructure. Separate model-serving systems and agent workloads from sensitive networks, restrict administrative APIs, limit outbound connectivity, and avoid treating internal AI components as inherently trusted.
- Monitor for unusual perimeter and AI-platform activity. Review authentication events, administrative API access, unexpected workflow or configuration changes, unexplained file creation, unusual model downloads, and abnormal GPU or compute consumption.
- Use automation carefully. Automated inventory, exploitability assessment, and remediation can help compress response times, but changes should be governed, logged, tested, and reversible—particularly where agent frameworks can execute actions or access data.
- Build security review into development. Organizations that ship software should consider AI-assisted code review and continuous testing as complementary controls, while validating findings through normal engineering and coordinated disclosure processes.
Conclusion
GTIG’s research describes a vulnerability ecosystem expanding in both scale and complexity. Disclosure counts are rising, exploitation is increasing mainly through high-risk n-days, and AI-assisted research appears to find a higher proportion of flaws with consequential outcomes such as remote code execution. At the same time, orchestration frameworks, inference services, and AI gateways are introducing new paths into enterprise environments.
The central defensive lesson is not to chase every CVE equally. Organizations should identify exposed systems, use evidence of exploitation to guide urgency, secure AI infrastructure as carefully as other production services, and automate remediation where controls are mature enough to manage the risk.