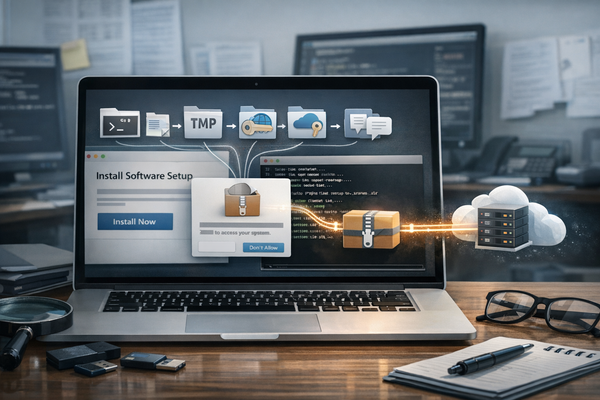
Ai Threat Intel Analysis Atomic macOS Stealer: How Deceptive Setup Guides Deliver AMOS Palo Alto Unit 42’s lab analysis shows how deceptive macOS setup instructions deliver AMOS, harvest sensitive data, and establish persistence.
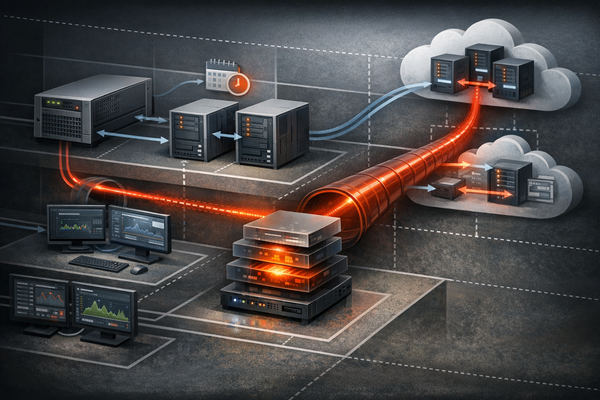
Ai Threat Intel Analysis NightEagle’s GhostContainer Campaign Targets Russian Businesses Kaspersky details NightEagle’s use of GhostContainer, Exchange servers, tunneling tools, RDP weaknesses, and Active Directory abuse.
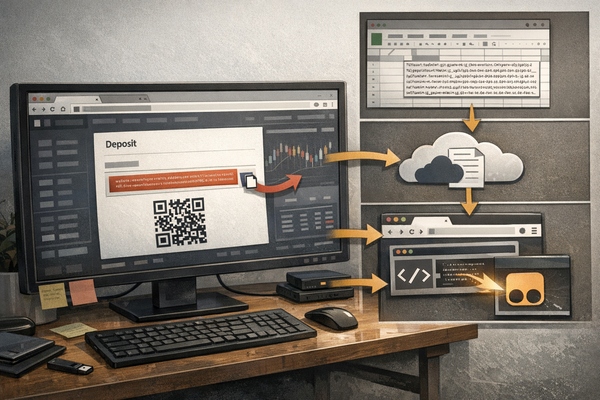
Ai Threat Intel Analysis ClickFix Turns the Browser Into a Cryptocurrency Skimmer Cisco Talos describes a ClickFix campaign that uses Google-hosted JavaScript, browser injection, and fake cryptocurrency bonuses to redirect deposits.
Ai Threat Intel Analysis September 2026 Microsoft Patch Tuesday: What to Prioritize Cisco Talos identifies two exploited flaws and a broad set of high-priority Microsoft vulnerabilities, with Snort coverage for selected attack attempts.
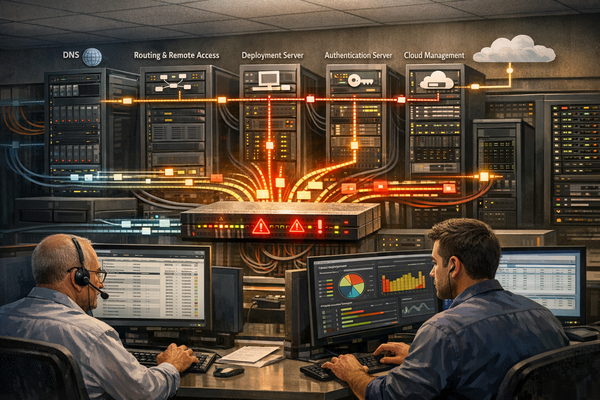
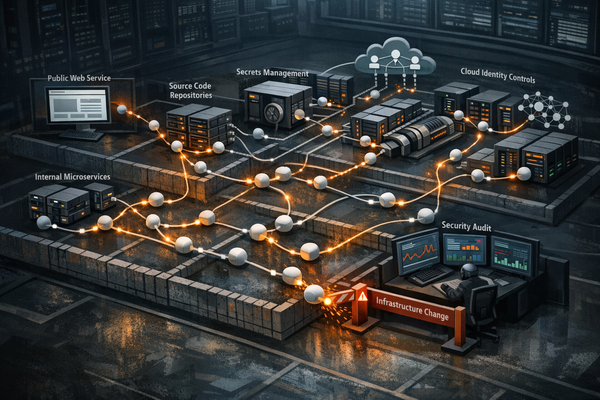
Ai Threat Intel Analysis How AI Agents Compressed an Enterprise Intrusion Unit 42 details an AI-assisted enterprise intrusion that automated reconnaissance, credential theft, pipeline abuse and cloud takeover.
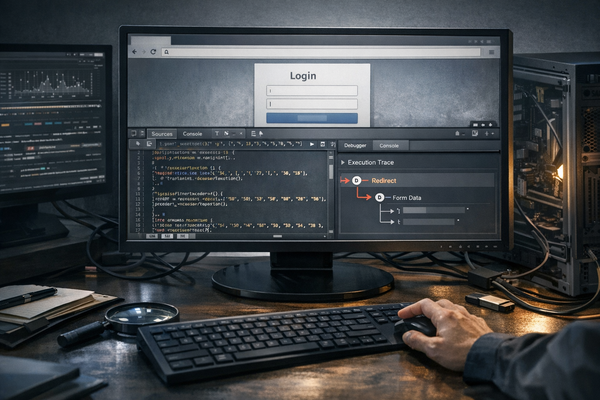
Ai Threat Intel Analysis How Obfuscated JavaScript Powers Modern Phishing Kits Cisco Talos explains how phishing kits hide JavaScript behavior and how defenders can safely recover redirects, payloads, and credential-theft logic.
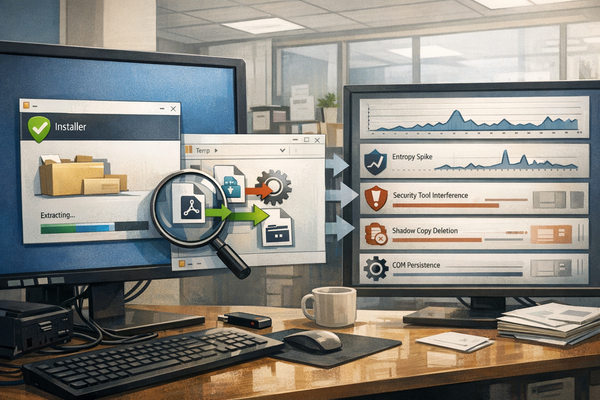
Ai Threat Intel Analysis AI-Enabled Malware: What Defenders Need to Know Unit 42’s analysis finds that AI is accelerating malware development, but conventional behavioral, endpoint, and sandbox defenses still detect the resulting code.