
NightEagle’s GhostContainer Campaign Targets Russian Businesses
Kaspersky details NightEagle’s use of GhostContainer, Exchange servers, tunneling tools, RDP weaknesses, and Active Directory abuse.
Kaspersky’s Global Emergency Response Team has documented a campaign by the group it identifies as NightEagle, also tracked as APT-Q-95, against businesses in Russia. The organization says the group has been active since at least 2023 and had previously focused on organizations in Asia.
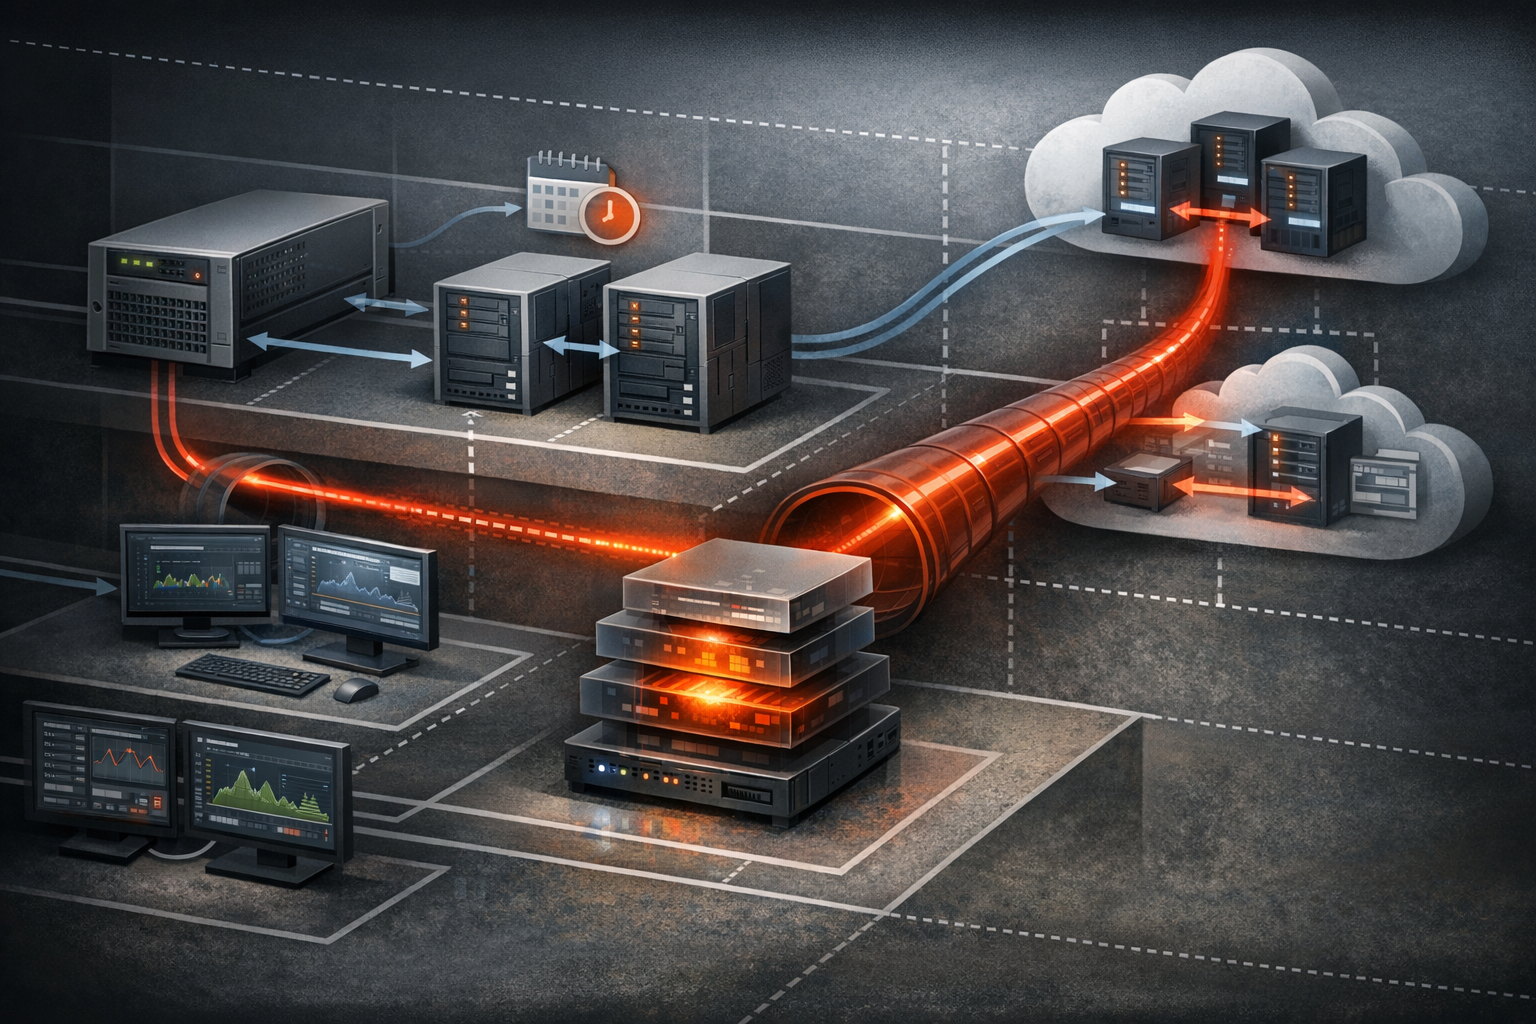
The campaign combines compromised VPN credentials, a .NET backdoor placed on Microsoft Exchange servers, traffic tunneling through legitimate or publicly available tools, and abuse of weaknesses in Remote Desktop Protocol (RDP) and Active Directory. The result is an intrusion pattern designed to preserve internal access while limiting the need for conspicuous inbound connections.
Several elements of the operation are confirmed through Kaspersky’s incident investigations. Other details, particularly the precise method used to install the Exchange backdoor, remain an assessment rather than a directly observed fact. That distinction matters when organizations use the report to prioritize investigation and detection.
What Kaspersky observed
In the incidents reviewed, initial access commonly involved valid credentials used to connect to corporate VPNs. Kaspersky observed connections originating from Russian IP space associated with Cloudflare WARP tunnels, as well as addresses linked to virtual infrastructure providers in Europe.
The use of valid credentials means that a conventional malware-focused investigation may miss the earliest stage of the intrusion. Authentication logs, VPN telemetry, source-location changes, unusual access times, and activity inconsistent with a user’s normal pattern are therefore important parts of the detection picture.
Kaspersky found that the attackers deployed the GhostContainer backdoor on Microsoft Exchange servers during both initial access and later phases. The researchers identified components associated with several open-source projects, including the Neo-reGeorg tunneling project, the GhostWebShell class from the ysoserial utility, and an exploit associated with CVE-2020-0688. Kaspersky says these components are publicly available on GitHub.
The research organization did not determine exactly how GhostContainer was delivered to the Exchange servers. Kaspersky assessed with a high degree of confidence that the attackers used a previously observed method involving cryptographic keys in the ASP.NET configuration, manipulation of the VIEWSTATE parameter, and injection of a payload that launched the backdoor in memory. This is an assessment, not a confirmed observation of the delivery step in every incident.
GhostContainer’s role on Exchange
GhostContainer is a .NET assembly built around three principal classes, according to Kaspersky’s analysis. The component named Stub processes commands received through the x-owa-urlpostdata headers. It also attempts to interfere with AMSI and Windows Event Log visibility by overwriting addresses in amsi.dll and ntdll.dll.
The other components support web-path handling and network forwarding. App_Web_843e75cf5b63 accepts the fakePath and fakePageName parameters and creates virtual paths that redirect requests to App_Web_8c9b251fb5b3. That class provides traffic-proxying and socket-forwarding functionality.
This design gives the operators two useful capabilities. First, the backdoor can receive commands through web-facing Exchange functionality rather than requiring a separate, obvious service. Second, the same server can act as a bridge into internal systems. Kaspersky detected identified GhostContainer samples as Trojan.MSIL.GhostContainer.gen and reported similarity to previously analyzed samples through its Threat Analysis and Threat Attribution Engine technologies.
The observed defense-evasion behavior is especially relevant to incident responders. If a compromised process has modified AMSI or event-logging behavior, the absence of expected telemetry cannot be treated as evidence that no suspicious activity occurred. Investigators should compare endpoint telemetry with Exchange, network, identity, and infrastructure logs collected independently.
From Exchange access to internal tunneling
After obtaining sufficient privileges, the operators used RDP for lateral movement. Kaspersky found that they downloaded and executed tools for forwarding and tunneling network traffic, using GitHub repositories to host archived tool packages.
The repositories were made to appear legitimate. Kaspersky identified repositories named mirror-js/mirror-js and browserthemes/resourcepack, with archive paths that appeared related to JavaScript or resource-pack content. The researchers also found executable names designed to resemble familiar business software, including AdobeSync.exe, adobe_32.exe, trueconf.exe, 1cbroker.exe, 1c-office-plugin.exe, and trueconf-broker.exe.
The reported repository references are: hxxps://github[.]com/mirror-js/mirror-js and hxxps://github[.]com/browserthemes/resourcepack. These indicators should be handled as investigation leads rather than proof that every download from the underlying service is malicious.
Two tunneling mechanisms were used together. One was Microsoft dev tunnels, a legitimate Microsoft service that can publish local web services through *[.]devtunnels[.]ms domains. Kaspersky says the attackers used it to expose TCP port 3389, the standard RDP port, on a compromised system.
The second was rdp2tcp, a publicly available tool that carries TCP traffic over an established RDP connection. The combination allowed the operators to maintain access through legitimate services and existing protocol channels without necessarily opening additional suspicious ports on the target network.
Windows Remote Desktop Services logs can provide a particularly useful detection opportunity. Kaspersky reports that RDP virtual-channel creation and closure are recorded with event IDs 132 and 148 in the Microsoft-Windows-RemoteDesktopServices-RdpCoreTS/Operational.evtx log. Normal RemoteFX-related channel names may appear there, while use of rdp2tcp or unexpected random alphanumeric channel names can indicate tunneling activity. The context of each event must be evaluated because channel names alone are not conclusive.
The operators also used the atexec utility from the Impacket toolkit to create scheduled tasks. Those tasks enabled port forwarding through Windows’ built-in netsh interface portproxy functionality. Kaspersky provided an example forwarding local port 443 to an internal address and port. In the published indicator, the internal address is defanged as 10[.]0[.]12[.]101.
RDP and Active Directory abuse
Kaspersky describes several methods used to obtain elevated privileges and move through the environment. In one incident, the attackers exploited CVE-2019-0708, commonly known as BlueKeep, in an RDP implementation. The researchers observed evidence that the exploit was used to create a local account and add it to the Administrators and Remote Desktop Users groups.
The presence of this vulnerability in the attack chain makes asset inventory and RDP exposure important defensive priorities. The report does not state that every targeted system was vulnerable, nor does it identify a universal initial-access method for all incidents.
The group also requested Kerberos tickets using an unusual combination of Forwardable, Proxiable, and Renewable flags. After obtaining an account with sufficient privileges, the operators attempted to replicate the Domain-Password object from the Active Directory database. Kaspersky identifies this activity as DCSync, a method that can enable an attacker to obtain domain password hashes while impersonating a domain controller.
According to the researchers, the combination of elevated privileges, replicated password data, and long-lived Kerberos tickets supported continued access to resources and ultimately the compromise of domain controllers and the wider Active Directory environment. Kaspersky also references attempts to compromise AD CS in its network-detection coverage, but the supplied research does not provide enough detail to describe a specific AD CS exploitation sequence.
Detection and investigation priorities
Organizations should correlate identity, Exchange, endpoint, RDP, and network telemetry rather than investigate each signal in isolation. High-value review areas include:
- VPN logins using valid accounts from unusual source networks, including unexpected Russian or European hosting infrastructure and Cloudflare WARP-associated addresses.
- Unexpected .NET assemblies, web-path behavior, or in-memory activity on Microsoft Exchange servers.
- Access to GitHub repositories or downloads of archives followed by execution of deceptively named binaries.
- DNS or proxy access to
*[.]devtunnels[.]msdomains from servers that do not normally publish services externally. - RDP virtual-channel events 132 and 148 containing
rdp2tcpor unexplained random channel names. - New scheduled tasks created by unusual administrative processes, use of
atexec, and changes tonetsh interface portproxy. - Unusual Kerberos ticket flags, replication requests involving the Domain-Password object, and attempts to perform DCSync.
Kaspersky lists several of its own detection rules and products for these behaviors, including detections for suspicious .NET assembly loading through PowerShell reflection, tunnel-domain access, possible Impacket activity, credential-dumping artifacts, and potential DCSync. Those product-specific detections are useful reference points, but organizations should translate the underlying behaviors into controls available in their own EDR, SIEM, NDR, and identity-monitoring platforms.
What organizations should do now
- Review recent VPN authentication activity for anomalous sources, impossible travel, unusual user-agent or device patterns, and access outside normal business requirements. Reset credentials when compromise is suspected and require phishing-resistant multifactor authentication where supported.
- Audit internet-facing Exchange servers for unexpected assemblies, modified ASP.NET configuration, suspicious VIEWSTATE-related activity, and web-access artifacts that cannot be explained by normal operations.
- Confirm that systems affected by CVE-2020-0688 and CVE-2019-0708 are remediated according to the organization’s supported Microsoft guidance and that obsolete or unnecessary RDP exposure is removed. The supplied research does not specify patch details.
- Restrict outbound access from servers, monitor access to developer-hosting and tunneling services, and alert when production systems use dev-tunnel infrastructure without an approved business reason.
- Enable and retain RDP operational logs, scheduled-task auditing, PowerShell logging, process creation telemetry, DNS records, and Active Directory replication auditing.
- Investigate suspicious RDP virtual channels, port-proxy rules, newly created privileged accounts, abnormal Kerberos tickets, and replication requests. If DCSync is confirmed, treat the domain as potentially compromised and follow an organization-approved identity recovery process.
- Use the supplied file hashes and filenames as starting points for retrospective searches, while recognizing that filenames can be changed and the listed hashes represent only observed samples.
Indicators reported by Kaspersky
The report lists these file hashes and associated filenames:
1dcafb7f8448683281106b06dd22409a—AdobeSync.exe1f3034b706c78b35d8e34044e68c693a—adobe_32.exe3ecd1cd627d0340c92901a478a7caad8—App_Web_Container_1.dll4aa9fb1bf9223dfcdac920759bc7a3c7—1c-office-plugin.exe,1cbroker.exe, ortrueconf.exe
Conclusion
Kaspersky’s findings show an intrusion model that blends credential abuse, server-side persistence, open-source tooling, legitimate tunneling services, RDP access, and Active Directory privilege escalation. The most effective defensive response is similarly layered: protect identities, harden Exchange and RDP, monitor tunneling and scheduled-task behavior, and treat unusual directory replication as a high-priority incident.
The precise delivery method for GhostContainer remains unconfirmed in the investigated cases. That uncertainty reinforces the need to examine both the initial access path and the later, better-defined behaviors across endpoints, network infrastructure, and Active Directory.
Sources
Securelist: NightEagle targets Russian companies, by Kaspersky Security Services.