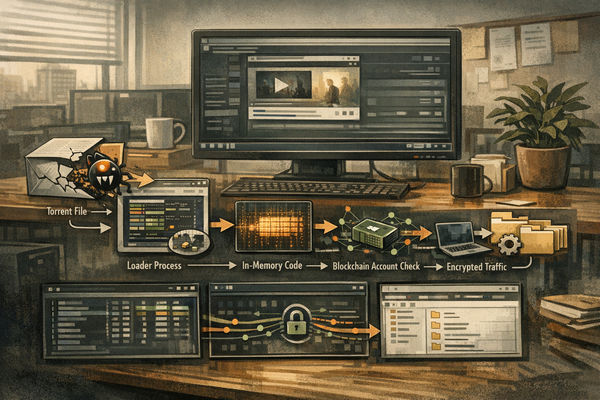
Ai Threat Intel Analysis MovieReaper: How Torrent Files Hide a Modular Trojan Securelist details MovieReaper, a multi-stage Windows Trojan distributed through compromised torrent files and using Solana to conceal its C2.
Ai Threat Intel Analysis How Pay-Per-Install Malware Hides Behind Trusted Downloads Palo Alto Unit 42 traced a pay-per-install campaign that used gaming videos, SEO poisoning and a shared loader to deliver multiple malware families.
Ai Threat Intel Analysis AI-Enabled Intrusions Target Latin American Organizations Unit 42 details two Latin American intrusion clusters using LLM-assisted workflows, SOCKS5 tooling, data theft, and exposed infrastructure.
Ai Threat Intel Analysis Mirage Kitten Targets Developers With Cross-Platform RATs Securelist details Mirage Kitten campaigns using NodeRabbit and PollCat backdoors in trojanized coding assessments aimed at aviation and FinTech.
Ai Threat Intel Analysis BREEZE COMET: How Brazil’s Payment Systems Were Targeted Google Threat Intelligence and Mandiant detail BREEZE COMET’s intrusion path into Brazilian financial environments and outline defensive priorities.
Ai Threat Intel Analysis ICS Threats in Q2 2026: What Defenders Should Know Securelist’s Q2 2026 telemetry shows declining overall ICS detections but rising email, ransomware, worm, and malicious-document activity.
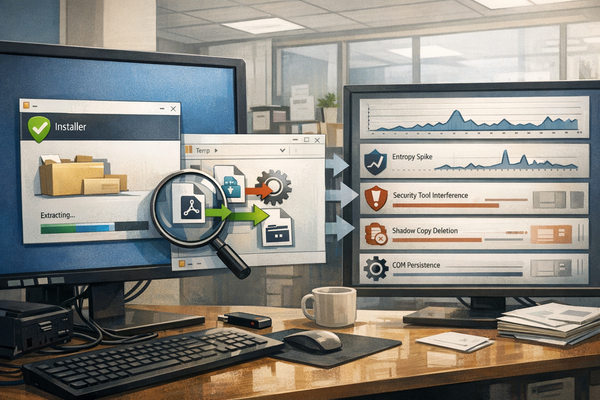
Ai Threat Intel Analysis AI-Enabled Malware: What Defenders Need to Know Unit 42’s analysis finds that AI is accelerating malware development, but conventional behavioral, endpoint, and sandbox defenses still detect the resulting code.