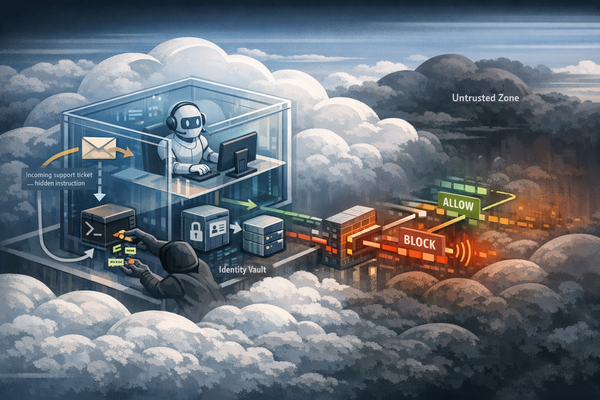
Ai Threat Intel Analysis AWS AgentCore Harness: When Prompt Injection Reaches Credentials Unit 42’s testing shows how default AgentCore Harness tools can turn prompt injection into credential exposure, with practical controls for AWS operators.
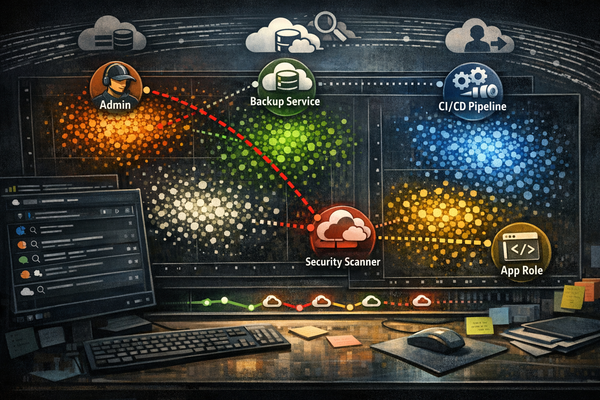
Ai Threat Intel Analysis Behavioral Mapping Brings Context to AWS Identity Detection Palo Alto Unit 42 shows how CloudTrail behavior can reveal functional identity roles and improve detection of anomalous AWS activity.
Ai Threat Intel Analysis September 2026 Microsoft Patch Tuesday: What to Prioritize Cisco Talos identifies two exploited flaws and a broad set of high-priority Microsoft vulnerabilities, with Snort coverage for selected attack attempts.
Ai Threat Intel Analysis SPIFFE/SPIRE: When Node Compromise Breaks Workload Identity Palo Alto Unit 42 shows how root access to a Kubernetes node can undermine SPIFFE/SPIRE workload identity and expose co-located service credentials.
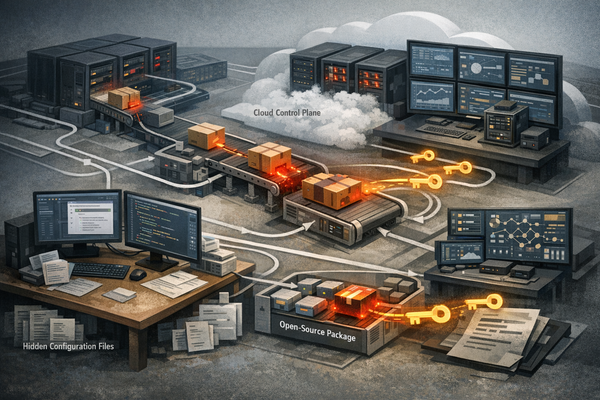
Ai Threat Intel Analysis How Agentic AI Is Reshaping the Threat Landscape Google Threat Intelligence and Mandiant report that adversaries are combining AI agents, stolen credentials, supply-chain abuse, and cloud hijacking.
Ai Threat Intel Analysis How AI Agents Compressed an Enterprise Intrusion Unit 42 details an AI-assisted enterprise intrusion that automated reconnaissance, credential theft, pipeline abuse and cloud takeover.
Ai Threat Intel Analysis BREEZE COMET: How Brazil’s Payment Systems Were Targeted Google Threat Intelligence and Mandiant detail BREEZE COMET’s intrusion path into Brazilian financial environments and outline defensive priorities.