Security News WordPress Issues Patch for Critical Flaw That Can Enable Code Execution on Some Servers TheHackerNews
Security News Malicious npm Package Poses as Twilio Bug-Bounty Probe, Can Exfiltrate Credentials TheHackerNews
Security News Microsoft Takes Down EvilTokens Device-Code Phishing Service Tied to 12,000 Inbox Compromises TheHackerNews
Security News Critical Bifrost AI Gateway Flaw Lets Attackers Run Commands Without Credentials TheHackerNews
Security News Researcher Drops BigDiskBuster Zero-Day PoC That Blocks Microsoft Defender Updates TheHackerNews
Security News EvilTokens PhaaS disrupted after compromising 12,000 Microsoft accounts BleepingComputer
Security News New CVSS 10.0 VeloCloud Orchestrator Flaw Actively Exploited in Certificate-Based Setups TheHackerNews
Security News New Linux Kernel Flaw Gives ARM64 KVM Guests Read-Write Access to Host Memory TheHackerNews
Security News SharePoint Flaw Initially Listed as Spoofing by Microsoft Enables Authenticated RCE TheHackerNews
Security News Malicious npm Package indexed-btree Hid Its Loader in Runtime Code Before Removal TheHackerNews
Security News SideCopy Broadens India Targeting to Academia With ReverseRAT Spear-Phishing TheHackerNews
Security News One Hidden Meta Muse Setting Could Let Attackers Turn the AI Assistant Into a Backdoor TheHackerNews
Security News WordPress Comment2Shell Flaw Can Turn Anonymous Comment XSS Into RCE via Admin Session TheHackerNews
Security News Zyxel and Veeam Flaws Under Active Exploitation With Command and SYSTEM Access TheHackerNews
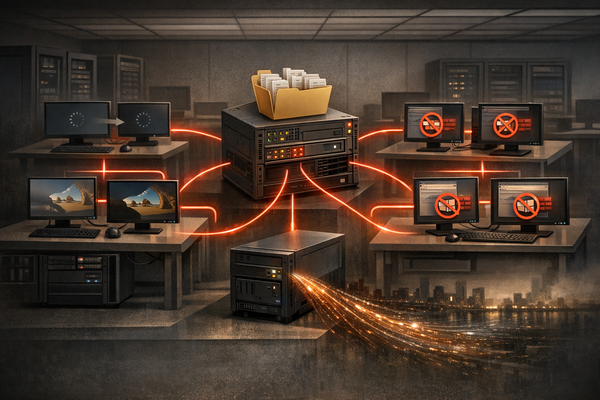
Ai Threat Intel Analysis PAYLOAD ransomware turns Active Directory into an attack tool Kaspersky’s analysis shows how PAYLOAD used trusted Active Directory Group Policy to disrupt a manufacturing environment without Windows encryption.