
How a Noisy Third-Party Intrusion Reached a European Bank
A European bank’s incident shows how weak third-party access controls, credential abuse, and noisy reconnaissance can create serious exposure.
A European bank’s recent intrusion illustrates an uncomfortable security reality: an attack does not need advanced malware or highly covert tradecraft to create a serious incident. According to Palo Alto Unit 42, the compromise developed from weaknesses in third-party access, authentication controls, and basic security hygiene.
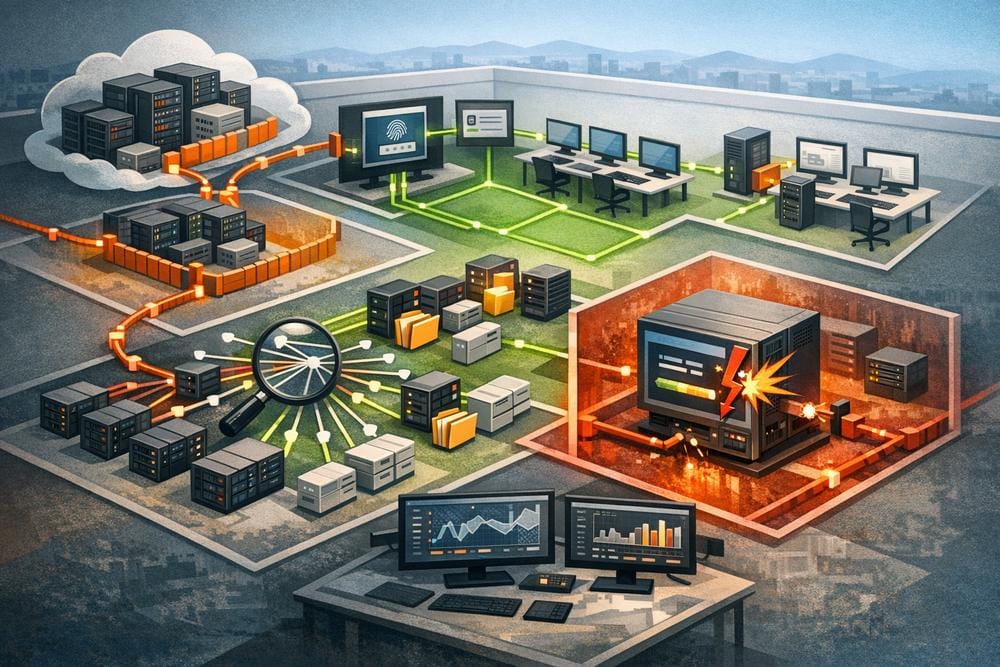
The incident involved unauthorized VPN-based access attempts over several months. After obtaining credentials, the attacker entered through a third-party-managed external gateway appliance that was not configured to enforce strict authentication. Inside the environment, the intruder conducted broad network reconnaissance, tested credentials against internal systems, scraped internal documentation, and attempted password-guessing campaigns against administrator accounts.
The activity was noisy rather than stealthy. That did not make it harmless. The attacker eventually attempted to exploit a remote code execution vulnerability affecting Windows Server Update Services (WSUS) on a central configuration-management server. Endpoint detection technology identified and contained the activity at that point, preventing the attacker from establishing the persistent foothold or lateral control described in the report.
What Palo Alto Unit 42 confirmed
Unit 42 investigated the incident after the bank’s security team detected unusual activity involving its central IT systems. The organization reports that the intrusion began through a third-party-managed external gateway appliance. The appliance was not properly configured to require strict authentication, and the attacker used compromised credentials to authenticate to internal systems.
The available research does not identify the third party, the gateway product, the compromised accounts, or the source of the stolen credentials. It also does not name the bank or provide indicators such as IP addresses, domains, usernames, hashes, or email addresses. Those details should therefore not be inferred from the incident narrative.
Once authenticated, the intruder performed extensive discovery across the internal network. Unit 42 describes multiple rounds of host and network scanning across a broad range of protocols, with interaction involving thousands of systems. The attacker also issued repeated authentication attempts and conducted several password-guessing campaigns over a period of months, concentrating on administrator accounts.
In parallel, the intruder targeted internal documentation and data shares. Automated web requests were used to retrieve individual pages and attachments from internal systems, while operational and network shares were enumerated. This combination suggests that the attacker was looking not only for reachable hosts, but also for information that could reveal system relationships, administrative procedures, or additional access opportunities.
The attack sequence
The incident can be understood as a series of access and discovery stages rather than a single exploit.
- Third-party entry point: The attacker reached the bank’s environment through a third-party-managed external gateway appliance. Strict authentication was not enforced, and compromised credentials were used to authenticate.
- Internal discovery: After gaining access, the intruder scanned hosts and networks across many protocols. The activity covered a large number of systems and was repeated in multiple reconnaissance rounds.
- Credential testing: The attacker launched password-guessing activity against internal systems, with administrator accounts receiving particular attention.
- Information gathering: Automated requests were used to browse internal documentation, retrieve attachments, and enumerate operational and network shares.
- Attempted expansion: The attacker eventually targeted the bank’s WSUS server, a central system responsible for software distribution. Unit 42 reports that the intruder attempted to exploit a remote code execution vulnerability on that server.
- Detection and containment: Cortex XDR detected the unauthorized code-execution activity and contained the threat before it could escalate into the persistent access or lateral movement described in the report.
This sequence matters because each stage created observable opportunities for intervention. The initial authentication event could have been challenged by stronger identity controls. Scanning and credential testing could have generated useful alerts. Documentation scraping could have been detected through web and file-access telemetry. Finally, endpoint controls interrupted the attempted expansion on a high-value management server.
Why the activity was still dangerous
Unit 42 assessed that the behavior did not resemble a highly sophisticated threat actor. The volume of scanning, repeated login attempts, and use of common system identifiers pointed, in the researchers’ assessment, to an opportunistic attacker seeking to compromise multiple systems. The intruder appeared to make little effort to conceal the activity or avoid detection.
That assessment should not be confused with a finding that the incident was low risk. An attacker who can use valid credentials and reach internal systems may be able to learn how an environment is organized, identify privileged accounts, locate sensitive operational material, and discover systems that provide broader control. In this case, the targeted WSUS server was especially important because it handled software distribution across the bank.
The research does not report that the attacker successfully established persistence, deployed a backdoor, moved laterally across the environment, or exfiltrated data. Unit 42’s investigation found no additional attacker presence or persistent backdoors after its review. The outcome was therefore shaped by both the limits of the intrusion and the organization’s response.
Detection and response lessons
The bank’s initial detection triggered an internal response, followed by a broader investigation by Unit 42. The researchers conducted threat hunting and a forensic review of endpoint telemetry across approximately thousands of systems, along with logs from dozens of Windows and Linux servers. The report does not provide an exact system count in the supplied material.
That review was important because stopping one suspicious process does not by itself establish that an environment is clean. Investigators need to determine whether the same credentials were used elsewhere, whether an attacker created persistence, and whether other hosts show related activity. In this case, Unit 42 reports that no additional attacker presence or persistent backdoors were found.
Bank leadership then reviewed the exposed documentation and rotated all compromised credentials. Unit 42 says those actions neutralized the threat. The bank also expanded its defensive coverage by deploying additional Cortex XSIAM and Cortex XDR licenses and broadening its incident-response retainer service. Those product and service decisions are specific to the reported organization; other defenders should treat them as context rather than a universal prescription.
What organizations should do now
Strengthen third-party access. Treat vendor-managed gateways, remote-support systems, and other externally managed infrastructure as part of the organization’s attack surface. Require explicit authentication controls, document who owns each access path, review accounts regularly, and remove access that is no longer justified. Third-party access should be subject to the same identity, logging, and response expectations as internally managed access.
Prioritize strong identity protection. Enforce multi-factor authentication for VPN and other remote-access paths where supported, especially for administrators and third-party users. Review authentication policies for legacy or exceptional paths that may not receive the same protections as standard access. Monitor for repeated failures, password guessing, unusual source locations, and successful logins that follow abnormal authentication patterns.
Watch for noisy reconnaissance. Broad host scanning, unusual protocol activity, repeated connections to many internal systems, and enumeration of network shares can be valuable signals even when they do not involve malware. Establish baselines for administrative discovery and investigate activity that is inconsistent with a user’s role or normal operating pattern.
Protect documentation and shares. Internal documentation can reveal architecture, operational procedures, hostnames, and access dependencies. Limit who can retrieve sensitive pages and attachments, log bulk or automated access, and review permissions on operational and network shares. Documentation systems should not be treated as harmless simply because they are not production databases.
Secure management infrastructure. Systems that distribute software or configuration deserve heightened monitoring and rapid patch management. Confirm that WSUS and other central management servers are covered by endpoint detection, have tightly limited administrative access, and generate alerts for unauthorized code execution or unexpected administrative activity. The supplied research identifies the WSUS issue as a remote code execution vulnerability but does not provide a CVE number or remediation details.
Build an investigation-ready telemetry set. Retain VPN and gateway authentication logs, identity-provider events, endpoint process telemetry, server logs, web access records, file-share activity, and administrative changes. Correlating these sources can help distinguish an isolated failed login from a sustained campaign that progresses from access to discovery and attempted expansion.
Prepare for rapid containment. Maintain a tested process for disabling or rotating compromised credentials, isolating endpoints, restricting third-party access, and preserving evidence. Threat hunting should extend beyond the initially detected host and include searches for related authentication, scanning, and persistence activity across the environment.
What remains unknown
The supplied Unit 42 account does not identify the attacker, establish a named threat-actor attribution, disclose how the credentials were originally compromised, or state whether data was removed from the environment. It also does not provide a CVE identifier for the WSUS vulnerability, detailed exploitation steps, specific indicators of compromise, or a formal MITRE ATT&CK mapping. Those omissions limit how precisely external organizations can reproduce the investigation, but they do not reduce the practical value of the control lessons.
Conclusion
This incident demonstrates how third-party exposure and weak authentication can provide a path into a complex enterprise without sophisticated tooling. The attacker’s broad and conspicuous behavior created multiple detection opportunities, while endpoint protection and follow-up threat hunting helped prevent the intrusion from becoming a persistent compromise. For banks, MSPs, and other organizations, the central lesson is straightforward: strong identity controls, disciplined third-party governance, timely patching, useful telemetry, and rapid response remain effective against unsophisticated attacks as well as more capable adversaries.