
Q3 2026 Threat Trends Across Windows, macOS and IoT
Securelist’s Q3 2026 review shows ransomware, software supply-chain attacks, macOS spyware and exposed IoT services driving cross-platform risk.
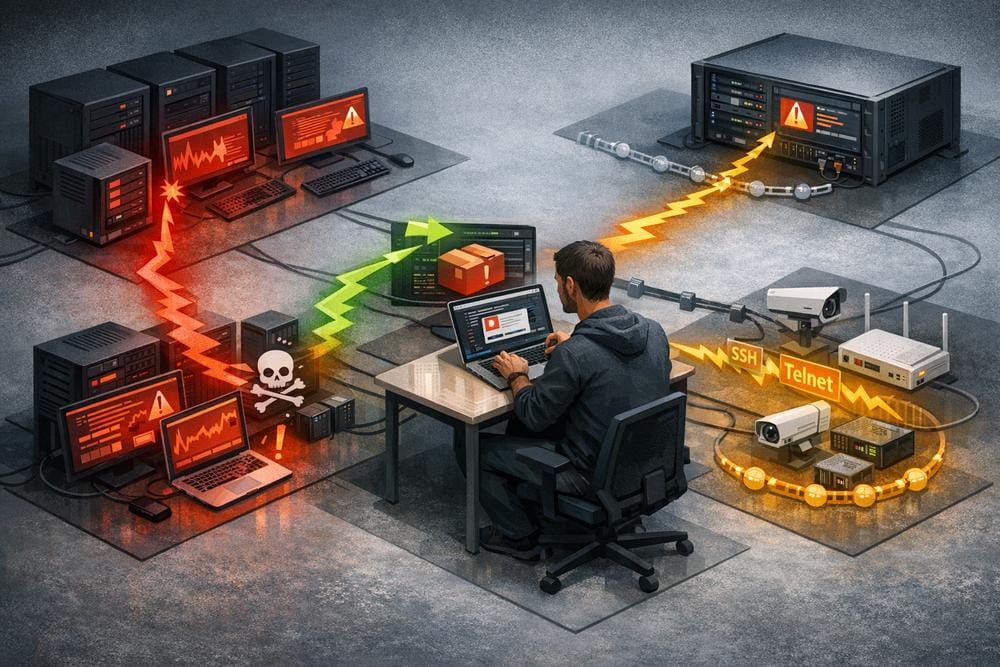
Threat activity in the third quarter of 2026 was distributed across familiar and emerging attack surfaces rather than concentrated in one malware category. Securelist’s review of non-mobile threats found sustained ransomware activity on Windows environments, continuing attacks against internet-facing vulnerabilities, malicious software packages affecting macOS users and other platforms, and persistent probing of exposed IoT services.
The report, published by Securelist, is based primarily on detection verdicts returned by Kaspersky products and on statistical data shared by users who consented to its collection. That methodology makes the figures useful for understanding activity visible to Kaspersky’s telemetry, but they should not be treated as a complete measurement of global incidents. The data also does not establish that every detection represented a successful compromise.
The quarter in numbers
Kaspersky products blocked more than 311 million attacks launched from online resources during Q3 2026. Web Anti-Virus responded to nearly 47 million unique links, while File Anti-Virus blocked more than 23 million malicious and potentially unwanted objects. The report also records 4,470 new ransomware variants, more than 81,000 users encountering ransomware attacks, and more than 217,000 users targeted by cryptocurrency miners.
These figures describe security-product detections, not a count of confirmed breaches. They nevertheless point to a broad defensive burden: organizations must manage endpoint protection, internet exposure, software dependencies, remote-access infrastructure and unmanaged devices at the same time.
Ransomware remained an access-and-impact problem
Securelist recorded 81,556 unique users protected from ransomware attacks during the quarter. Three new ransomware families and 4,470 new variants were detected, with the number of variants exceeding the previous quarter’s total by more than 1.5 times. Qilin accounted for 15% of ransomware victims whose data appeared on the data-leak sites reviewed by the researchers. In the same analysis, Qilin represented 15.39% of victims listed across the groups’ leak sites, followed by The Gentlemen at 7.89% and Deadlock at 4.46%.
Those rankings reflect victims added to leak sites, not the total number of organizations attacked. They also do not prove that every listed victim was encrypted or that the same operational model was used in every case. Securelist’s assessment does, however, show that extortion activity continued to be measured through both encryption-related detections and public claims of data theft.
The report describes several law-enforcement developments involving ransomware operations. The creator and lead administrator of the Ransom Cartel ransomware-as-a-service operation received a 16-year prison sentence. A member of the Ryuk group received two years in prison and three years of supervised release, while a Conti member received a four-year sentence. These cases confirm disruption and prosecution activity, but Securelist does not present them as evidence that ransomware risk has materially subsided.
Vulnerabilities created multiple routes into enterprise networks
Securelist highlights a series of vulnerabilities that appeared in CISA’s Known Exploited Vulnerabilities Catalog or were discussed in connection with ransomware activity. Researchers reported that Qilin exploited CVE-2026-0257 in Palo Alto Networks firewall software. According to the report, the flaw allowed authentication bypass and network compromise without valid accounts.
The report also lists CVE-2026-15409 and CVE-2026-15410 in SonicWall SMA1000 remote-access gateways. CISA identified these vulnerabilities as actively exploited by ransomware groups, although CISA did not specify the groups involved. Researchers linked the activity to INC Ransom, but that connection is an assessment rather than a confirmed attribution presented as fact.
Other vulnerabilities identified in the report include:
- CVE-2026-45659: Microsoft SharePoint Server, allowing an authenticated low-privileged attacker to achieve remote code execution.
- CVE-2025-60710: Microsoft Windows, enabling local privilege escalation.
- CVE-2026-59310: VMware vCenter, enabling unauthenticated remote code execution.
- CVE-2025-14733: WatchGuard Firebox, also enabling unauthenticated remote code execution.
- CVE-2026-63077: JetBrains TeamCity, where an authentication bypass through the agent polling protocol could allow operating-system commands to run with the privileges of the TeamCity server process.
The TeamCity issue is particularly relevant to build and release environments because server-level access can expose configurations, credentials and CI/CD pipelines. The supplied research does not describe a specific victim, exploit chain or confirmed compromise for each vulnerability. Administrators should therefore treat the list as a prioritization signal for exposure review and remediation, not as evidence that every listed product was compromised in every environment.
macOS risk increasingly includes trusted software ecosystems
The macOS findings show that attackers were not limited to standalone downloads. Securelist reports several supply-chain incidents involving npm, PyPI and Cargo packages. On July 11, a malicious version of the npm package jscrambler was published. Its payload was an infostealer written in Rust that targeted cryptocurrency wallets, service secrets, browser data, MCP server configurations and API keys associated with AI agents.
In August, malicious activity involving the Rust crates arrayref, internment and append-only-vec delivered a Rust backdoor to affected devices. In September, malicious versions of the MemTensor npm and PyPI packages delivered a Go backdoor aimed at secrets, service configurations and API tokens. The report states that these payloads targeted macOS systems along with other platforms; it does not provide a complete list of affected operating systems or identify confirmed victims.
Securelist also describes PamStealer, identified by Jamf researchers. Its notable behavior was the use of Pluggable Authentication Modules to verify the administrator password entered by a user. The report does not specify the broader persistence mechanism, infrastructure or command-and-control design of PamStealer.
Another macOS backdoor, Overlord, was distributed through fake Zoom installers. Securelist says it included spyware capabilities such as microphone eavesdropping, camera monitoring, screen capture and keystroke logging. That behavior raises the impact of a successful installation beyond credential theft, but the report does not establish how widely the campaign spread or identify particular victims.
The report also notes continued detections of Amos, including both stealer and backdoor functionality, increased detections involving Ngrok—a legitimate network tunneling tool with both legitimate and malicious uses—and an updated MacSync crypto stealer and backdoor with a substantially changed payload-delivery method. Securelist does not provide enough detail to conclude that Ngrok detections were inherently malicious; defenders should investigate its use in context.
IoT exposure continued through remote administration services
Kaspersky’s IoT statistics are based on attacks against its honeypots. In Q3 2026, devices attacking those honeypots over SSH represented 18.42% of the attacking devices by unique IP address. The report says Mirai’s share of delivered IoT threats declined while other botnet threats grew.
SSH activity was most commonly associated with the Netherlands, Bulgaria and the United States in the reported distribution. Bulgaria’s share increased fourfold compared with the previous quarter. For Telnet attacks, Pakistan accounted for 47.73% and China for 33.83% of the reported source distribution. These geographic results identify the apparent locations of attacking devices, not the identities or locations of the operators. Compromised devices, proxies and other intermediaries can affect such measurements.
The observed activity is consistent with the continuing risk posed by internet-exposed management services. However, the supplied research does not describe a specific exploit, default credential set, persistence method or command-and-control protocol for the IoT threats. Organizations should avoid inferring those details from the geographic statistics alone.
What organizations should do now
- Prioritize exposed systems. Inventory internet-facing firewalls, remote-access gateways, SharePoint servers, VMware vCenter, WatchGuard Firebox appliances and TeamCity installations. Check whether affected products and versions are present, then apply vendor-provided fixes or other approved remediation as soon as possible.
- Protect the software supply chain. Review recent npm, PyPI and Cargo package changes, pin dependencies where appropriate, require code review for updates and use software composition analysis. Treat unexpected access to API keys, browser stores, wallet files or build credentials as a high-priority investigation.
- Strengthen macOS application controls. Restrict software installation to trusted sources, monitor fake or unauthorized installers and investigate applications that request administrator credentials unexpectedly. EDR telemetry should cover process launches, credential prompts, camera and microphone access, screen capture and unusual access to browser or developer-tool secrets.
- Reduce ransomware blast radius. Maintain tested offline or otherwise isolated backups, separate administrative accounts from ordinary user accounts, and monitor unusual authentication, privilege changes, mass file modifications and access to backup infrastructure.
- Harden IoT management services. Remove unnecessary internet exposure for SSH and Telnet, place devices behind access controls, disable unused services, enforce unique credentials and update firmware according to the manufacturer’s guidance. Segment IoT networks from business-critical systems.
- Hunt for credential and secret access. Review endpoint and CI/CD logs for unexpected reads of browser data, API tokens, wallet files, package-manager credentials and service configurations. Rotate exposed credentials after containment and assess where the same secret was reused.
Detection teams should also correlate endpoint alerts with vulnerability exposure and identity events. A suspicious package installation, an unexpected administrator-password prompt, or new remote-access activity may be more significant when it occurs on a system running an exposed service. The report does not supply malware hashes, domains, IP addresses, MITRE ATT&CK mappings or detection signatures, so organizations should obtain those details from their own telemetry, security vendors and incident-response providers rather than inferring them.
Conclusion
Securelist’s Q3 2026 data presents a cross-platform threat picture: ransomware groups continued to exploit enterprise weaknesses, software packages became delivery vehicles for credential theft and backdoors, and IoT honeypots recorded ongoing SSH and Telnet activity. The most practical response is not a single malware-specific control. It is disciplined exposure management, supply-chain governance, endpoint visibility, credential protection, segmentation and recovery testing. The findings establish where defenders should focus attention, while campaign scope, victim identities and several technical details remain unconfirmed in the supplied research.
Sources
Securelist: IT threat evolution in Q3 2026 — non-mobile statistics