
PerfectPioneer and KUKURAT Target Southeast Asian Governments
Unit 42 details a stealth-focused espionage campaign using custom RATs, phishing, DLL sideloading, log-on scripts and HTTP/3 C2.
Palo Alto Networks’ Unit 42 has analyzed a multi-stage cyberespionage campaign targeting Southeast Asian government organizations with two previously undocumented remote access trojans: PerfectPioneer and KUKURAT. The activity, tracked by Unit 42 as TGR-STA-0049, combines targeted phishing, compromised servers, DLL sideloading, shellcode, credential collection and covert command-and-control communications over HTTP/3.
Unit 42 reports that the activity has affected government entities and other high-value organizations across Southeast Asia, South America and Europe, with the campaign described in this research dating from at least July 2025. The organization also links the broader activity to earlier deployments of the Squidoor backdoor, also known as FINALDRAFT. Those connections are assessments from Unit 42 rather than independently established attribution in the supplied research.
The campaign is notable less for a single delivery mechanism than for the way its components are designed to preserve access while limiting visibility. PerfectPioneer provides a broad, integrated feature set, while KUKURAT moves toward a modular architecture in which capabilities are fetched and loaded only when needed. Both malware families use HTTP/3 or related HTTP protocols for C2, giving defenders a particularly important network-monitoring problem: distinguishing malicious QUIC traffic from legitimate encrypted web activity.
Two malware families, an evolving operation
PerfectPioneer is a custom malware family written in Go. Unit 42 identified six variants, including one it examined in depth under the project name “newhttp3.” The variants share a common development lineage but differ in communication methods and capabilities. Some are comparatively lightweight, while others include credential harvesting, process manipulation and network tunneling functions.
KUKURAT appeared later in the operation. Unit 42 observed it in compromised environments in March 2026 and identified two variants: one using HTTP/2 and another using HTTP/3. Unlike PerfectPioneer, KUKURAT places most post-compromise functionality in separate modules. The base program can retrieve and load modules dynamically, reducing the amount of capability visible in the main executable and allowing the operators to change the toolset without replacing the entire agent.
Unit 42 describes KUKURAT as supporting modules for screenshots, keylogging, file operations, shell execution, process management, host and port scanning, SOCKS tunneling, privilege elevation and lateral movement. The research also identifies modules associated with PsExec-style remote execution, SMB credential brute-forcing and Beacon Object File loading. These findings describe capabilities present in the analyzed code; the supplied research does not establish that every capability was used against every victim.
How access and execution were established
The campaign used two broad access paths. The primary vector observed by Unit 42 involved exploitation of vulnerable, unpatched Microsoft Exchange and web servers, followed by deployment of web shells. The observed web-shell tooling included ASPXSpy, Godzilla, Bysunue.aspx and Suo5, with both custom and publicly available variants identified.
From a web shell, the operators could execute reconnaissance commands and launch PerfectPioneer on a compromised server. The supplied research does not identify a specific vulnerability or CVE associated with those intrusions, so organizations should not infer that a particular Exchange or web-server flaw was responsible.
Phishing served as a secondary route. Unit 42 observed decoy PDFs, lookalike domains and files presented with PDF icons. In the documented execution pattern, a user opening the apparent document instead launched malware, which then displayed a decoy PDF to preserve the appearance of a legitimate government notice.
PerfectPioneer was also delivered through decoy installers and DLL sideloading. In the sideloading chain, a modified legitimate executable contained XOR-encrypted shellcode, while a malicious loader DLL accompanied it. When the executable ran, it loaded the DLL; the DLL read and decrypted the embedded shellcode, which then deployed the payload in memory.
Unit 42 additionally observed a decoy installer that displayed a legitimate GlobalProtect installation process while writing and executing PerfectPioneer in the background. That observation demonstrates how trusted software branding can be used as a social-engineering cover, but it does not indicate that the legitimate product itself was compromised.
Persistence, movement and credential collection
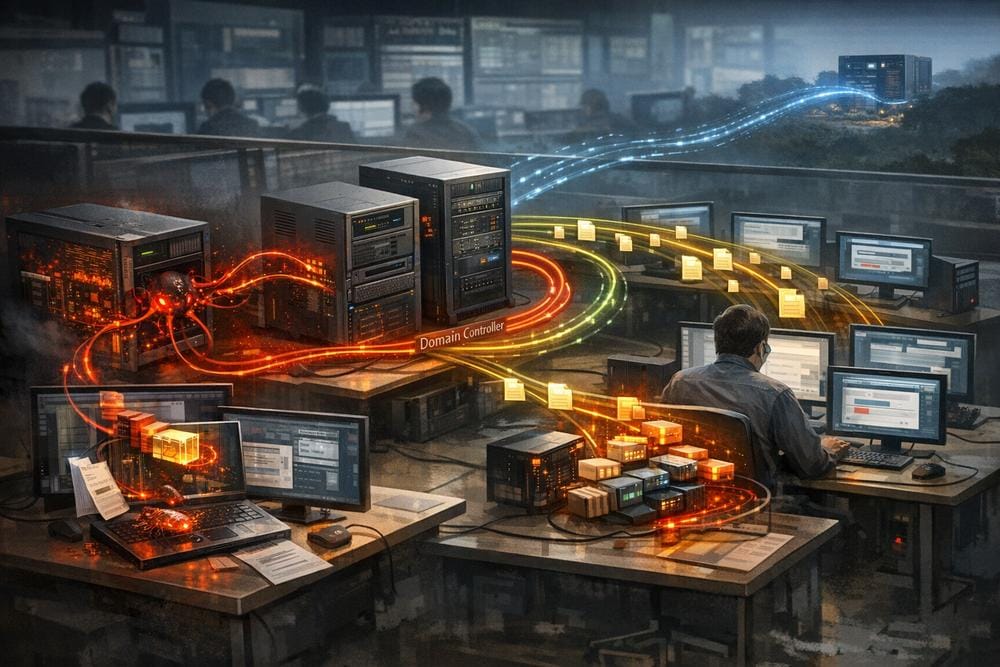
The research documents multiple persistence and propagation mechanisms. PerfectPioneer can establish local persistence through a Windows Registry Run key and a shortcut in the user’s Startup folder. KUKURAT was also distributed through manipulated domain log-on scripts. After the attackers compromised a domain controller, the scripts executed when users authenticated and triggered the download and execution of KUKURAT on their endpoints.
Unit 42 further observed the use of PsExec, Windows Management Instrumentation and Windows Remote Management for movement across networks. A separate executable associated with KUKURAT, named PsExecService.exe, registered a local service and created a named pipe. The service supported shell execution, file transfer and directory listing, and included a five-minute inactivity timer intended to remove the service and related artifacts.
Credential access included LSASS memory dumping and Directory Service Replication, according to Unit 42. KUKURAT’s analyzed capabilities also included SMB credential brute-forcing. The research describes these functions as part of the operators’ broader effort to collect credentials, move from directory infrastructure to endpoints and obtain sensitive information. It does not provide a complete account of the credentials or records taken from each organization.
HTTP/3 creates a monitoring blind spot
Both malware families use HTTP/3 as a primary C2 option, while PerfectPioneer can fall back to HTTP/2 if the preferred connection fails. HTTP/3 runs over QUIC and UDP, commonly using UDP port 443. Unit 42’s assessment is that many legacy inspection systems remain more capable with TCP traffic than with UDP-based web communications, potentially allowing malicious QUIC connections to receive less scrutiny.
PerfectPioneer’s representative variant communicates through registration, heartbeat, task retrieval and result-submission functions. KUKURAT similarly registers the host, sends periodic heartbeats and retrieves queued commands. Its registration data can include the hostname, username, integrity level, operating-system information, host IP address and a randomly generated agent identifier.
The endpoint paths are not, by themselves, sufficient for detection. Unit 42 reports that KUKURAT uses hashed equivalents of some paths during communication, further reducing the value of simple URL matching. The more durable detection opportunity is behavioral: unusual outbound QUIC from servers or workstations that do not normally need it, persistent heartbeat-like traffic, unexpected registration-style exchanges and encrypted UDP connections associated with newly created or unsigned processes.
Defense evasion built into the malware
PerfectPioneer includes an operational safeguard that Unit 42 calls isDangerousCommand. In two variants, the routine blocks commands considered destructive, disruptive or likely to generate forensic evidence. The blocked categories include disk destruction, broad deletion, shutdown actions, account manipulation, service disruption, firewall changes and certain encoded or download-and-execute patterns.
Unit 42 assesses that this mechanism helps prevent operators from accidentally creating noisy activity. The presence of Linux command syntax in the blocklist also suggests to the researchers that the developers may have been preparing a Linux version, although the supplied research does not confirm deployment of such a variant.
KUKURAT uses a different form of concealment: a configurable heuristic camouflage engine. It can generate decoy web requests, imitate selected Chrome-related Registry activity and create temporary files that are quickly removed. Each of the network, Registry and file-noise features can be enabled or disabled through C2 commands.
The malware also uses process supervision. In observed incidents, a watchdog communicated with KUKURAT through a named pipe and relaunched it when heartbeats stopped. Unit 42 saw one deployment placed under a directory structure historically associated with Cortex XDR, which the researchers interpret as an effort to appear less suspicious. That path is an observation from the analyzed incident, not evidence that the security product was responsible for the infection.
What organizations should do now
- Prioritize internet-facing servers. Verify that Exchange and web servers are fully updated, restrict administrative access, review exposed services and investigate unexpected web shells or newly created server-side scripts.
- Inspect domain log-on infrastructure. Audit log-on scripts, Group Policy-related changes and domain-controller activity. Alert on scripts that download or execute binaries on user endpoints.
- Strengthen phishing defenses. Block lookalike government domains where appropriate, detonate suspicious PDF-labeled executables, show true file extensions and restrict execution from user-writable locations.
- Monitor DLL loading. Look for legitimate applications loading unexpected DLLs, especially when the executable and library appear together in unusual directories. Correlate this with in-memory execution and shellcode-related endpoint alerts.
- Expand UDP and QUIC visibility. Record outbound UDP 443 by process, destination and user context. Establish a baseline for legitimate HTTP/3 use and investigate new QUIC clients, particularly on servers and administrative workstations.
- Hunt for persistence and supervision. Review Run keys, Startup-folder shortcuts, unfamiliar services, named pipes and watchdog processes. Pay particular attention to binaries stored in directories that imitate security-product paths.
- Protect credentials and privileged paths. Restrict access to LSASS, monitor directory replication activity, use phishing-resistant multifactor authentication and review unexpected SMB, PsExec, WMI and WinRM activity.
- Investigate in-memory and modular behavior. Endpoint telemetry should correlate module downloads, reflective or memory-based execution, unusual child processes, screenshot or keylogging access and file transfers rather than relying only on static malware signatures.
These are general defensive recommendations based on the behaviors described by Unit 42. The research does not provide a complete set of indicators in the supplied material, nor does it identify a CVE that organizations can use as a single filtering criterion.
What remains unknown
The supplied research does not name individual victims, disclose the C2 domains or IP addresses, establish a definitive national attribution or quantify the amount of data exfiltrated. It also does not confirm that every capability present in PerfectPioneer or KUKURAT was used during each intrusion. Those limitations matter when translating malware analysis into incident conclusions: a matching behavior can justify investigation without proving that the full campaign is present.
Conclusion
Unit 42’s analysis presents TGR-STA-0049 as a technically adaptive espionage operation built around stealth, persistence and flexible collection. PerfectPioneer and KUKURAT give the operators several ways to enter environments, maintain access, gather credentials and move laterally. Their use of HTTP/3 and configurable activity camouflage raises the detection bar, but it also creates practical hunting opportunities around unexpected QUIC, log-on-script changes, DLL sideloading, named-pipe supervision and abnormal credential access.