
PAN-OS CVE-2026-0257 Exploitation: What Defenders Need
Unit 42 reports active PAN-OS CVE-2026-0257 exploitation linked to ransomware operations. Here is what defenders should investigate and do now.
Palo Alto Networks Unit 42 is reporting active exploitation of CVE-2026-0257, an authentication-bypass vulnerability affecting the portal and gateway components used by GlobalProtect on vulnerable PAN-OS versions. The flaw can allow an unauthorized attacker to bypass security controls and initiate a VPN connection.
Unit 42’s reporting describes activity that has developed from probing and attempted VPN access into ransomware intrusion operations. The research names Spikey Scorpius, also known as Qilin, and Tarnished Scorpius, also known as Inc, among the ransomware operators exploiting the vulnerability. Unit 42 also notes public reporting that attributes exploitation to actors using Settra ransomware, but does not present that attribution as its own confirmed finding.
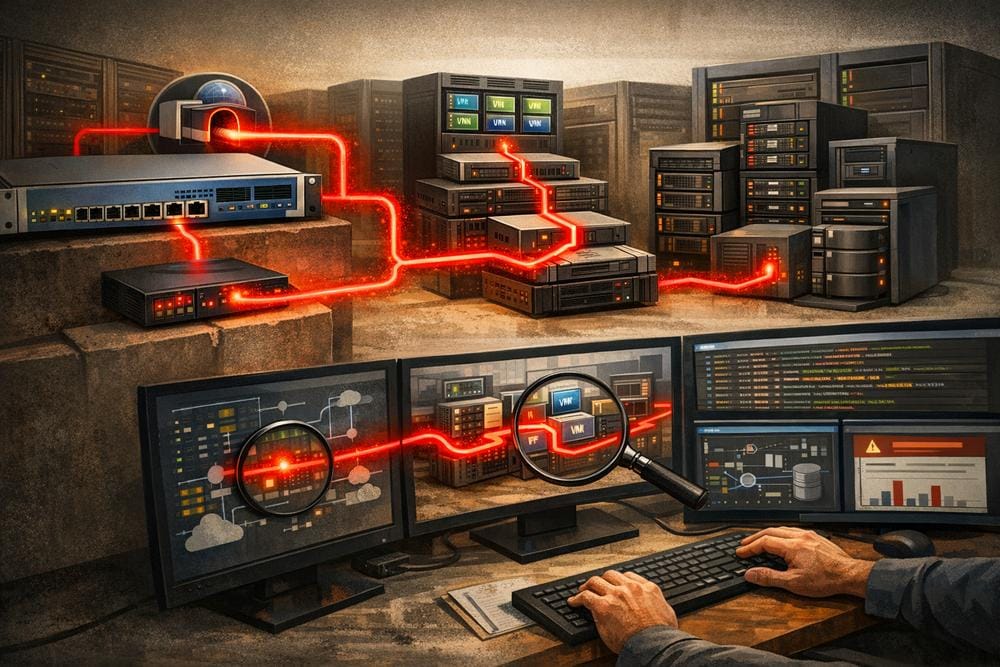
The immediate concern is not limited to the firewall itself. In cases where attackers successfully established a gateway-connected session, Unit 42 observed follow-on reconnaissance, lateral movement, credential-access activity and ransomware preparation. The research also documents a particularly consequential route into virtualization infrastructure, where attackers reached vCenter and then targeted virtualized domain-controller data. That sequence can move the impact of an edge-device compromise well beyond the initial VPN service.
What Unit 42 confirmed
According to Unit 42, an unidentified threat actor was actively attempting to exploit CVE-2026-0257 to access GlobalProtect. The vulnerability was added to the U.S. Cybersecurity and Infrastructure Security Agency’s Known Exploited Vulnerabilities catalog on May 13, 2026.
Only a small portion of the devices probed in the activity established VPN sessions. Unit 42 describes those successful connections as gateway-connected events. This distinction is important for triage: repeated scanning or failed attempts indicate exposure and targeting, while a successful gateway-connected event warrants an incident-response investigation.
Unit 42’s investigations began in early June 2026 and covered organizations in education, financial services, healthcare, high technology, hospitality, manufacturing, professional and legal services, government, transportation and logistics, utilities and energy, and wholesale and retail. The report identifies these as industries involved in the investigations; it does not publish a complete victim list.
The research does not establish that every organization probed was compromised. It also does not claim that every successful VPN session led to ransomware deployment. Organizations should therefore separate confirmed authentication or gateway events from attempted exploitation and from evidence of later intrusion.
How the reported intrusion sequence unfolded
The initial stage involved exploiting the authentication bypass to obtain access through GlobalProtect and establish a VPN session, including in circumstances where multi-factor authentication controls were bypassed. Unit 42 says that, after successful exploitation, the operators typically conducted internal network reconnaissance with dual-use remote monitoring and management tools.
The reported sequence then included lateral movement through Remote Desktop Protocol and Server Message Block. Attackers staged additional tools for credential harvesting and data exfiltration before moving toward ransomware deployment. These observations describe activity in ransomware-related investigations, not an assertion that the vulnerability itself automatically provides access to internal systems or deploys malware.
Unit 42 highlights a more advanced post-exploitation path involving the virtualization layer. In one notable case, attackers moved from a compromised VPN gateway to the vCenter management appliance. They then disabled the ESXi control identified in the report as execInstalledOnly and used a custom tool to perform offline credential dumping against a domain controller’s virtual disk, or VMDK.
This approach is significant because it targets the storage representation of a virtual machine rather than relying solely on activity inside the guest operating system. Unit 42 assesses that the method can bypass in-guest endpoint detection and response and other guest-level security controls, creating a route to domain-wide credentials. The report characterizes this as a highly sophisticated method; it does not provide the custom tool or operational instructions for reproducing it.
Unit 42 also observed attackers chaining the initial access with tools targeting Veeam backup infrastructure, including exploitation associated with CVE-2023-27532. The stated objective was to maximize impact. Defenders should treat backup systems as part of the affected attack surface rather than assuming that a firewall-focused investigation can be isolated from recovery infrastructure.
Indicators defenders can investigate
For activity before the public proof-of-concept release on May 29, 2026, Unit 42 recommends searching GlobalProtect logs for successful login connections associated with these source IP addresses:
23.128.228[.]6104.207.144[.]154146.19.216[.]119146.19.216[.]120146.19.216[.]125179.43.172[.]213185.195.232[.]139198.12.106[.]60202.144.192[.]47
The IP addresses are indicators reported by Unit 42 and should be treated as leads rather than proof of compromise. Logs should be retained and correlated with authentication results, session creation, administrator activity, endpoint alerts and network connections. Because infrastructure can change and not all activity will use the listed addresses, an absence of matches does not by itself clear an environment.
Unit 42 also identifies suspicious host identifiers and device names seen in successful gateway-connected events. These include:
aa:bb:cc:dd:ee:ff00:11:22:33:44:55WINDOWS-LAPTOP-001DESKTOP-GP01GP-CLIENT
For monitoring after the proof-of-concept release, Unit 42 recommends searching for successful gateway-connected events that match the hard-coded client configuration values reported in the proof of concept: an endpoint operating-system value of Microsoft Windows 10 Pro 64-bit and an empty source_user_info.domain field. These values should be used in context with session timing, source address, user identity and device history, since a match alone is not confirmation of malicious activity.
Management-interface exposure adds risk
During incident-response engagements connected with the Lunar Peak campaign, Unit 42 repeatedly observed GlobalProtect profiles mapped to HTTP or HTTPS services on firewall management interfaces. This configuration can unintentionally expose the management interface to the internet, particularly on ports 4443 and 3879.
This issue is separate from the authentication-bypass vulnerability, but it can increase the consequences of weak or unintended exposure. Administrators should verify whether management interfaces are reachable externally and review Interface Management profiles against the principle of least privilege. Unit 42 recommends an out-of-band HTTPS check to the management IP address on ports 4443 and 3879, followed by remediation using the organization’s official Palo Alto Networks configuration guidance.
What organizations should do now
- Confirm exposure and patch status. Review the official Palo Alto Networks security advisory for CVE-2026-0257, identify affected PAN-OS deployments and apply the available fix or documented workaround. The supplied Unit 42 report does not list vulnerable-version ranges, so teams should use the vendor advisory for product-specific applicability.
- Prioritize successful sessions. Search historical and current GlobalProtect logs for the listed IP indicators, suspicious host identifiers, device names and proof-of-concept client values. Escalate successful gateway-connected events for incident response, especially when they occurred on vulnerable systems.
- Expand the investigation beyond the firewall. Review VPN session times against RMM activity, RDP and SMB connections, unusual administrator actions, credential-access alerts, data-transfer events and ransomware-preparation signals.
- Inspect virtualization and backup infrastructure. Examine vCenter and ESXi administrative activity, changes involving
execInstalledOnly, access to virtual-disk files and unusual interaction with domain-controller VMDKs. Review Veeam systems for activity associated with CVE-2023-27532 and ensure backup credentials and management paths receive separate scrutiny. - Remove unintended management exposure. Audit GlobalProtect and Interface Management profiles. Restrict internet access to management services and confirm that only required administrative sources can reach them.
- Preserve evidence before making broad changes. Retain firewall, GlobalProtect, identity, endpoint, virtualization, backup and network telemetry. If a successful gateway event is associated with the reported indicators, activate incident-response procedures and coordinate containment with appropriate internal or external responders.
These are defensive recommendations based on the activity described by Unit 42. They do not establish that an organization has been compromised, and they should be adapted to local logging, business continuity and incident-response procedures.
What remains unknown
Unit 42 identifies an unidentified actor behind some observed exploitation and separately names ransomware operators associated with activity. The report does not establish that all exploitation attempts came from one actor or that every event can be attributed to Qilin, Inc or Settra. It also does not provide a complete list of victims, a universal post-exploitation sequence, or evidence that every successful VPN session resulted in lateral movement.
The report’s findings are updated over time. Its earlier executive summary stated that no post-access behavior or lateral movement had been identified at that point, while later reporting described such activity in ransomware investigations. Defenders should read those statements as reflecting different stages and observations within the campaign rather than as a contradiction about every affected device.
Conclusion
CVE-2026-0257 presents an edge-access risk with potentially serious downstream consequences when exploitation produces a working GlobalProtect session. Unit 42’s findings show why investigation should not stop at the firewall: ransomware operators may move through internal services, virtualization management and backup infrastructure. The most useful immediate actions are to patch or apply the vendor’s mitigation, hunt for successful gateway-connected events, review management-interface exposure and investigate adjacent systems when the indicators align.
Sources
Palo Alto Networks Unit 42: Threat Brief — Active Exploitation of PAN-OS CVE-2026-0257