
Operation ShadowCloud: GraphDoor Abuses Cloud C2
Securelist details GraphDoor, a modular backdoor that uses Microsoft Graph, SharePoint and Ably to collect data, deliver plug-ins and relay traffic.
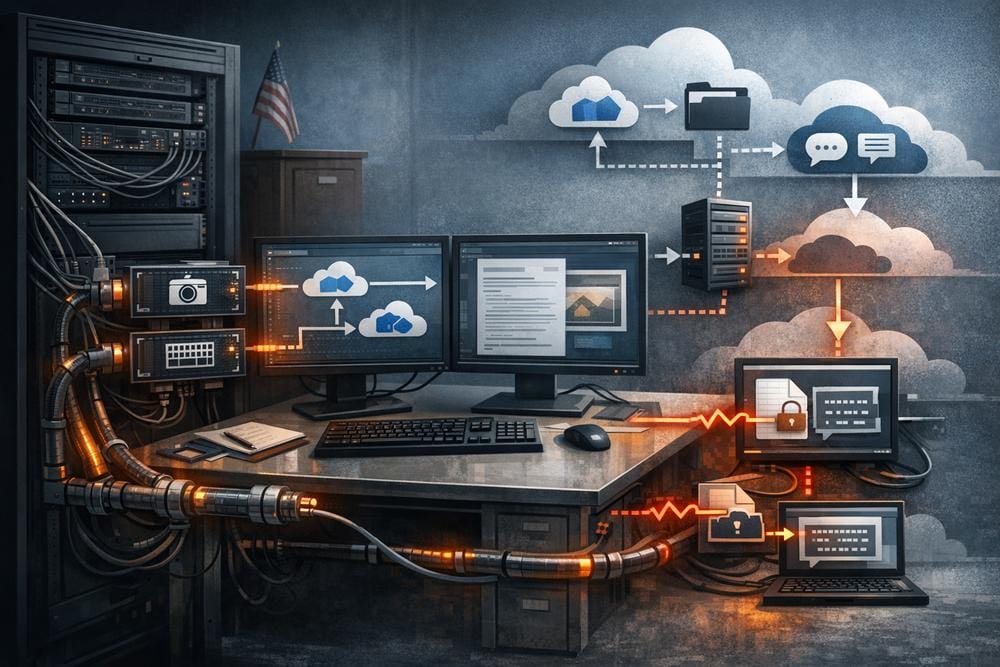
Operation ShadowCloud illustrates a difficult detection problem for organizations that rely heavily on cloud services: malicious traffic can use the same APIs and infrastructure as legitimate business applications. In its analysis, Securelist describes GraphDoor, a Windows backdoor that uses Microsoft Graph and SharePoint for command-and-control, while additional plug-ins extend its collection and networking capabilities through local loaders and the Ably messaging platform.
Securelist reports that the operation targeted government networks in Asia and Africa. The research describes a modular design rather than a single self-contained implant. GraphDoor gathers host information, obtains additional components on demand, receives victim-specific commands, and passes data between plug-ins through a named pipe. This architecture gives operators the ability to add functionality without replacing the main backdoor on disk.
What Securelist confirmed
GraphDoor creates a named pipe based on its process identifier, using a pattern equivalent to \\.\pipe\p<PID>. The backdoor and its plug-ins use that pipe to exchange status and collected information. It also creates an Intel_Log directory beneath C:\ProgramData, followed by a subdirectory named with a randomly generated GUID.
Before communicating with its operators, the malware collects network-adapter information, operating-system details, a generated victim identifier, public and private IP addresses, the username, host name, current execution directory, its own process ID and a list of running processes. Securelist says the resulting data is encrypted with AES, Base64-encoded and transmitted through the campaign’s cloud-based communication mechanism.
The backdoor resolves Windows APIs at runtime by hashing DLL and function names with DJB2. Securelist also observed an indirect invocation technique involving a vectored exception handler and deliberately raised exceptions. These mechanisms can complicate straightforward static analysis and may be useful behavioral signals when combined with the malware’s other activity.
How the cloud command channel works
GraphDoor first establishes TLS communication with login.microsoftonline.com over port 443. It authenticates an application rather than an interactive user, using embedded encrypted values that become an application identifier, client secret and tenant-related path component. If authentication succeeds, the implant receives an access token for Microsoft Graph.
It then connects to graph.microsoft.com and uses Microsoft Graph requests to interact with SharePoint. Securelist observed the malware uploading encrypted victim information as a file with a name resembling a JavaScript source-map file, using a dynamically generated eight-character victim code. The file is placed in a SharePoint document library through a Graph API request.
This model separates the malware from a conventional attacker-controlled command server. The network session may look like ordinary Microsoft 365 activity, and the content exchanged with the service is encrypted or encoded by the malware. The use of randomly generated victim identifiers also allows command and response material to be associated with an individual infected host without requiring a unique external domain for every victim.
GraphDoor retrieves plug-ins by querying a specific SharePoint list. Securelist identified modules named scr.ts, pr.ts and kl.ts, corresponding to screenshot capture, process enumeration and keylogging. The backdoor launches separate threads for these downloads and decrypts the modules after retrieval. It later queries another SharePoint list for files whose names begin with the host’s unique code. Only selected extensions are accepted, including .js, .swp, .tmp, .kmap and .pmap.
That filtering is important from a defensive perspective. Detection teams should not look only for an executable downloaded from a suspicious domain. They should also examine unusual Graph API access, SharePoint list enumeration, uploads of source-map-like files, and repeated requests whose names contain host-specific random identifiers.
Modular execution and operator capabilities
The plug-ins use a compact loader followed by a COFF object. Securelist reports that the loader locates a marker in its own binary, allocates executable memory, performs relocations and invokes an entry point named go. Other components use reflective loading to place compiled Go programs into the current process. This reduces the need to create conventional plug-in files on disk.
The keylogging component stores captured keyboard and mouse activity in %APPDATA%\Microsoft\SystemCertificates\Cache\logs.dat. It generates a per-log random XOR key, masks that key with a hard-coded key, and writes the resulting material alongside the captured data. The plug-in installs low-level keyboard and mouse hooks and records window text, timestamps, virtual-key information and mouse events. Securelist also observed a named synchronization object that can be used to stop logging.
The process-listing plug-in acquires SeDebugPrivilege and enumerates active processes. Its records include process and parent-process identifiers, executable name, architecture, session identifier and domain-account information. The results are sent to GraphDoor through the existing named pipe.
The screenshot plug-in searches visible top-level windows and compares their owning process identifiers with a supplied value. It captures the matching window, encodes the image as JPEG and Base64-encodes the result before sending it through the pipe. When the supplied identifier is zero, Securelist says the component captures the full desktop.
A separate move-directory plug-in supports relocation of the legitimate executable, loader DLLs and encrypted backdoor file. It can launch the copied executable from a new path, coordinate termination of an older instance through a global event and, under specified conditions, remove files associated with the previous instance. These behaviors are relevant to both persistence investigations and post-compromise scoping, although the supplied research does not establish a single universal persistence mechanism for every deployment.
Proxying through Erfrp and Ably
GraphDoor’s networking extensions are particularly significant. Securelist identified a proxy plug-in derived from the open-source Erfrp project. Instead of reading a normal configuration file, the modified client reads configuration from a per-process shared-memory segment and can start a reverse-proxy session. The plug-in is reflectively loaded from a compiled Go binary.
Two other components use Ably. One connects to Ably’s real-time messaging service with a token and channel name supplied through shared memory. It subscribes to message events, opens a TCP connection when instructed, relays data and publishes responses back to the channel. The other implements a SOCKS5 proxy over an Ably Pusher-compatible WebSocket service. It creates request and response channels derived from an instance identifier, then handles connection, data and close messages for individual TCP sessions.
These components make cloud messaging part of the operational layer, not merely a place to store files. Security teams that permit Ably or similar services should therefore consider whether endpoint processes are expected to create persistent WebSocket sessions, use unusual client identifiers or access messaging channels from servers that normally have no such requirement.
Attribution and infrastructure: what remains uncertain
Securelist does not definitively attribute Operation ShadowCloud to a named threat group. The organization reports overlaps with activity associated with Chinese-speaking groups, including FamousSparrow and CopperTurtle, and observed shared staging directories and deployment timing on some systems. Securelist explicitly treats these observations as suggestive rather than conclusive.
The report also describes related samples and infrastructure, including domains that were used as Cobalt Strike beacon command servers. The listed indicators include ms[.]twnic[.]top, ekmt[.]tw, SharePoint sites buildersemp[.]sharepoint[.]com and cskautogo[.]sharepoint[.]com, the GraphDoor MD5 14ec33ea808e697870d00c5e434c2952, and multiple proxy IP addresses. These indicators should be validated against the full Securelist report before operational use, because cloud tenants, proxy endpoints and associated infrastructure may change.
The report says GraphDoor does not embed a hard-coded command-and-control domain. Instead, it can obtain a host and port through the proxy plug-in or an Ably channel. Securelist also notes that the initial delivery of the MeshCentral Agent was not clear at the time of publication. Consequently, the supplied research supports a detailed description of post-compromise behavior, but not a complete, confirmed initial-access sequence.
What organizations should do now
- Review Microsoft Graph and SharePoint telemetry. Look for unusual application authentication, client-credential use, unexpected access to SharePoint lists, file creation through Graph, and uploads with source-map-like names or random host identifiers.
- Correlate endpoint and cloud events. A Windows process that creates a PID-derived named pipe, accesses
C:\ProgramData\Intel_Log, performs unusual API-resolution behavior and immediately communicates with Microsoft Graph warrants investigation. - Monitor for suspicious plug-in behavior. Hunt for low-level keyboard and mouse hooks, access to the reported log-file path, acquisition of
SeDebugPrivilege, broad process enumeration, JPEG screenshots and reflective loading of COFF or Go components. - Examine shared-memory and WebSocket activity. Unexpected use of named shared-memory segments, long-lived connections to Ably, SOCKS5-like traffic and TCP relay behavior can help identify the proxy modules even when cloud destinations are permitted.
- Restrict application identities. Audit application registrations, client secrets, Graph permissions and SharePoint access. Remove unused identities, reduce permissions and alert on new or anomalous application authentication.
- Control legitimate remote-management tools. Securelist specifically notes uncertainty around the introduction of MeshCentral Agent. Record approved deployments, enforce software allowlisting where practical and investigate unplanned installations.
- Use the indicators carefully. Add the published hash, defanged domains and IP addresses to appropriate hunting and blocking workflows, while preserving cloud-service telemetry and endpoint evidence for behavioral detection.
Conclusion
Operation ShadowCloud demonstrates how a modular implant can make Microsoft 365 and real-time messaging services part of its control plane. GraphDoor combines host discovery, encrypted cloud exchange, on-demand plug-ins, process and screen collection, keylogging and proxy functionality. The most durable defensive response is layered: monitor identity and Graph activity, inspect endpoint behavior, investigate unusual cloud-to-process relationships and treat unexpected remote-management software as a security event. Attribution remains unresolved, but the technical behaviors described by Securelist provide concrete opportunities for detection and containment.
Sources
Securelist: Operation ShadowCloud — GraphDoor backdoor, plug-ins and attribution