
Operation FlashHole: Lazarus Abuses South Korean Security Software
Kaspersky details Operation FlashHole, a Lazarus campaign combining watering-hole lures, CrossWeb EX abuse, memory-only execution, and modular Windows malware.
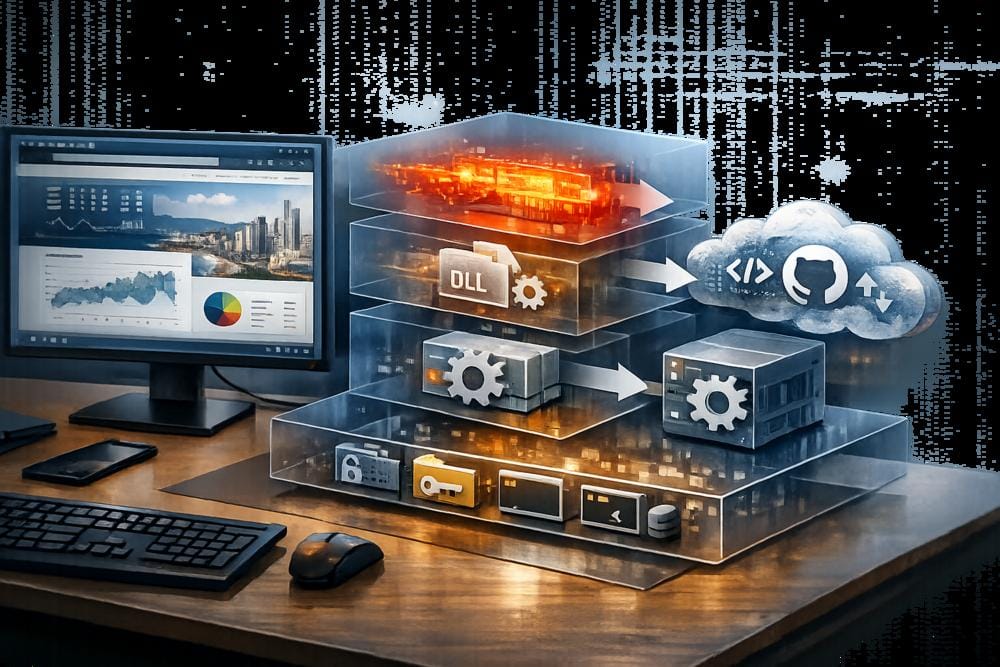
Operation FlashHole illustrates a recurring security problem in highly integrated enterprise environments: software installed to protect access to financial and government services can become an attractive delivery point when attackers find a way to abuse its trusted execution context. In its analysis, Kaspersky Securelist describes a Lazarus campaign targeting organizations in South Korea with a layered Windows malware framework, selective phishing lures, and a mixture of memory-only and persistent components.
The campaign is notable less for a single novel payload than for the way its parts are coordinated. TechHub initiates the chain, TouchHub and TouchShift establish persistence, ClientHub and LPEClient support later-stage delivery, and Cubridge acts as a modular orchestration layer. The result is an intrusion designed to minimize disk artifacts, blend command traffic with legitimate web activity, and retain flexibility after the initial compromise.
What Kaspersky confirmed—and what remains an assessment
Kaspersky identified at least three affected organizations in South Korea, spanning the software, construction, and wired communication equipment manufacturing sectors. The researchers also assess that the true number of affected organizations and industries is likely higher. That broader impact is not confirmed in the published findings.
The earliest evidence examined by Kaspersky dates to July 2025. The researchers assess with medium-to-high confidence that the activity was conducted by the same actor responsible for Operation SyncHole and attribute the broader operation to Lazarus. Their assessment is based on the initial-access pattern, targeted sectors, malware lineage, and operational similarities, including the use of LPEClient. The connection should therefore be treated as a research judgment rather than a directly observed identity statement.
Kaspersky also assesses with medium-to-high confidence that ClientHub is an advanced version of the malware known as CookiePlus. The report links several components to toolsets associated historically with Lazarus activity, including the Dream Job campaign. These relationships are useful for threat intelligence and hunting, but organizations should distinguish the reported overlaps from independently verified attribution.
Initial access: selective lures and a trusted software path
The campaign used websites hosted on GitHub Pages that were tailored to prospective victims. Kaspersky found a résumé-themed site apparently aimed at an employee of a wired communication equipment manufacturer and a separate interior-design site associated with a construction-sector target. The researchers assess with medium-to-high confidence that spear-phishing emails directed victims to these pages.
The sites embedded external JavaScript links. Defanged examples identified by Kaspersky include hxxps://javadevhouse[.]co[.]kr/ajax/libs/jquery/1.7.3/jquery.min.js and hxxps://pythonapischool[.]com/api/detach. The report says the exact event that triggered the infection chain could not be determined precisely, although visiting the tailored site likely initiated a process involving CrossWeb EX.
CrossWeb EX is a South Korean financial security product required by widely used online banking and government websites. Kaspersky states that the campaign abused CrossWeb EX rather than Cross EX, which had been involved in the earlier Operation SyncHole. Both products appear to be maintained by the same vendor. The precise abuse mechanism remains unclear, but the observed chain ultimately executed malicious code in memory. Kaspersky also observed the relevant spawned process operating with high integrity and identified INISAFECrossWebEXSvc.exe as the parent process associated with the CrossWeb EX installation.
This distinction matters operationally. The report does not establish a conventional software update compromise, nor does it provide a confirmed vulnerability identifier for CrossWeb EX. Instead, it documents abuse of software that is widely installed, runs in the background, interacts with browsers, and may operate with elevated trust. Administrators should avoid assuming that signed or familiar parent processes are inherently benign.
The infection chain moves from memory to persistence
During initial compromise, the legitimate Windows binary fsquirt.exe was executed under the CrossWeb EX process and injected with shellcode containing the TechHub malware. Kaspersky emphasizes that the initial execution chain existed only in memory. This design reduces the number of files available for conventional antivirus scanning and complicates retrospective investigation.
TechHub is a downloader and host-profiling component. Kaspersky identified three forms in the chain: an in-memory version, a DLL side-loading version, and a DLL side-loading version that uses a registered Windows service. TechHub communicates with a private GitHub repository through the GitHub API, using either hard-coded credentials or credentials held in configuration data. It creates a host identifier, performs a handshake, exchanges encrypted files, gathers information about the device and running processes, and then waits for commands.
The GitHub repository functions as a cloud-based command channel rather than an obviously dedicated control server. TechHub uses GitHub issues and repository files for communication, with encrypted content exchanged through names incorporating host identifiers and random values. Kaspersky observed commands for host discovery, in-memory shellcode execution, process termination, and beaconing after the handshake.
After the initial stage, the attackers installed TouchHub and TouchShift. TouchHub copies a legitimate executable to a new location, places a malicious mscoree.dll beside it, writes configuration data, and registers a service. The service is given a name derived from a legitimate service name with two additional random letters and uses a command line ending in -TimeBroker. TouchShift is then loaded through DLL side-loading and decrypts a further TechHub payload.
Observed persistence-related paths included C:\Windows\System32\RasConv\ImeBroker.exe, C:\Windows\System32\RasConv\mscoree.dll, and C:\Windows\System32\RasConv\ActivationStore.dat. Kaspersky also found related paths under C:\ProgramData, including C:\ProgramData\RasConv\mscoree.dll, C:\ProgramData\Apple\mscoree.dll, and C:\ProgramData\Dell\mscoree.dll.
TouchHub additionally synchronized file timestamps with a legitimate system file. That behavior is intended to complicate timeline analysis and is a useful behavioral signal for defenders: a newly created service, a side-loaded DLL, an unusual system-directory subfolder, and suspicious timestamp manipulation should be investigated together rather than in isolation.
ClientHub, LPEClient, and Cubridge divide the work
Once persistence was established, the chain deployed ClientHub and LPEClient before redeploying Cubridge. Kaspersky suspects this sequencing was deliberate because Cubridge is the most capable orchestration layer and was better protected by the earlier stages.
ClientHub supports multiple communication models. One version uses HTTP(S), while another communicates through the Dropbox API. Its configuration can be stored internally or in C:\Program Files\Common Files\System\msadc\msadc.inc. The malware uses the SNOW 1.0 stream cipher and constructs a communication key from both random bytes and host data. Requests include browser-oriented headers such as Sec-CH-UA, Sec-CH-UA-Platform, and Sec-Fetch-Mode, allowing traffic to resemble Chromium activity.
LPEClient provides profiling and payload delivery support. Kaspersky observed it preparing cryptographic material, relaying communication through ClientHub, and receiving payloads that were ultimately reflectively loaded in memory. The researchers identified the final payload in the examined sequence as Cubridge. They also observed LPEClient attempting to disable a user-mode syscall instrumentation hook before loading the acquired payload, an example of defense evasion that may be difficult to see through ordinary file scanning.
Cubridge functions as the framework’s central controller. It can load plugins, tools, and modules using reflective loading, DLL injection, and section-mapping injection. Its reported functions include collecting host and process information, creating and reading files, executing commands, managing processes, inspecting disks and network configuration, capturing displays, querying Active Directory through an ADFinder plugin, and extracting browser data through a browser-stealing tool. Kaspersky also identified functionality for scheduled execution, file cleanup, firewall and network command emulation, and loading additional modules.
The report describes Cubridge traffic that imitates browser requests and uses dynamically constructed URL paths. One defanged infrastructure example is hxxps://cubedesign[.]co[.]kr/news. Other reported domains and paths include hxxps://cubedesign[.]co[.]kr/mobile/fashion, hxxps://fp-news[.]co[.]kr/shop/cart, hxxps://k-wbc[.]co[.]kr/skin/social/social_view.php, hxxps://rcsh[.]co[.]kr/modules/bbs/tiles/bbs_div/inputForm.php, and hxxps://www[.]ksog[.]org/insert_file/handle.php. These should be treated as hunting indicators from the report, not as a complete list of campaign infrastructure.
Why the chain is difficult to investigate
FlashHole combines several visibility challenges. The first-stage payload is memory-resident, later components use legitimate binaries for side-loading, persistence is created through a service, and control traffic is distributed across GitHub, compromised websites, and in one observed ClientHub sample, Dropbox. Encryption and browser-like headers further reduce the value of simple network signatures.
The modular structure also allows the operator to change capabilities without replacing the entire framework. Plugins and tools can be delivered when needed, while modules remain available for extended activity. This segmentation means that finding one component does not necessarily prove the intrusion has been contained.
What organizations should do now
- Inventory CrossWeb EX and related security software. Confirm versions, deployment scope, parent-child process relationships, service registrations, and whether the software is required for business operations. Do not assume that a security product is outside the threat model.
- Monitor for abnormal process ancestry. Investigate CrossWeb EX spawning or injecting into
fsquirt.exe, unexpected high-integrity descendants, and legitimate Windows binaries loading DLLs from newly created or unusual directories. - Hunt for persistence artifacts. Review newly registered services, especially services with names resembling legitimate
netsvcsentries, command lines containing-TimeBroker, and side-by-side files namedmscoree.dll. - Inspect memory, not only disk. Use endpoint telemetry capable of identifying reflective loading, suspicious executable memory, section-mapping injection, anomalous thread creation, and code execution from processes that normally do not host those behaviors.
- Audit outbound access. Review GitHub API activity, GitHub Pages visits, Dropbox API use, and traffic to the defanged domains listed in the Kaspersky report. Browser-like headers should not be treated as proof of legitimate browsing.
- Review browser and identity exposure. Because the reported toolkit includes browser-data collection and Active Directory querying, rotate potentially exposed credentials and tokens after scoping the incident, and examine unusual directory-query activity.
- Use the supplied indicators carefully. Kaspersky lists TouchShift hashes including
ec84d6cb2ae7974767aedac246b50a3eand ClientHub Loader hashff07641dc56914dd90ee0bd7404d7ad7. It also reports detections such asMEM:Trojan.Win64.Shellcode.gen,Trojan.Win64.DLLhijack.*, andTrojan.Win64.Lazarus.*. Validate these indicators against local telemetry and retain surrounding process and network context.
Conclusion
Operation FlashHole shows how Lazarus can combine targeted social engineering with trusted local software, memory-only execution, service-based persistence, and a modular post-compromise framework. Kaspersky’s findings support a focused defensive response: monitor trusted software for abnormal behavior, make memory and service telemetry central to investigations, and treat cloud platforms and browser-like traffic as potential parts of the control channel. The campaign’s full reach remains unknown, but its documented design is sufficient to justify proactive hunting across South Korean-linked environments and organizations using comparable software ecosystems.
Sources
Kaspersky Securelist: Dissecting Operation FlashHole, a complex attack by Lazarus