
eMudhra CA Key Compromise: PKI Risk and Response
The compromise of eight eMudhra intermediate CA private keys creates a certificate-trust emergency. Here is how organizations should assess exposure and respond.
A compromise of eight intermediate certificate authority (CA) private keys belonging to Indian certificate authority eMudhra Limited has created a broad trust-management problem for organizations that rely on certificates issued through those intermediates.
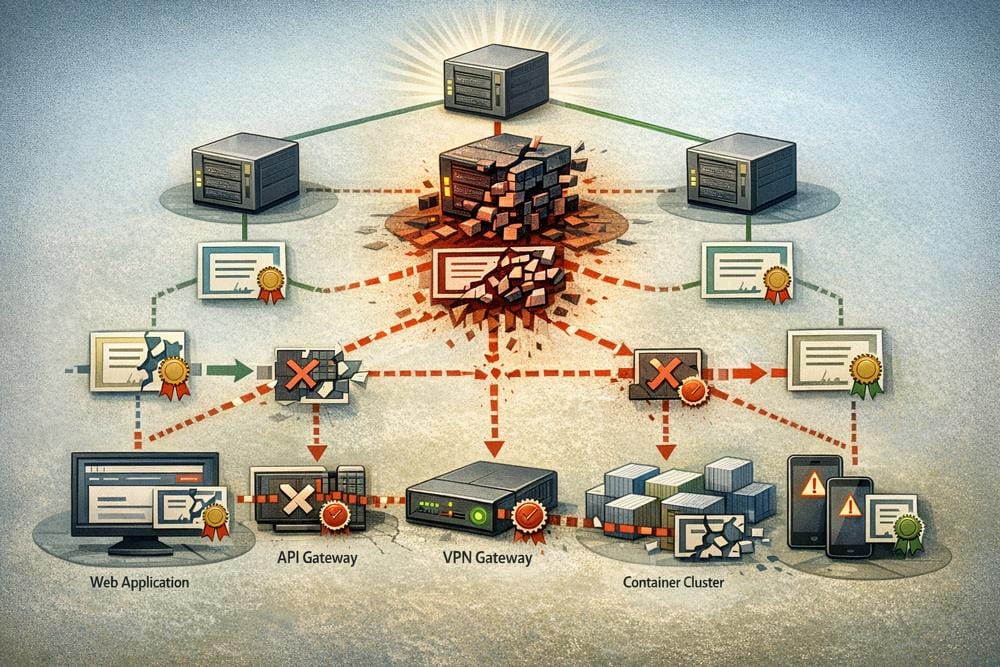
According to Palo Alto Unit 42, the private keys were generated with insufficient randomness during certificate creation. That cryptographic defect may allow an attacker to derive the private keys from the corresponding public certificates. Because an intermediate CA can authorize the issuance of end-entity certificates, possession of these keys could enable certificates that appear to chain to a trusted authority.
The practical concern is not limited to replacing a few website certificates. A compromised intermediate CA can affect the assumptions that browsers, operating systems, enterprise appliances, applications and custom trust stores make about certificate authenticity. Organizations therefore need to treat the incident as a PKI exposure assessment and trust-store containment exercise, rather than as a routine certificate renewal.
What Palo Alto Unit 42 confirmed
Unit 42 reports that eight eMudhra intermediate CA private keys were compromised because of inadequate randomness in the key-generation process. The organization says the weakness could allow third parties to derive the private keys from public certificates and use them to sign unauthorized public TLS certificates.
Unit 42 also reports that eMudhra revoked the eight affected certificates and that major browser and operating-system vendors have moved to revoke or distrust the affected intermediate CAs. Those actions reduce the usefulness of certificates issued through the compromised chain, but they do not by themselves answer every organizational question. Enterprises may still have certificates deployed internally, hard-coded trust anchors in applications, or systems that do not receive trust-store updates promptly.
The supplied research does not identify a confirmed attacker, a named victim, a specific fraudulent certificate, or confirmed traffic interception. It describes the interception, impersonation and session-hijacking consequences as potential abuse scenarios enabled by the compromised keys. That distinction matters: the key compromise is the reported finding; active exploitation against a particular organization remains unconfirmed in the supplied material.
Why an intermediate CA compromise matters
Public-key infrastructure separates trust and operational use across several certificate layers. A root CA normally anchors trust, while an intermediate CA issues certificates beneath that root. Organizations and software generally do not need to trust every individual website certificate separately; they trust the chain that validates it.
If an intermediate CA private key is exposed, an unauthorized party may be able to create certificates for domains or services that the intermediate is permitted to cover. A certificate generated in this way could appear valid to a client that still trusts the affected chain, at least until revocation and trust updates take effect and provided other certificate constraints do not block validation.
Unit 42 identifies several possible consequences: unauthorized TLS certificate issuance, man-in-the-middle interception, service impersonation and session hijacking. These outcomes depend on additional conditions, including the target environment's certificate validation behavior, network position and ability to influence a connection. The report does not state that any of these activities occurred in a confirmed victim environment.
The risk is particularly difficult to assess when certificate trust is distributed across many places. Public websites and APIs are obvious targets for inventory, but certificates and trust anchors can also be embedded in VPN gateways, internal services, containers, Java keystores, application bundles, mobile software, Python certificate bundles and Linux certificate directories. Build pipelines and deployment scripts may also preserve outdated intermediate certificates long after a central certificate-management system has been updated.
How a defensive assessment should proceed
The first step is discovery. Organizations should inventory public-facing services, APIs, web applications, VPN gateways and internal infrastructure, then identify certificates whose chains include an affected eMudhra intermediate CA. This work should cover systems managed by central IT as well as business-unit applications, cloud services and environments operated by managed service providers.
Teams should separately inspect repositories, container images, deployment scripts and application packages for bundled eMudhra certificates or hard-coded trust anchors. A centrally managed endpoint may receive a current operating-system trust store while an application continues to use its own embedded bundle. The two systems can therefore make different trust decisions.
Custom enterprise trust stores require the same attention. Unit 42 specifically calls out Linux certificate locations, Java keystores, Python certificate bundles, Docker base images and mobile application bundles as places where affected roots or intermediates may be retained. The objective is not only to find a currently deployed server certificate, but also to locate any component that could continue accepting a compromised chain.
Containment and certificate replacement
Where a service uses a certificate issued under an affected eMudhra intermediate, Unit 42 recommends immediate revocation and reissuance through an alternative, fully trusted CA. Replacement should be coordinated with service owners, load-balancer administrators, API teams, application developers and certificate-management personnel so that all active termination points are covered.
Organizations should also deploy updated trust stores across endpoints, servers, containers and mobile devices. The report recommends using mobile device management for emergency distribution to managed devices and explicitly distrusting or removing affected eMudhra intermediates where appropriate. Systems that are offline, unmanaged or maintained by third parties should be handled as separate workstreams rather than assumed to be updated automatically.
Revocation checking should be enforced by web proxies, API gateways, outbound egress controls and security appliances wherever operationally feasible. Unit 42 recommends strict checking of certificate revocation lists and Online Certificate Status Protocol responses, with connections presenting revoked chains blocked. Administrators should validate how each platform behaves when revocation services are unavailable; a policy that silently falls back to acceptance may not provide the intended containment.
Looking for evidence of abuse
The available research does not provide indicators of compromise, malicious domains, IP addresses or confirmed fraudulent certificates. Detection should therefore begin with organization-specific certificate and identity telemetry rather than a fixed IOC list.
Network, proxy and DNS logs can be reviewed for unusual connections to external services presenting eMudhra-signed certificates, especially where the destination, certificate subject or issuer does not match the expected service. TLS telemetry should be examined for unusual increases in handshake failures, certificate-validation errors or untrusted-issuer warnings. Such events are not proof of interception; they may also result from incomplete trust-store changes or ordinary service misconfiguration. Their timing and relationship to affected assets are important.
Identity logs deserve special attention. Unit 42 recommends reviewing authentication activity for sensitive services such as single sign-on systems, VPNs and cloud portals around the period relevant to the compromise. Investigators should look for anomalous access, unexpected session behavior or authentication events inconsistent with known users and devices. The report frames this as a way to assess whether valid sessions might have been intercepted or replayed through rogue certificates; it does not report that session theft occurred.
Certificate Transparency monitoring provides a longer-term way to identify publicly logged certificates issued for an organization's domains. Security teams should monitor CT logs for unexpected certificates and establish an escalation process for investigating them. CT monitoring will not reveal every internal certificate or every trust-store problem, but it can expose unauthorized public issuance for registered domains.
What organizations should do now
- Identify exposure: Inventory public, private and third-party TLS certificates and determine whether any chain to an affected eMudhra intermediate CA.
- Replace affected certificates: Revoke and reissue impacted certificates through an alternative trusted CA, then verify deployment at every termination point.
- Update trust stores: Push current trust-store changes to endpoints, servers, container images, mobile devices, applications and custom runtime environments.
- Check software supply chains: Search repositories, build pipelines, deployment scripts and packaged applications for embedded eMudhra certificates or trust anchors.
- Enforce validation: Configure proxies, gateways and security appliances to perform CRL and OCSP checks and to reject revoked chains.
- Review telemetry: Investigate certificate errors, TLS handshake anomalies, proxy records, DNS activity and authentication logs for affected services.
- Monitor certificate issuance: Use Certificate Transparency monitoring for organizational domains and investigate certificates that do not match approved issuance activity.
- Reduce future exposure: Publish or review DNS CAA records, harden automated certificate lifecycle management and consider shorter-lived certificates where operationally suitable.
CAA records can restrict which certificate authorities are authorized to issue for an organization's domains, although they should be treated as one control within a broader PKI program. Unit 42 also recommends strengthening automated certificate lifecycle management and using short-lived certificates to reduce the potential impact window of future CA-key incidents.
What remains unknown
The supplied research does not establish how the keys were accessed after the cryptographic defect made derivation possible, whether unauthorized certificates were issued, which organizations may have been targeted, or whether traffic was actually intercepted. It also does not provide a CVE identifier, malware name, threat-actor attribution or MITRE ATT&CK mapping.
Those gaps should not be interpreted as evidence that no exposure occurred. They define the limits of the current reporting and reinforce the need for asset-specific investigation. Organizations should preserve relevant certificate, proxy, TLS and identity logs while performing the review, particularly if they identify affected certificates or unexplained validation events.
Conclusion
The eMudhra incident demonstrates how a weakness in certificate generation can extend beyond one CA's infrastructure and affect trust decisions across browsers, operating systems, enterprise platforms and applications. The immediate priorities are straightforward but operationally broad: find affected chains, replace certificates, update trust stores, enforce revocation and examine telemetry for signs of misuse. Longer term, comprehensive certificate inventory, CT monitoring, CAA controls and automated lifecycle management can make future trust emergencies faster to contain.
Sources
Technical findings and recommendations in this analysis are based on Palo Alto Unit 42's report on the compromise of eMudhra intermediate CA certificates.