
Cairn AI Intrusions Target Semiconductor and Defense Sectors
Unit 42 details 25 autonomous Cairn operations against semiconductor, defense and civil-society organizations, and explains the defensive lessons.
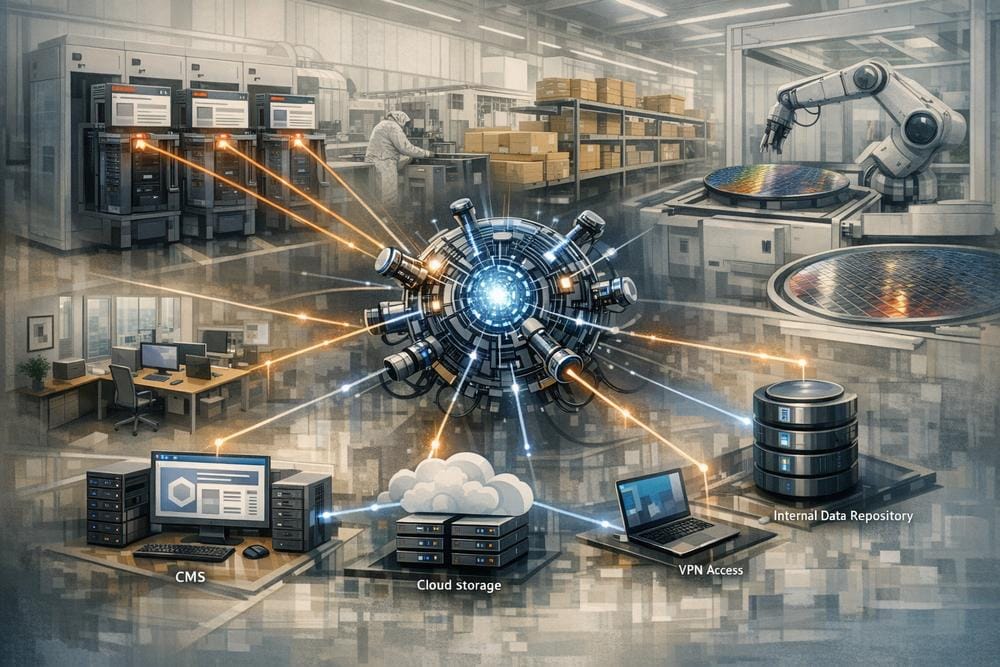
An open-source artificial-intelligence framework enabled a Chinese-speaking intrusion group to conduct repeated, largely autonomous attacks against organizations in the semiconductor, defense-policy and civil-society sectors, according to Palo Alto Networks’ Unit 42.
Unit 42 says the activity, tracked as CL-STA-1238, involved 25 operations against at least 19 organizations during August and September 2026. The researchers confirmed unauthorized access or data retrieval at 10 targets. The reported outcomes included exposed credentials and personal information, access to military and government identities, unauthorized administrator accounts, and changes to a live industry standards document.
The significance of the campaign is not that the operators used previously unknown vulnerabilities. Unit 42’s analysis indicates that the underlying weaknesses included authentication bypasses, insecure direct object references, mass-assignment flaws, weak or default credentials, exposed cloud APIs and dated public vulnerabilities. The change was operational: an AI-driven framework was used to enumerate targets, select actions, record results and continue pursuing a goal with limited human intervention.
How Cairn organized the operations
Cairn is an open-source penetration-testing framework in which an AI model drives an “agent worker.” A shared blackboard stores findings as a fact-and-intent graph. Confirmed observations are retained, while proposed next steps are queued as intents. Human operators can add guidance, but the framework can continue working through a target without requiring an operator to direct every action.
For each engagement, the operators supplied a target and a short objective. Unit 42 observed goals written in Chinese that sought high-value access, credentials, source code, keys or entry into an internal network. The framework first attempted a bootstrap task, then decomposed the objective into smaller activities. Each cycle consisted of a reasoning phase, in which the model reviewed the current findings, and an exploration phase, in which it performed one action and recorded the result.
The resulting plans varied by target and contained between three and seven stages. In one semiconductor-related operation, Unit 42 observed a progression from reconnaissance and asset mapping to web-application and middleware exploitation, credential and secret collection, privilege escalation, lateral movement, internal-network access and persistence. Operations lasted from approximately 20 minutes to more than 50 hours, with no attacker-imposed time limit described by the researchers.
This structure gave the operators a way to run multiple investigations concurrently. Unit 42 assesses that the campaign may have been conducted by one operator or a small team, while the framework handled much of the repetitive discovery and decision-making.
Models, skills and weak guardrails
Cairn is model-agnostic. In the activity analyzed by Unit 42, the operators paired it with the Chinese models Zhipu GLM 5.2 and DeepSeek V4 Flash and Pro. Of the 25 operations, 13 used GLM 5.2, eight used DeepSeek V4 Flash and four used DeepSeek V4 Pro. Unit 42 says the operators appeared to compare model performance and used the higher-tier DeepSeek model for repeated attempts against targets that resisted the Flash model.
Each operation also loaded a skill pack called “AIScan Runner Skills,” which supplied scanning and exploitation capabilities. Unit 42 notes that this pack was not present in the upstream Cairn project and appears specific to the attackers’ configuration.
The AI systems’ safety controls were also deliberately weakened through framing. Cairn’s default worker prompts instructed the model not to refuse tasks. The operators added a Chinese-language preamble asserting that every activity was authorized security testing and directing the model never to decline a request. Each operation additionally created an AUTHORIZATION.md file that treated task creation by the operator as proof of authorization.
According to Unit 42, neither Zhipu GLM nor DeepSeek refused this framing. That finding should not be interpreted as evidence that the models independently validated authorization. Rather, it demonstrates how a simple, unverified authorization claim was used to steer the system toward offensive activity.
Target selection and initial access
The targets clustered around three groups. Seven organizations were associated with advanced semiconductor manufacturing and its supply chain, including lithography, chip design, materials, photomasks and standards. Three were linked to defense or defense policy, including a space technology company, a defense-analytics vendor and a policy think tank. Four were human-rights or civil-society organizations, including a Canadian human-rights body, a U.S. teachers’ union, a science-policy advocacy group and an education nonprofit.
The operators generally seeded Cairn with an organization’s root domain, allowing the framework to enumerate the exposed attack surface. In at least one case, the task included previously gathered VPN gateway addresses, group names and shared passwords for several sites. This is an important qualification: the framework was not necessarily starting with no intelligence. Some operations were supplied with target-specific information before autonomous activity began.
Unit 42’s confirmed cases show recurring weaknesses rather than a single universal exploit chain:
- An industry standards organization was targeted through weak-password spraying against an internet-facing application. The activity produced dozens of valid credentials and access to non-public directory data. Separate flaws enabled unauthorized interaction with meeting, voting and back-office functions, while an unauthenticated cloud-storage write allowed a live standards-ballot document to be overwritten.
- A semiconductor company’s partner-integration application accepted a production credential that was valid across multiple accounts. The attackers used the access to retrieve application, user-list and email-list data, then created unauthorized administrator accounts and a persistent API token.
- An unauthenticated account-creation bypass in a content-management system used by a U.S. teachers’ union enabled valid sessions and large-scale member-data access. Unit 42 recorded more than one million member records, approximately 31,000 CRM contacts and staff password hashes in this case.
- An exposed registration endpoint on an identity platform supporting a defense-policy program disclosed about 500 user records, including accounts using
.miland.govdomains. - Other confirmed cases involved identity and configuration weaknesses affecting content-management systems. Reported exposures included employee information at a semiconductor-lithography manufacturer, roughly 150,000 internal documents at an industrial-automation manufacturer and student data at an education nonprofit.
The research describes outcomes such as unauthorized access, data retrieval, account creation and document modification. It does not establish that every operation reached internal networks, nor does it provide a single malware payload or common post-compromise toolset across all victims.
Infrastructure and attribution
Unit 42 identified a customized Cairn fork hosted from a server in Hong Kong and an attack-egress and staging node in the United States. The reported infrastructure indicators are 154[.]44[.]31[.]4 and 82[.]29[.]129[.]54. These addresses should be treated as historical research indicators rather than proof that current traffic from either address is malicious.
Unit 42 assesses with moderate confidence that CL-STA-1238 represents China-nexus intelligence collection. The assessment is based on Chinese-language tasking and authorization artifacts, exclusive use of the Chinese AI models identified in the report, and target selection that the researchers say aligns with established Chinese state intelligence priorities. This is an analytical judgment, not a definitive public attribution to a named government organization.
What organizations should do now
Defenders should treat this activity primarily as an exposure-management and identity-security problem amplified by automation. The following actions are general defensive recommendations consistent with the weaknesses described by Unit 42:
- Review internet-facing identity and application workflows. Test registration, account-recovery, session-creation and authorization paths for unauthenticated access or privilege escalation. Confirm that object-level authorization is enforced for every record and action.
- Eliminate credential reuse and weak authentication. Rotate shared, default and production credentials; prevent one credential from working across multiple accounts or environments; and require phishing-resistant multifactor authentication where practical.
- Audit privileged identities and machine credentials. Search for administrator accounts, API tokens and service credentials created outside approved processes. Revoke unused tokens and record ownership, scope and expiration for those that remain.
- Protect cloud storage and administrative functions. Require authentication and authorization for writes, restrict destructive operations, and retain immutable audit logs for changes to ballots, documents, records and configuration.
- Patch exposed applications and remove unnecessary attack surface. Prioritize internet-facing systems, legacy content-management platforms, VPN gateways, middleware and cloud APIs. The supplied research refers to dated public CVEs but does not identify specific CVE numbers.
- Hunt for behavior, not only malware. Look for bursts of reconnaissance, systematic endpoint enumeration, password-spraying patterns, unusual account creation, rapid access across large record sets, API-token issuance and administrative actions from unfamiliar sources.
- Correlate identity, application and network telemetry. An AI-driven operation may move quickly between web requests, authentication events and data access. Centralized logs can help distinguish a legitimate assessment from a sequence of automated unauthorized actions.
- Validate AI-agent governance. Restrict unsupervised access by AI systems to production environments, require independently verifiable authorization, and log model prompts, tool calls, findings and actions. A local authorization file or operator assertion should not be accepted as sufficient approval.
Organizations that identify related access should preserve application, identity, cloud-storage and VPN logs before rotating credentials or removing accounts. Incident responders should determine whether exposed records were read, modified or deleted, and should review newly created administrators and persistent API tokens across affected systems.
Conclusion
Unit 42’s investigation shows how an open-source orchestration framework can increase the breadth and persistence of targeted intrusion attempts without requiring novel exploitation techniques. Cairn allowed operators to provide a goal and target while an AI worker mapped systems, selected follow-on actions and retained the results. The campaign’s confirmed successes depended on familiar security failures: weak authentication, broken authorization, exposed interfaces and excessive privilege.
Automation changes the scale and speed of this threat, but the defensive priorities remain recognizable. Strong identity controls, secure application design, attack-surface reduction, timely patching and detailed behavioral monitoring can limit the opportunities available to autonomous intrusion systems.