
Agentic Offensive Frameworks Push Intrusions to Machine Speed
Google Threat Intelligence and Mandiant report that threat actors are using LLM-powered offensive frameworks to automate major stages of intrusions.
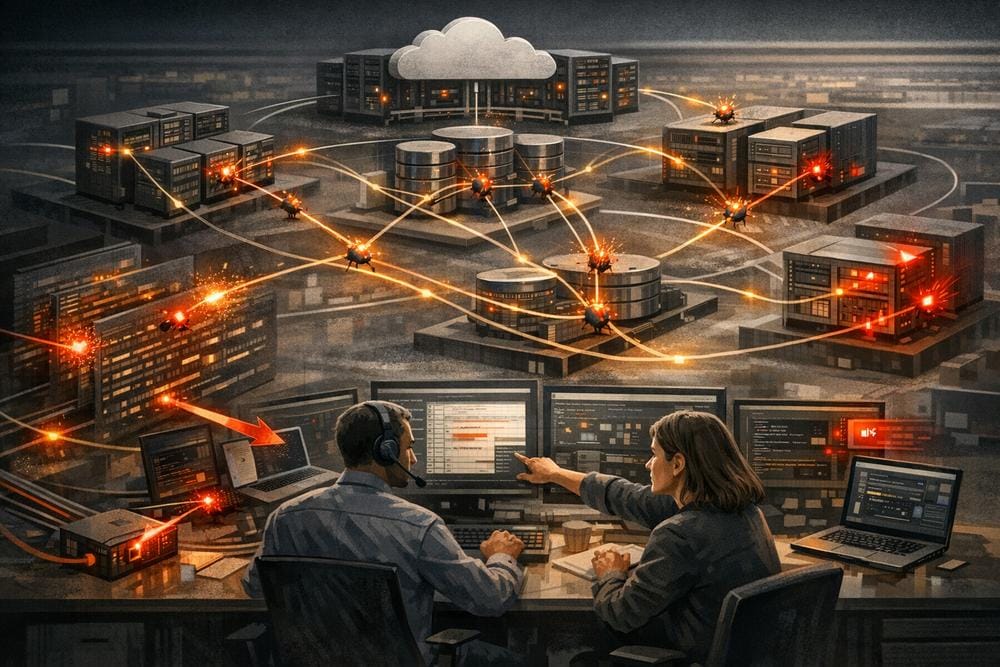
Threat actors are beginning to use large-language-model-powered offensive frameworks as operational systems rather than simple assistants for writing code or drafting phishing content. According to Google Threat Intelligence and Mandiant, incident-response investigations have identified in-the-wild use of ARTEX, PentAGI, CAIRN, Hexstrike and potentially customized agentic harnesses.
The significance is not that these frameworks introduce entirely new attack methods. The underlying actions remain familiar: abusing valid credentials, probing permissions, moving through poorly segmented environments, exploiting exposed application functionality and preparing data for collection. The change is operational. Agentic systems can select tools, execute commands, interpret errors, change direction and continue through multiple stages with substantially less human intervention.
What the research confirms
Google Threat Intelligence Group, working with Mandiant, reported observing these frameworks during incident-response engagements since late August 2026. The activity included reconnaissance, privilege escalation, lateral movement, database exploitation and preparation for exfiltration. The researchers also corroborated the observations with their broader telemetry.
ARTEX is described as a Go-based, multi-agent offensive command-and-control and penetration-testing platform with a Next.js web console. It coordinates specialized agents and uses model APIs to convert broad objectives into executable actions. The original public repository was removed by its creator in October 2026, but the framework continued to circulate through community forks, including variants identified by the researchers as ScopeWeaver and ARTEX PRO.
GTIG observed ARTEX performing activities such as Active Directory reconnaissance, privilege escalation attempts, cloud-infrastructure profiling and the harvesting of Azure storage credentials. It also generated and deployed custom webshells in one investigated environment. The framework was used by actors with different motivations, including financially motivated extortion groups and clusters that the researchers assess as suspected cyber-espionage operators.
PentAGI represents a related but distinct approach. The framework, developed by VXControl, is available in open-source and commercial forms and is designed to automate penetration-testing workflows inside isolated Kali Linux sandboxes. It can coordinate specialized agents, use common security tools and connect to more than a dozen local or cloud-based language-model backends. Much of the activity observed by GTIG remained focused on WHOIS mapping and vulnerability scanning, but operational artifacts indicated that some campaigns progressed into active intrusion and persistence. The researchers also identified customized deployments and use of proxy services.
How an agentic intrusion can unfold
The investigations show an attack sequence that begins with access already obtained or an exposed service that can be interrogated. In several ARTEX cases, operators supplied compromised credentials and instructed the framework to continue. From there, the system tested what the identity could do, discovered relationships between applications and infrastructure, and pursued whichever paths appeared viable.
In cloud environments, ARTEX rapidly tested the effective permissions of Azure credentials, including SAS tokens, service principals, Kudu credentials and storage-account keys. It also assessed AWS IAM capabilities using dry-run requests and placeholder resource identifiers. These checks were not necessarily exploit attempts in the conventional sense; they were automated attempts to map available authority and identify useful next steps.
The framework then moved into execution and persistence activity where permissions allowed. The research describes abuse of Kudu administrative APIs to run commands and stage Python, C# and PowerShell content. In one case, a compromised Windows database server used the native curl utility to retrieve dynamically generated scripts and send results to rotating webhook[.]site URLs.
Privilege escalation activity included Kerberoasting, database credential extraction, DCSync activity and attempts to create or use highly privileged accounts. The researchers also observed efforts to launch cloud instances with valuable IAM roles, create SSH keys, allocate public addresses and establish externally reachable jump hosts. Some attempts failed because of permission problems or invalid role identifiers, but the framework continued adapting to those errors.
Internal reconnaissance included enumeration of domain users, group-managed service accounts, certificate-service templates, cross-forest security principals, Exchange systems, credential vaults and possible server-side request forgery or source-control-management targets. Lateral-movement attempts included Pass-the-Ticket, WinRM, Kerberos relay and Pass-the-Hash activity. In one investigation, endpoint protection blocked execution and defenders cut off access before the attempted movement succeeded.
For mission activity, ARTEX queried backend databases, read large numbers of cloud objects, enumerated more than 110,000 Active Directory objects and retrieved the Domain Admins group. It also created storage capacity and launched ephemeral instances in preparation for automated collection. The research characterizes some of these actions as preparation for exfiltration rather than proof that all intended data was successfully removed.
Speed, noise and the limits of current tooling
One of the clearest behavioral differences from conventional operator activity was the timing. GTIG and Mandiant found execution bursts lasting roughly two to 25 seconds. In one example, 27 events occurred during 23 seconds of active execution while AWS permissions were probed across security groups.
The automation was fast, but it was not consistently quiet or elegant. The researchers observed iterative trial and error, repeated requests and errors that may have resulted from multiple agents pursuing the same objective. During one database-focused operation, approximately 240 log events were generated as the framework used application-specific SQL APIs and attempted to move from database execution toward system execution.
That operation also demonstrates why defenders should monitor legitimate functionality, not only unfamiliar binaries. ARTEX used a database logging feature and publicly accessible application paths in an apparent attempt to create JSP webshells. It generated several candidate filenames, including cl1217.jsp, f1219a.jsp and z1219.jsp, revising its approach when earlier attempts failed. The behavior was noisy, but the framework could use application errors as feedback and continue refining its actions.
Other artifacts included filenames beginning with artex-probe-, incremental numeric markers, and account or password naming patterns containing ArtexProbe. These are useful investigative clues where present, but they should not be treated as universal indicators. The source specifically notes that the meaning of the numeric patterns was uncertain.
Attribution and assessment
The research links one ARTEX-associated campaign tracked by GTIG as UNC7228 to activity that overlaps with the PRC-nexus actor designation STORM-0940 used by Microsoft. This is presented as an overlap and assessment, not as a definitive attribution for every ARTEX intrusion.
GTIG also observed ARTEX use by financially motivated actors and additional suspected PRC-nexus clusters across government, technology, chemicals and materials, and manufacturing organizations in the United States. Public reporting cited by the researchers described ARTEX targeting in the Asian financial sector. The source does not establish that every organization scanned or contacted by these frameworks was successfully compromised.
GTIG assesses that current use remains relatively unsophisticated, broad and forensically noisy, even when it succeeds. The organization expects more stealth and less human involvement as the underlying models, framework engineering and operator practices improve. It expresses high confidence that cybercrime actors will continue adopting these tools because increased scale may offset lower success rates. The researchers consider long-term stealth-focused operators less likely to use public versions routinely, though they may still use them when speed or scale is more important than concealment.
Detection implications
Static indicators remain useful when available, but they are insufficient for this activity. A valid service principal, a normal management API or a supported storage protocol can all be used inside an automated attack. Detection should therefore connect identity, control-plane, data-plane, endpoint and network events into behavioral sequences.
Security teams should look for unusual authentication origins, rapid permission testing, bursts of management API calls, sudden enumeration of storage or directory objects, and read-write-delete patterns that do not match the workload’s normal behavior. A previously unseen hosting provider or webhook service contacted by a production server deserves investigation, particularly when the connection follows credential use, administrative API activity or data enumeration.
Defenders should also examine exposed workloads for unexpected east-west traffic involving LDAP, Kerberos, NTLM, SMB, WinRM, databases or remote administration. Application logs may reveal repeated file probes, abnormal API calls, attempts to alter database-wide settings, or rapid creation and deletion of accounts, records and files. Burst timing and event sequence may be more revealing than any single command.
What organizations should do now
- Protect control planes: Restrict administrative consoles, cloud APIs and CI/CD systems to trusted networks and approved workloads. Do not assume that possession of a credential should permit access from arbitrary infrastructure.
- Reduce identity blast radius: Replace long-lived secrets with short-lived, narrowly scoped workload credentials. Limit service principals to the APIs, projects, subscriptions, repositories and storage resources they need, and constrain where they can authenticate.
- Assume workloads can be compromised: Segment internet-facing applications from identity systems, management infrastructure and unrelated internal services. Review whether application identities can reach databases, secrets, storage or administrative interfaces beyond their business purpose.
- Harden databases and applications: Prevent application accounts from changing server-wide settings, writing arbitrary files or crossing from database functionality into operating-system execution unless explicitly required. Add rate limits and approval controls to user creation, password resets, messaging and bulk-data functions.
- Improve telemetry: Centralize non-interactive identity logs, cloud control-plane events, storage access records, application administration logs, DNS, proxy, network-flow and endpoint data. Retain enough history to establish normal behavior for sensitive identities and workloads.
- Correlate behavior: Prioritize detections that connect a new authentication source with permission probing, resource enumeration, bulk access and unusual external communication. This is more resilient than relying only on filenames, hashes or IP addresses.
- Limit egress: Route sensitive workloads through controlled outbound paths and investigate unexpected contact with webhook services, tunneling platforms, public file-transfer services or external AI platforms.
Conclusion
Agentic offensive frameworks are changing the tempo of intrusion operations without fundamentally changing the weaknesses attackers exploit. ARTEX and PentAGI show how valid access, excessive permissions, exposed administrative functions and weak segmentation can be combined in minutes rather than hours. The immediate defensive priority is not to hunt for a single “AI attack” signature. It is to reduce the consequences of identity compromise, protect control planes and detect abnormal sequences across cloud, application, identity and network telemetry.
Sources
Technical findings and assessments in this analysis are based on “ARTEX and Friends: Enter Agentic Offensive Frameworks,” published by Google Threat Intelligence Group and Mandiant.