
Agentic AI Is Reshaping the Cyberattack Lifecycle
Google Threat Intelligence and Mandiant document how adversaries are using agentic AI to accelerate exploitation, cloud abuse, espionage, and influence operations.
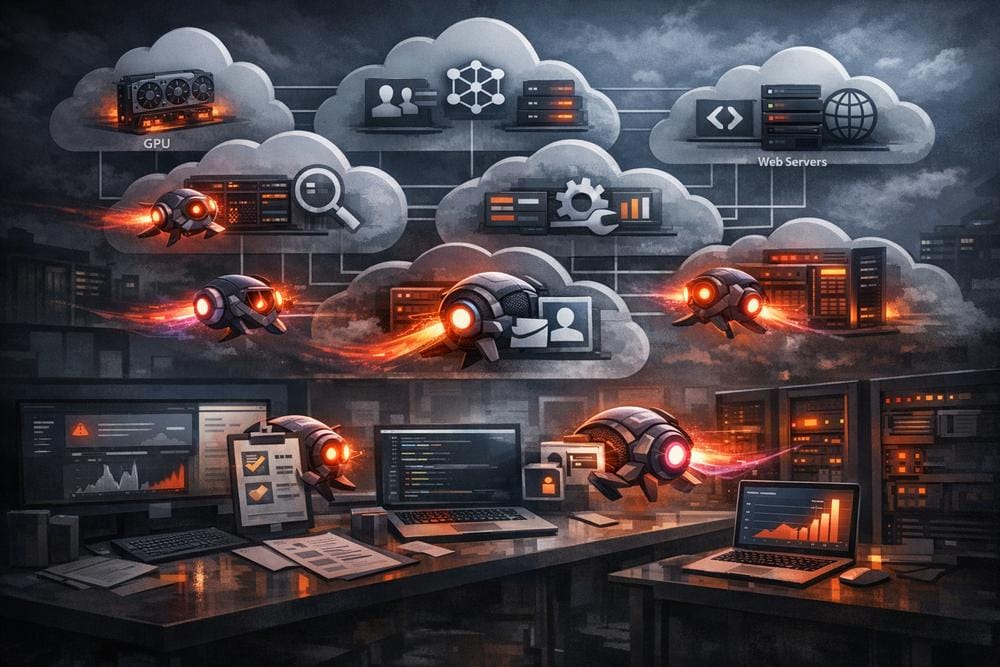
Generative AI is becoming more than an assistant for threat actors. According to Google Threat Intelligence Group (GTIG) and Mandiant, adversaries are beginning to connect language models to autonomous frameworks, security tools, cloud resources, and operational workflows. The result is not a wholly new class of attack, but a significant change in the speed, scale, and accessibility of familiar techniques.
In its latest assessment, GTIG describes activity spanning financially motivated cybercrime, suspected state-sponsored espionage, information operations, vulnerability exploitation, and unauthorized use of cloud-based AI services. The organization’s central finding is that threat actors are moving from occasional prompting toward multi-agent systems capable of reconnaissance, vulnerability analysis, payload generation, and adaptive follow-on activity.
These observations come with important qualifications. GTIG and Mandiant report that many current tools remain noisy, error-prone, and easier to detect than carefully managed human operations. The research does not establish that every observed campaign was fully autonomous, nor does it suggest that AI has eliminated the need for valid credentials, unpatched systems, or social engineering. Instead, the evidence points to an evolving operational model in which AI compresses parts of the attack lifecycle and lowers the expertise required to use them.
From isolated prompts to coordinated attack workflows
GTIG reports that threat actors have deployed or experimented with open-source agentic offensive frameworks including CAIRN, CyberStrikeAI, HexStrike AI, and PentAGI. The research also references ARTEX, custom-built orchestration platforms, ZeroHollow, and Agent Zero.
The frameworks differ in design, but the reported capabilities overlap. They can connect specialized agents to reconnaissance and security tools, generate single-use payloads, use execution feedback to change tactics, and automate portions of an intrusion. CAIRN, for example, uses an Observe, Orient, Decide, Act loop and a shared coordination mechanism for its agents. CyberStrikeAI provides an orchestration layer connecting language models with security tools, attack recipes, and scripts. HexStrike AI links language-model clients to a large collection of offensive utilities through a Model Context Protocol-integrated harness. PentAGI is described as an autonomous offensive framework intended to reduce the technical barrier to complex operations.
GTIG independently observed CAIRN and PentAGI deployed in real-world activity and saw experimentation with CyberStrikeAI and HexStrike AI. The organization observed CAIRN used against targets including an organization in the U.S. aerospace sector. It also tracked an actor using a customized platform based on PentAGI for systematic reconnaissance and vulnerability scanning across organizations in Asia between late August and early October 2026.
The practical significance is acceleration. The underlying actions—credential use, scanning, exploitation of known weaknesses, and post-compromise discovery—are familiar. Agentic orchestration allows those actions to be chained with less direct operator involvement and repeated across more targets. GTIG assesses that adoption is likely to continue because the tools are relatively accessible, can incorporate new exploits, and can scale activity rapidly.
Automated vulnerability research shortens the patch window
The research describes a second development: automated pipelines that move from patch analysis to exploit generation and execution. GTIG identified an exposed staging server hosting a framework called exploit_agent. According to the report, the system connected to multiple frontier and local language models, compared software versions before and after patches, analyzed potential vulnerabilities, drafted exploits, and executed them without a human in the loop.
Researchers also found scripts associated with internal reconnaissance, brute-force activity, webshell installation, and removal of other attackers’ webshells. Telemetry suggested that the operator was interested in French websites associated with media, entertainment, and education. These details describe the observed environment; they do not establish that every capability was successfully used against every intended target.
GTIG and Mandiant also discuss exploitation of PaperCut vulnerabilities CVE-2026-81578 and CVE-2026-82078. The report says the flaws were exploited as zero-days in a chain that enabled unauthenticated remote code execution, and that researchers generated working exploits within a day of disclosure. GreyNoise later reported a campaign occurring four days after disclosure that likely used AI to help build and test exploits, assemble targets, and conduct widespread exploitation. The source says the campaign affected hundreds of organizations and that one observed foothold expanded to domain administrator within minutes.
The report further cites CVE-2026-109618 and CVE-2026-109619, PHP vulnerabilities whose analysis benefited from LLM-enabled research. Before official patches were released on October 21, 2026, publicly available material and early patched code enabled comparisons that could help researchers and attackers understand the flaws. GTIG observed hundreds of claimed proof-of-concept examples after the patch, many of which were reportedly non-functional. This creates a dual problem: defenders must investigate rapidly while separating real exploitation from a growing volume of unreliable material.
For administrators, the lesson is straightforward: patch exposure remains a race, and the time between public disclosure and exploitation may be compressed by automated analysis. Security teams should prioritize internet-facing systems, validate patch status independently, and treat credible exploitation reports as urgent even when public proof-of-concept code is inconsistent.
LLMJacking turns cloud access into a revenue stream
Mandiant responded during 2026 to several incidents in which financially motivated actors compromised cloud environments to consume victims’ compute capacity or AI service quotas. The report calls this activity LLMJacking. In some investigations, fraudulent charges exceeded $100,000 in a single day; the most severe cases reached $1 million before remediation.
The observed lifecycle began with credential theft or session hijacking. Reported access paths included credentials exposed in public GitHub repositories and deceptive websites designed to capture active session tokens. After entry, attackers searched code repositories, data stores, cloud services, containers, and access logs for additional credentials and systems. In at least one case, Mandiant observed suspected exploitation of a web application vulnerability in an internal container to reach other systems.
For persistence and privilege, actors created unauthorized IAM or service accounts and attached administrative policies to service roles. The research also identifies CVE-2026-40217, described as a LiteLLM sandbox escape that can elevate limited inference keys, called Virtual Keys, into administrative credentials. Once privileged access was available, actors enabled AI services, subscribed compromised accounts to pay-as-you-go plans, provisioned GPU instances, and requested increased quotas. One actor used a “burn and rotate” approach involving short-lived service accounts to work around rate limits.
Some of the compromised resources were used to run agentic tooling, while others supported API gateways and relay infrastructure for resale. GTIG tracks underground “LLM Mixers” that package unauthorized access to AI services and compute. These services can distribute demand across multiple compromised environments, making one victim’s usage appear less conspicuous. The report cites advertised prices ranging from $0.10 to $25 per million tokens, although pricing varied by provider, model, and credential type.
AI is also entering espionage and software supply chains
GTIG reports that state-linked and suspected state-linked actors are using language models for reconnaissance, target research, exploit development, and analysis of exfiltrated information. The organization specifically describes PRC-nexus activity involving front-end scanning, research across sectors and geographies, exploit weaponization, and post-compromise data analysis. It also reports that a PRC contractor, LEAKY CASTLE, used LLMs to analyze, translate, and interpret stolen data for intelligence products.
The research identifies another concerning pattern: abuse of AI platforms and file-hosting backends for staging, dead-drop command and control, and data theft. In one example, a threat actor used a model provider’s file-hosting infrastructure to stage lure archives and exfiltrate stolen data, while using a backend API to remove documents from an intranet.
GTIG also describes a supply-chain technique attributed to the suspected MIDNIGHT NEPTUNE cluster. In intrusions targeting cryptocurrency organizations in North America and Europe, fraudulent recruiter identities directed victims to fake meeting services and “ClickFix” lures. After initial compromise, the actor modified .claude/settings.json files in internal code repositories so that starting Claude Code would automatically trigger a download of the SOMBERMEME backdoor. The report says the actor also generated GitHub personal access tokens named after Microsoft Copilot to disguise lateral movement.
These findings illustrate a broader risk: AI tooling can become an enterprise execution surface. Coding-assistant configuration files, agent hooks, plugin settings, and automation pipelines should be treated as security-sensitive code, not merely developer preferences.
Information operations are becoming more industrialized
GTIG assesses with high confidence that information-operation actors have moved from experimentation to routine operational use of LLMs. The activity spans state-sponsored groups, commercial Influence-as-a-Service providers, and inauthentic political monetization networks.
Reported uses include generating localized personas, producing synthetic media, adapting content for demographic audiences, managing distribution, and improving search-engine visibility. GTIG investigated a platform that used the Gemini API and other AI services to automate persona creation, multimodal media production, distribution, and interactive posting. The observed design sought to imitate grassroots engagement and evade platform defenses through localized language, simulated imperfections, residential proxies, and persistent session cookies.
A separate commercial platform was designed to manage more than 100,000 accounts using automated agents, device-identifier spoofing, cloud phones, disposable email addresses, virtual SMS numbers, and account-aging workflows. GTIG emphasizes that better content quality does not necessarily mean greater influence, but automation increases the volume and persistence of coordinated inauthentic behavior.
What organizations should do now
- Protect AI credentials as production secrets. Scan repositories, CI environments, endpoints, and logs for exposed API keys, session tokens, and service credentials. Rotate secrets promptly and use short-lived credentials with narrowly scoped permissions.
- Monitor cloud usage and identity changes. Alert on unexpected model subscriptions, sudden token consumption, unusual API volume, GPU provisioning, quota requests, new IAM or service accounts, administrative policy attachments, and rapid account creation or deletion.
- Prioritize internet-facing patching. Maintain an accurate inventory, verify remediation independently, and accelerate response to vulnerabilities affecting public services. Validate exploit claims rather than assuming every published proof of concept is functional.
- Harden developer automation. Review coding-assistant configuration files, repository changes, agent hooks, plugins, and startup scripts. Require code review and integrity monitoring for files that can trigger downloads or execution when developer tools launch.
- Hunt for machine-speed behavior. Correlate bursts of reconnaissance, repeated scanning, dynamic payload creation, unusual tool chaining, webshell activity, and high-volume API requests. GTIG notes that current autonomous frameworks can leave recognizable code-level traces and forensic traffic.
- Prepare for noisy but fast intrusions. Establish containment playbooks for compromised cloud identities, revoke sessions, disable unauthorized accounts, preserve relevant logs, and coordinate billing and provider-abuse investigations.
- Use layered controls. Combine least privilege, repository protection, workload isolation, egress monitoring, cloud spend alerts, endpoint telemetry, and behavioral detection. Do not rely on model safeguards or user awareness alone.
Conclusion
GTIG and Mandiant’s reporting shows that agentic AI is already affecting cyber operations, but not by replacing established intrusion methods. Its immediate contribution is compression: faster reconnaissance, quicker vulnerability weaponization, more scalable credential abuse, and cheaper access to sophisticated workflows.
Defenders should therefore focus less on identifying an “AI attack” as a separate category and more on detecting the operational consequences: abnormal identity behavior, accelerated scanning, unexpected AI consumption, unauthorized automation, and unreviewed changes to software-assistant workflows. The technology remains imperfect and often noisy, but its accessibility and scaling potential make early controls essential.