Ai Threat Intel Analysis How AI Agent Swarms Change the Cyberattack Playbook Cisco Talos examines how autonomous AI agents could compress attack campaigns from months to hours and outlines practical resilience measures.
Ai Threat Intel Analysis DPRK-Linked Supply-Chain Attacks Move C2 Into Web3 Palo Alto Unit 42 details how poisoned open-source packages and blockchain-based C2 expose cloud credentials through developer workflows.
Ai Threat Intel Analysis How Malware Is Learning to Manipulate AI Analysis Cisco Talos examines malware that embeds instructions for AI systems, showing why automated analysis pipelines must treat sample text as evidence.
Ai Threat Intel Analysis UAT-11985 Uses Event Lures for Real-Time Google Phishing Cisco Talos details a Taiwan-focused spear-phishing campaign using AI-assisted event invitations, malicious QR codes, and real-time Google AitM credential theft.
Ai Threat Intel Analysis Patch Priorities for Adobe, Apple, Foxit and Windows Cisco Talos details patched vulnerabilities across Photoshop, macOS, Foxit Reader and Windows, with practical guidance for prioritization and detection.
Ai Threat Intel Analysis Blinder Tunnel: GitHub C2 Targets Iraqi Infrastructure Unit 42 details a recruitment-themed campaign using malicious Visual Studio projects, AppDomainManager hijacking, DLL sideloading and GitHub-based C2.
Ai Threat Intel Analysis Cisco Talos on Making Cyber Defense Harder to Abuse Cisco Talos argues that behavior-based detection, controlled tools, deception, and bounded AI agents can reduce attacker flexibility.
Ai Threat Intel Analysis Executive Threat Detection: Hunting High-Value Assets Cisco Talos outlines an intelligence-led approach to hunting for subtle threats against executives and other high-value organizational assets.
Ai Threat Intel Analysis How Defenders Can Make Attack Chains Slower and Noisier Cisco Talos outlines practical ways to disrupt adversary workflows through deception, behavioral detection, tool governance, and attack-chain dependency management.
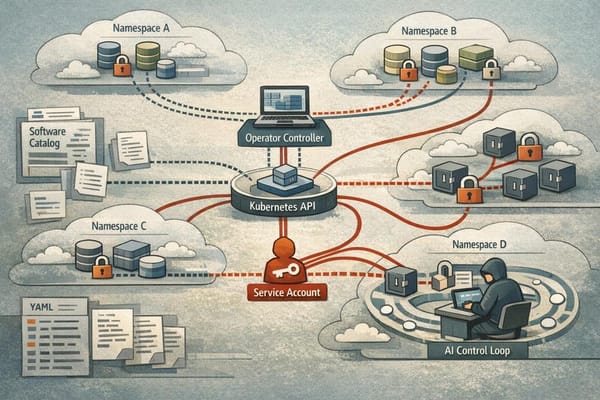
Ai Threat Intel Analysis Kubernetes Operators: The Hidden Risk of Excessive RBAC Palo Alto Unit 42 finds that overprivileged Kubernetes operators can turn trusted automation into high-impact non-human identities.
Ai Threat Intel Analysis AI Is Reshaping Vulnerability Discovery and Exploitation Google Threat Intelligence finds faster vulnerability disclosure and exploitation, with edge appliances and AI infrastructure emerging as priority risks.
Ai Threat Intel Analysis Antino Backdoor Targets Asian Government Organizations Cisco Talos details UAT-11587, a China-nexus campaign using the Antino backdoor, cloud-hosted delivery chains and Microsoft 365-based command and control.
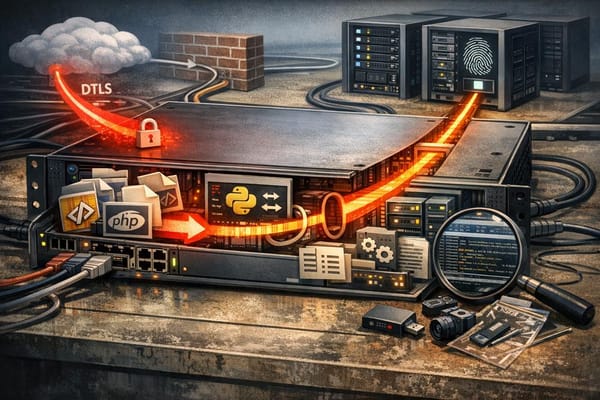
Ai Threat Intel Analysis Citrix NetScaler Campaign Uses Web Shells and Tunneling Google Threat Intelligence and Mandiant detail active NetScaler exploitation involving root access, disguised PHP web shells, and internal network tunneling.
Ai Threat Intel Analysis Why Security Fundamentals Matter More Than More Tools Unit 42 challenges three common security assumptions and outlines practical ways to improve tool use, privileged access governance, and enterprise resilience.
Ai Threat Intel Analysis NetScaler Zero-Days Put Internet-Facing Gateways at Risk Palo Alto Unit 42 examines in-the-wild exploitation reports involving two critical NetScaler vulnerabilities and outlines immediate defensive priorities.
Ai Threat Intel Analysis How CAIRN Tracks AI-Integrated Malware Cisco Talos’s CAIRN toolkit uses metadata, behavioral clues, and relationship graphs to help defenders study malware that incorporates AI services or models.
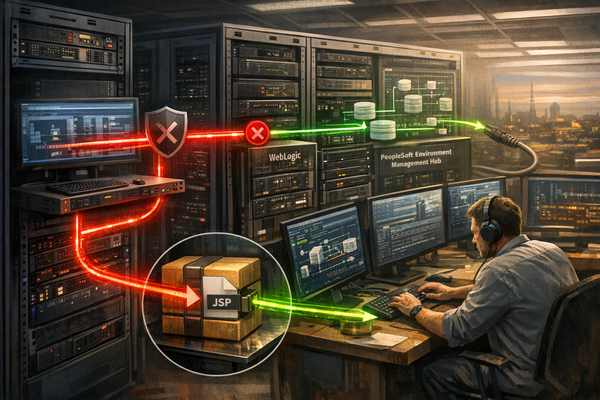
Ai Threat Intel Analysis UNC6240 Bypasses PeopleSoft WAF Rules to Deploy Web Shells Google Threat Intelligence and Mandiant detail UNC6240’s renewed exploitation of Oracle PeopleSoft, including WAF bypasses, web shells, and follow-on access.
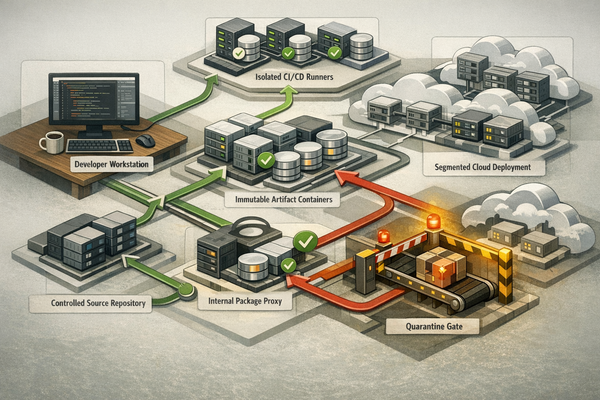
Ai Threat Intel Analysis Hardening CI/CD Against Modern Supply-Chain Attacks A practical analysis of how attackers target developer endpoints, repositories, dependencies, CI/CD runners, cloud identities, and software releases.
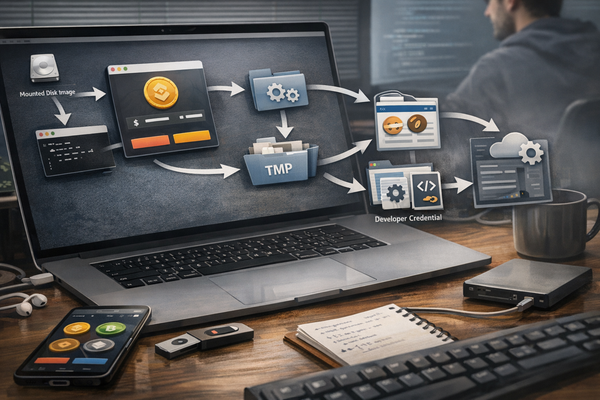
Ai Threat Intel Analysis MacSync on macOS: Stealer Gains a Persistent Backdoor Securelist details a redesigned MacSync campaign that targets macOS developers and cryptocurrency users with binary loaders, data theft, and a backdoor.
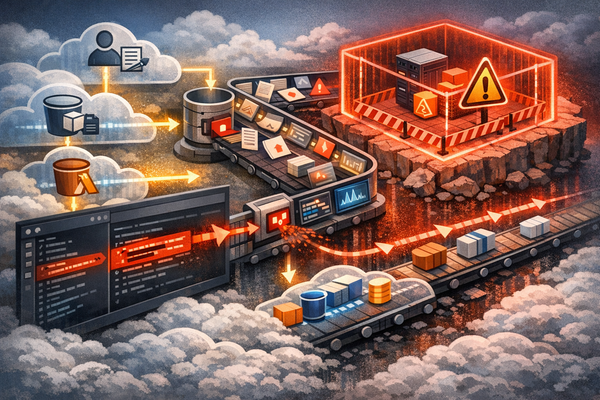
Ai Threat Intel Analysis How AWS Quarantines Exposed IAM Credentials Palo Alto Unit 42 explains how GitHub secret scanning, AWS quarantine policies and CloudTrail can help contain exposed IAM credentials.
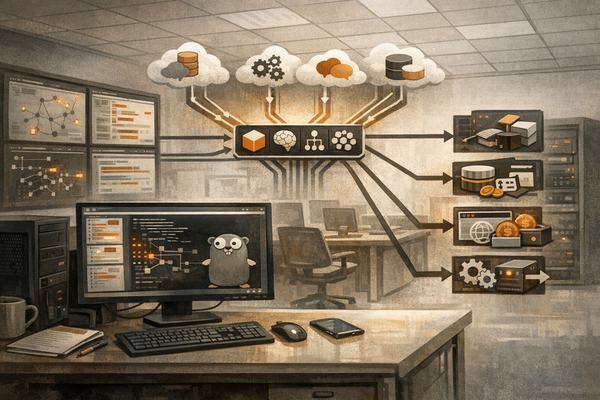
Ai Threat Intel Analysis CLOSEDQUORUM and the Rise of Autonomous AI Malware Cisco Talos analyzes CLOSEDQUORUM, a Windows implant that delegates tactical decisions to multiple commercial LLMs instead of a conventional C2 server.
Ai Threat Intel Analysis PAYLOAD ransomware turns Active Directory into an attack tool Kaspersky’s analysis shows how PAYLOAD used trusted Active Directory Group Policy to disrupt a manufacturing environment without Windows encryption.
Ai Threat Intel Analysis Atomic macOS Stealer: How Deceptive Setup Guides Deliver AMOS Palo Alto Unit 42’s lab analysis shows how deceptive macOS setup instructions deliver AMOS, harvest sensitive data, and establish persistence.
Ai Threat Intel Analysis AWS AgentCore Harness: When Prompt Injection Reaches Credentials Unit 42’s testing shows how default AgentCore Harness tools can turn prompt injection into credential exposure, with practical controls for AWS operators.
Ai Threat Intel Analysis Japanese Ransomware Activity: The Gentlemen and Qilin Cisco Talos examines ransomware activity affecting Japan, including The Gentlemen’s intrusion workflow and Qilin’s possible use of AI-assisted tooling.